 Recover MCU ATtiny88V Software
 October 26th, 2010 |
 Author:
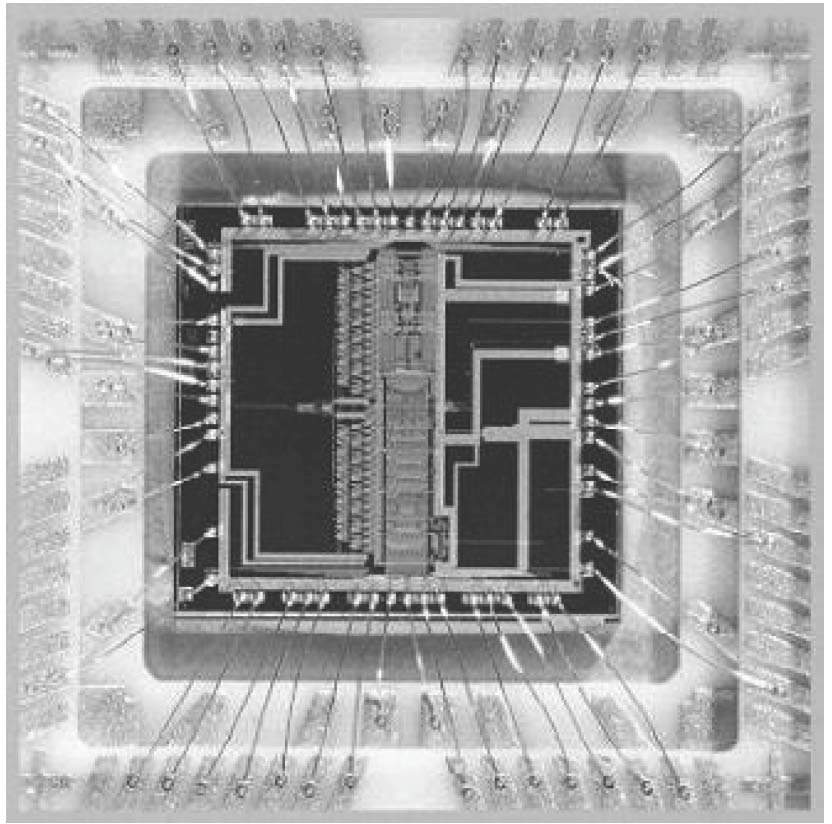
Recover MCU ATtiny88V Software and make the firmware cloning from master attiny88v which will provide the same functions, program from attiny88v memory will be readout by programmer;
The Stack is mainly used for storing temporary data, for storing local variables and for storing return addresses after interrupts and subroutine calls. The Stack Pointer Register always points to the top of the Stack. Note that the Stack is implemented as growing from higher memory locations to lower memory locations when Recover Mcu pic16f628 firmware.
This implies that a Stack PUSH command decreases the Stack Pointer. The Stack Pointer points to the data SRAM Stack area where the Subroutine and Interrupt Stacks are located. This Stack space in the data SRAM must be defined by the program before any subroutine calls are executed or interrupts are enabled.
The Stack Pointer must be set to point above 0x0200. The initial value of the stack pointer is the last address of the internal SRAM. The Stack Pointer is decremented by one when data is pushed onto the Stack with the PUSH instruction, and it is decremented by three when the return address is pushed onto the Stack with subroutine call or interrupt.
The Stack Pointer is incremented by one when data is popped from the Stack with the POP instruction, and it is incremented by three when data is popped from the Stack with return from subroutine RET or return from interrupt RETI after break pic12hv615 Mcu.
The AVR Stack Pointer is implemented as two 8-bit registers in the I/O space. The number of bits actually used is implementation dependent. Note that the data space in some implementations of the AVR architecture is so small that only SPL is needed.
In this case, the SPH Register will not be present. This section describes the general access timing concepts for instruction execution. The AVR CPU is driven by the CPU clock clkCPU, directly generated from the selected clock source for the chip. No internal clock division is used.
Figure 9 shows the parallel instruction fetches and instruction executions enabled by the Harvard architecture and the fast-access Register File concept. This is the basic pipelining concept to obtain up to 1 MIPS per MHz with the corresponding unique results for functions per cost, functions per clocks, and functions per power-unit.
The AVR provides several different interrupt sources. These interrupts and the separate Reset Vector each have a separate program vector in the program memory space. All interrupts are assigned individual enable bits which must be written logic one together with the Global Interrupt Enable bit in the Status Register in order to enable the interrupt.
Depending on the Program Counter value, interrupts may be automatically disabled when Boot Lock bits BLB02 or BLB12 are programmed. This feature improves software security.
The lowest addresses in the program memory space are by default defined as the Reset and Interrupt Vectors. The complete list of vectors is shown in “Interrupts” on page 69. The list also determines the priority levels of the different interrupts. The lower the address the higher is the priority level.
RESET has the highest priority, and next is INT0 – the External Interrupt Request 0. The Interrupt Vectors can be moved to the start of the Boot Flash section by setting the IVSEL bit in the MCU Control Register (MCUCR).
Refer to “Interrupts” on page 69 for more information. The Reset Vector can also be moved to the start of the Boot Flash section by programming the BOOTRST Fuse. When an interrupt occurs, the Global Interrupt Enable I-bit is cleared and all interrupts are disabled.
The user software can write logic one to the I-bit to enable nested inter rupts. All enabled interrupts can then interrupt the current interrupt routine. The I-bit is automatically set when a Return from Interrupt instruction – RETI – is executed.
 Posted in Recover Chip |
 Tags: recover mcu embedded archive, recover mcu embedded binary, recover mcu embedded code, recover mcu embedded content, recover mcu embedded data, recover mcu embedded eeprom, recover mcu embedded file, recover mcu embedded firmware, recover mcu embedded heximal, recover mcu embedded information, recover mcu embedded memory, recover mcu embedded program |
 Comments Closed
ATtiny88: Page Boundaries and the Partial Write Fingerprint
A flash page is the unit of both erasure and programming. The controller erases the page, the code fills a buffer with the words that belong there, and a commit transfers the buffer into the array. Power lost between the erase and the commit leaves a page of nothing. Power lost during the fill leaves a page that is part data and part erased.
On a large array those artefacts are needles. On an array this small they are conspicuous, because there are few enough pages that each one can be examined individually.
The three artefacts and what each means
| Appearance | Mechanism | Reading |
|---|---|---|
Whole page of FF |
Erased, never committed | An interruption, or a build that does not fill the array |
Partial page, then FF |
Committed before the buffer was full | An update interrupted mid-page |
| Page with a single anomalous word | Read margin, not content | Re-read at a lower clock |
The second row is the informative one, because the position of the boundary within the page is a measure of progress. If the update was interrupted after filling three quarters of a page, three quarters of that page holds new data and the rest holds the erased state.
That is a narrow but real forensic result: it establishes not only that an update failed, but approximately where.
Why this differs from a large part
On a device with a quarter megabyte of flash, one partial page among thousands is invisible unless you are looking for it. On a device with a few kilobytes, every page is a candidate for individual inspection, and the pattern across pages becomes legible.
Two patterns are worth knowing:
A run of FF pages starting at a clean boundary. The build is smaller than the array, or the application ends and a reserved region begins. Normal.
A run starting mid-page. The array was being written and something stopped it. Not normal, and worth investigating because the device may still be running code that was never fully written.
The distinction is the boundary alignment, and it costs one pass over the page map to establish.
What a small array implies about the program
A few kilobytes of flash with a page granularity of a few dozen bytes means a program of a few hundred instructions. There is no room for abstraction: no runtime library to speak of, no layered drivers, no dynamic dispatch.
What there is instead is directness. The code writes to registers, waits for flags, and moves on. On a device this size, the disassembly reads like the schematic it implements, which makes the analysis tractable in an afternoon rather than a week.
That is not a limitation of the method. It is a property of the artefact: a small program has fewer ways to hide.
Reading it
- Signature, fuses, lock byte. Clock configuration first, because a part waiting for a crystal does not answer.
- Full array read, page by page, each page twice.
- Build a page map: for each page, the number of non-
FFwords. - Identify boundary discontinuities in that map.
- Disassemble from the vector table and follow the reset path.
Step 3 is the one that is cheap here and expensive elsewhere. On a few kilobytes, a page map is a small table and it makes the structure of the image visible instantly: where code ends, whether there is a gap, and whether the gap is aligned.
The protection layer, briefly
Two lock bits, four states, one erase. No boot section, no self-programming. The array is readable or it is not, and the only thing that changes the answer destroys the content.
Because the array is small, the erase is fast and the temptation to “just erase and start over” is stronger than it should be. That instinct costs the content, and the content is the only reason the device is on the bench.
Related notes
- ATtiny48 and the same package — the smaller array in the identical footprint.
- ATtiny48A and revision workarounds — reading the code for silicon history.
- ATmega644 and page buffers — the same mechanism described at scale.
FAQ
Does a page of FF mean the chip is damaged? No. It means an erased page with nothing committed to it.
Can the position within a page be interpreted? Yes, as progress through the buffer at the moment of interruption.
Is a partial page still executable? The remainder is FF, which is an invalid instruction. Execution reaching it will not do what the source intended.
Why build a page map? Because it makes the image’s structure visible in one table, which is the fastest route to understanding an unfamiliar device.
Conclusion
Page granularity is the mechanism, and a small array makes its fingerprints legible. A page map plus boundary alignment distinguishes a small build from a failed update, and on a device this size the distinction is established in one pass instead of argued about.
Posted in Break IC |
Tags: attack ATtiny88 mcu, break attiny88 mcu, crack ATtiny88 mcu, hack ATtiny88 mcu |
Comments Closed
ATtiny48A: Workarounds Are a Record of What Changed
Silicon revisions are documented unevenly. Some arrive with a change list and a revised errata; others arrive with a new suffix and nothing else. In both cases the firmware often documents the change better than the vendor did, because whoever wrote it had to work around the problem.
Reading an image for workarounds is therefore a way of reading the die’s history. Three patterns recur, and each points at a different kind of defect.
Pattern one: the redundant write
A register is written twice with the same value, with nothing in between that could have changed it. On a modern compiler that is not an optimisation failure — it is an instruction to the hardware, usually because the first write did not take effect reliably.
The distance between the two writes is informative. A few cycles apart suggests a synchroniser that needed time. A separate function suggests the workaround was applied at a call site rather than at the driver.
Pattern two: the delay that does nothing useful
A loop with no side effects, sitting between two register operations. Delay loops exist for legitimate reasons — start-up time, analogue settling, protocol spacing — and they also exist because a peripheral needed longer than the datasheet said.
Distinguishing the two requires context. A delay after enabling an oscillator is legitimate. A delay after writing a control register that has no start-up requirement is a workaround, and it names the peripheral that misbehaved.
Pattern three: reading a status bit twice
The code polls a flag, sees it set, and polls again before acting. That pattern appears in firmware written against a part where the flag was known to glitch, and it is close to conclusive evidence of a silicon defect in that path.
| Pattern | Likely cause | What it names |
|---|---|---|
| Duplicate register write | Write did not take | That peripheral |
| Unexplained delay loop | Operation slower than specified | Whatever the delay precedes |
| Double status poll | Flag unreliable | Whatever the flag reports |
| Value written then masked | Register reserved bits behave unexpectedly | Register-level behaviour |
The fourth row is subtler and shows up in code that writes a value, then immediately rewrites it with a mask applied. That is a response to reserved bits that do not read back as written.
Why this matters for a reproduction
A reconstruction that strips the workarounds produces code that is cleaner and, on the original die, wrong. It will fail intermittently, and the failure will appear in exactly the place the workaround was protecting.
Keeping them has the opposite cost: on a newer die they are harmless but they obscure the logic. The right answer is to keep them and annotate them, so that a later reader knows which parts of the code are the design and which are the design’s response to a defect.
Annotation is the part that gets skipped. An image with comments like “this delay is for the errata” is worth considerably more than the same image without them, and the cost of adding them is minutes.
What the revision changes at the observable level
Three things are visible without any errata:
The signature byte may differ. The fuse map does not. The lock bit state machine does not.
That combination means the recovery procedure is identical and only the interpretation changes, which is the useful split: method is portable across revisions, timing and thresholds are not.
Reading order for a revision-aware reconstruction
- Read signature and record it with the date code from the package.
- Read fuses and lock byte.
- Read the array, verified.
- Locate the three workaround patterns in the code.
- For each, record what it protects and which peripheral it names.
Step 5 produces something unusual and valuable: a per-peripheral list of suspected silicon quirks, derived from the firmware rather than from documentation. For anyone maintaining a product across a revision change, that list is the practical answer to “what do we have to be careful about”.
Related notes
- ATtiny48 and the wide package — the same die in its base revision.
- ATtiny88A and the program layout — the larger array with the same revision question.
- ATmega644A and revision footprints — the same analysis on a larger die.
FAQ
Can workarounds be identified without symbols? Yes. They are structural patterns, and they do not depend on names.
Should workarounds be removed from a reconstruction? No. Annotate them instead. Removing one that is still needed creates an intermittent fault.
Does the A revision change the lock bits? No. The state machine is stable across the family.
Is a duplicated register write always a workaround? Not always. It can be a compiler artefact from a volatile access. Context decides.
Conclusion
A revision leaves two records: the vendor’s, which may be terse, and the firmware’s, which is detailed and specific. Reading the second is a matter of recognising three patterns and asking what each one protects. Doing so turns an image into a change log for the silicon it was written against.
Posted in Break IC |
Tags: attack attiny48a mcu, crack mcu attiny48a, hack attiny48a mcu |
Comments Closed
Copy Microcontroller PIC16F639 Heximal
Copy Microcontroller PIC16F639 Heximal needs to extract the flash program from microprocessor PIC16F639 and then crack microcontroller pic16f639 security fuse bit;
A single comparator is shown in Figure 6-1, along with the relationship between the analog input levels and the digital output. When the analog input at VIN+ is less than the analog input VIN-, the output of the comparator is a digital low level. When the analog input at VIN+ is greater than the analog input VIN-, the output of the comparator is a digital high level. The shaded areas of the output of the comparator in Figure 6-1 represent the uncertainty due to input offsets and response time.
The polarity of the comparator output can be inverted by setting the CINV bit (CMCON<4>). Clearing CINV results in a non-inverted output. A complete table showing the output state versus input conditions and VIN-the polarity bit.
There are eight modes of operation for the comparator. The CMCON register, shown in Register 6-1, is used to select the mode. Figure 6-2 shows the eight possible modes. The TRISA register controls the data direction of the comparator pins for each mode.
If the Comparator mode is changed, the comparator output
The CMCON register, shown in Register 6-1, is used to select the mode. Figure 6-2 shows the eight possible modes. The TRISA register controls the data direction of the comparator pins for each mode.
A simplified circuit for an analog input is shown in Figure 6-3. Since the analog pins are connected to a digital output, they have reverse biased diodes to VDD and VSS. The analog input, therefore, must be between VSS and VDD. If the input voltage deviates from this libri the polarity bit.
Response time is the minimum time, after selecting a new reference voltage or input source, before the comparator output is ensured to have a valid level. If the internal reference is changed, the maximum delay of the internal voltage reference must be considered when using the comparator outputs. Otherwise, the maximum delay of the comparators should be used H-CN;
Posted in Reverse Engineer Microcontroller |
Tags: copy microcontroller source bin, copy microcontroller source content, copy microcontroller source data, copy microcontroller source file, copy microcontroller source flash, copy microcontroller source hex, copy microcontroller source software |
Comments Closed
ATmega128A: EEPROM Endurance and the Pages That Wear Out
Flash and EEPROM are both non-volatile and both wear out. They differ in how fast, and the difference matters when a device arrives with data that looks damaged: it may not be damaged, it may be worn.
An EEPROM byte tolerates a large but finite number of write cycles. A product that updates a counter every few seconds will exhaust that budget within its service life, and a product that updates the same byte every second will exhaust it quickly.
The mechanism
Writing an EEPROM cell moves charge through a thin oxide. Each write degrades the oxide slightly. Enough writes and the cell no longer holds its state reliably: it reads as the erased value, or reads inconsistently between passes.
Two properties make this different from random corruption:
It is localised. Wear happens where writes happen. A log record at a fixed address wears that address out while the rest of the array is untouched.
It is predictable. Given the write rate and the endurance figure, the failure point is arithmetic, not chance.
That combination is useful diagnostically: a device whose damage is concentrated in a small, repeatedly-written region is showing wear, not damage.
Where wear appears
| Pattern in the EEPROM | Likely cause |
|---|---|
| One byte stuck at the erased value | That byte exhausted |
| A fixed-width record blank at one offset | Fixed-address logging |
| Damage spread evenly across a region | Rotating log, uneven rotation |
| Whole array blank | Erased, or never written |
The second and third rows are the interesting pair. They distinguish a naive design from a considered one: a firmware that writes a record at the same offset every time has no rotation, and a firmware that rotates has spread the wear.
Reading the image tells you which, and that is a statement about the design’s quality as well as its history.
How firmware mitigates it
Wear levelling, in its simplest form, is a cursor: the firmware keeps a write index in a header and appends records cyclically, so consecutive writes land in different cells. More elaborate schemes track per-block counters.
Both leave traces in the code:
- An index variable that wraps at a limit.
- A header structure with a generation counter.
- Code that scans for the most recent valid record at start-up.
The third is the clearest signal. A start-up scan through records looking for the newest valid one is a ring buffer in EEPROM, and it means the design anticipated wear.
Why this matters for reading a worn device
A worn byte does not announce itself. It reads as a value, and if that value is plausible the reader accepts it. The check that reveals wear is reading the array twice and comparing, plus looking for a region whose values are systematically at one extreme.
Isolated bytes that read as FF in an otherwise populated record are the classic signature. They are not erased — the page was written — they are exhausted.
Distinguishing that from an intentional blank requires knowing what the firmware expects to write there, which comes from reading the code rather than the data.
The reading order, with wear in mind
- Signature, fuses, lock byte.
- EEPROM read, before any operation that could erase it. Record EESAVE.
- EEPROM read again, comparing byte for byte.
- Identify repeated-write regions by structure: fixed width, cyclical content.
- Correlate with the firmware’s logging code.
Step 5 is where a data anomaly becomes an explanation. A record blank at one offset, in a firmware that writes to that offset every cycle, is wear — and that is a conclusion no amount of staring at the bytes will produce.
Related notes
- ATmega128P and binary layout — the other array on the same die.
- ATmega1280P and EESAVE — surviving through an erase.
- ATmega32PA and EEPROM survival — the fuse that decides it.
FAQ
How many writes can an EEPROM byte take? A large but finite number, given in the datasheet. Frequent logging can exhaust it within a product’s life.
Can worn cells be recovered? The value is gone. What can be recovered is the pattern and the design that produced it.
Is wear visible in a single read? Partly. A second read exposes cells whose state is no longer stable.
Does reading wear the array? No. Only writes do.
Conclusion
Wear is localised, predictable, and often mistaken for corruption. Concentrated damage in a repeatedly-written region, isolated bytes at one extreme, and a firmware that logs to a fixed offset together describe an exhausted page rather than a broken device — and the code, not the data, is what makes that attribution possible.
Reverse Engineering Microcontroller ATmega16PA Heximal
Reverse Engineering Microcontroller ATmega16PA to locate the security fuse bit of mcu atmega16pa, crack mcu atmega16pa fuse bit and readout embedded Heximal from mcu atmega16pa eeprom and flash memory;
First Analog Comparator conversion may be delayed, If the device is powered by a slow rising VCC, the first Analog Comparator conversion will take longer than expected on some devices.
Problem Fix/Workaround
When the device has been powered or reset, disable then enable the Analog Comparator before the first conversion.
Interrupts may be lost when writing the timer registers in the asynchronous timer, The interrupt will be lost if a timer register that is synchronized to the asynchronous timer clock is written when the asynchronous Timer/Counter register (TCNTx) is 0x00.
Problem Fix / Workaround
Always check that the asynchronous Timer/Counter register neither have the value 0xFF nor 0x00 before writing to the asynchronous Timer Control Register (TCCRx), asynchronous Timer Counter Register(TCNTx), or asynchronous Output Compare Register (OCRx).
IDCODE masks data from TDI input
The JTAG instruction IDCODE is not working correctly. Data to succeeding devices are replaced by all-ones during Update-DR.
Problem Fix / Workaround
If ATmega16 is the only device in the scan chain, the problem is not visible. Select the Device ID Register of the ATmega16 by issuing the IDCODE instruction or by entering the Test-Logic-Reset state of the TAP controller to reverse engineering out the contents of its Device ID Register and possibly data from succeeding devices of the scan chain. Issue the BYPASS instruction to the ATmega16.
Registers of preceding devices of the boundary scan chain.
If the Device IDs of all devices in the boundary scan chain must be captured simultaneously, the ATmega16 must be the fist device in the chain.
Reverse engineeringing EEPROM by using ST or STS to set EERE bit triggers unexpected interrupt request.
Reverse engineeringing EEPROM by using the ST or STS command to set the EERE bit in the EECR register triggers an unexpected EEPROM interrupt request.
Problem Fix / Workaround
Always use OUT or SBI to set EERE in EECR.
First Analog Comparator conversion may be delayed
If the device is powered by a slow rising VCC, the first Analog Comparator conversion will take longer than expected on some devices.
Problem Fix/Workaround
When the device has been powered or reset, disable then enable the Analog Comparator before the first conversion.
Interrupts may be lost when writing the timer registers in the asynchronous timer
The interrupt will be lost if a timer register that is synchronized to the asynchronous timer clock is written when the asynchronous Timer/Counter register(TCNTx) is 0x00.
Problem Fix / Workaround
Always check that the asynchronous Timer/Counter register neither have the value 0xFF nor 0x00 before writing to the asynchronous Timer Control Register(TCCRx), asynchronous Timer Counter Register(TCNTx), or asynchronous Output Compare Register(OCRx).
IDCODE masks data from TDI input
The JTAG instruction IDCODE is not working correctly. Data to succeeding devices are replaced by all-ones during Update-DR.
Problem Fix / Workaround
If ATmega16 is the only device in the scan chain, the problem is not visible.
Select the Device ID Register of the ATmega16 by issuing the IDCODE instruction or by entering the Test-Logic-Reset state of the TAP controller to reverse engineering out the contents of its Device ID Register and possibly data from succeeding devices of the scan chain. Issue the BYPASS instruction to the ATmega16 while reverse engineeringing the Device ID
Registers of preceding devices of the boundary scan chain. If the Device IDs of all devices in the boundary scan chain must be captured.
Posted in Recover Chip |
Tags: reverse engineering microcontroller embedded archive, reverse engineering microcontroller embedded bin, reverse engineering microcontroller embedded code, reverse engineering microcontroller embedded content, reverse engineering microcontroller embedded data, reverse engineering microcontroller embedded eeprom, reverse engineering microcontroller embedded file, reverse engineering microcontroller embedded firmware, reverse engineering microcontroller embedded hex, reverse engineering microcontroller embedded information, reverse engineering microcontroller embedded memory, reverse engineering microcontroller embedded program |
Comments Closed
ATtiny48V: What the V Suffix Costs You, and What the Lock Bits Actually Do
The ATtiny48V is a 28-pin tinyAVR with 4 KB of flash, 256 bytes of SRAM, 64 bytes of EEPROM, 24 general-purpose I/O pins, an 8-bit and a 16-bit timer, SPI, TWI and a six-channel 10-bit ADC. It shares its pinout with the ATmega48 family, which is the reason it appears in designs that were laid out for a larger part and then cost-reduced.
The V suffix is the part that usually gets skipped over in discussion. It is not a package or temperature variant. It is a lower voltage range — 1.8 V to 5.5 V instead of 2.7 V to 5.5 V — and it comes with a lower maximum clock frequency. That single trade has more effect on whether a recovered binary behaves identically than the lock bits do.
What the ATtiny48V actually contains
| Item | ATtiny48V |
|---|---|
| Core | 8-bit AVR |
| Flash | 4 KB (2048 × 16) |
| SRAM | 256 bytes |
| EEPROM | 64 bytes |
| I/O pins | 24 (PORTA, PORTB, PORTC, PORTD) |
| Timers | 1 × 8-bit, 1 × 16-bit |
| Serial | SPI, TWI (I²C) |
| A/D converter | 6 channels, 10-bit |
| Operating voltage | 1.8–5.5 V |
| Max clock at 1.8 V | 4 MHz |
| Max clock at 4.5 V | 12 MHz |
| Packages | 28-pin PDIP, 32-pin TQFP, 32-pin MLF |
| Programming | ISP over SPI, high-voltage parallel |
The frequency table is the part to read twice. Speed grade is a function of supply voltage on these parts, not a fixed number: at 1.8 V the core is limited to 4 MHz, at 2.7 V to 8 MHz, at 4.5 V to 12 MHz. A design using the ATtiny48V at 3.3 V is a design running at 8 MHz or below, whatever the crystal says.
Why the clock ceiling is a recovery constraint
Flash contents describe what the firmware does. They do not describe how fast it does it. On an AVR, the relationship between the two is fixed by a small number of values that live outside flash:
- The clock source, set by the low fuse byte: internal 8 MHz RC, internal 128 kHz RC, external crystal, or external clock.
- The CKDIV8 bit, which divides whatever that source produces by eight.
- The timer prescaler registers, written at runtime.
A binary recovered from an ATtiny48V that ran at 8 MHz and reflashed into a device configured for the internal 128 kHz oscillator will execute the same instructions and produce completely different timing. Delay loops become 62 times longer, software PWM frequencies collapse, and any protocol with a bit-time budget stops working. This is not a subtle failure — it is total — and it is caused by a fuse byte, not by the flash.
The 64-byte EEPROM raises the same point in a different form. It is small enough that many designs skip it entirely and put configuration in flash, but where it is used it typically holds exactly the values that are easiest to lose: an offset correction, a node address, a run-hour counter. Sixty-four bytes that are absent from a recovered image produce a device that boots, runs, and reports the wrong numbers.
Lock bits and the erase that clears them
The ATtiny48 uses the standard AVR two-bit lock field with inverted polarity.
| Mode | LB1 | LB0 | Effect |
|---|---|---|---|
| 1 | 1 | 1 | No memory lock |
| 2 | 0 | 1 | Further programming of flash and EEPROM disabled; verification allowed |
| 3 | 0 | 0 | Further programming and verification disabled |
The distinction that matters in the field is between modes 2 and 3. Mode 2 leaves the verify path open, which is what a manufacturer wants when the device has to be tested after programming but must not be changed. Mode 3 closes both.
Both modes are subject to the same rule:
The chip erase operation erases the flash and EEPROM arrays and resets the lock bits.
On AVR parts the lock bits are stored in the same non-volatile array as the data they protect, so there is no sequence in which they are cleared independently. The erase clears the bits and the memory at once. This is a structural property of the family, and it means that the state of the lock bits in a device taken off a board is informative about how the part was manufactured and uninformative about how to read it.
The self-programming path
The ATtiny48 supports self-programming: the application can write to its own flash through the SPM instruction, using the RWW and SPM control registers. On a 4 KB part with no separate boot section, that means the application itself contains any routine that modifies flash.
Two practical notes follow. First, flash-write routines are the easiest thing in a recovered image to identify, because SPM requires a fixed four-instruction sequence that cannot be rearranged: write the address low byte, the address high byte, the data low byte, the data high byte, in that order, before executing SPM. Nothing else in a tinyAVR program looks like that.
Second, if a design uses self-programming for calibration storage, some of the constants in a recovered image may be written during operation rather than present at manufacture. A dump taken from a device that has been running for years is a dump of a device that has modified itself, and a fresh device programmed with that image is not necessarily a device in its original state. This is worth knowing before treating a recovered image as the factory firmware.
What a complete image contains
- 0000h–07FFh — 2048 × 16 bits of flash
- lock bits — LB1:LB0, in the non-volatile array
- fuse bytes — low fuse (clock source, start-up, CKDIV8), high fuse, extended fuse
- 64 bytes of EEPROM, separate address space
- calibration byte — read from the signature area at manufacture, sometimes written into flash by the application
The fuse bytes are the part that a flash-only image omits, and on a part whose speed grade is a function of supply voltage they determine more of the observable behaviour than anything in the first 4 KB.
Related notes
The non-V ATtiny48 has the same die at a 2.7 V minimum, and the ATtiny48A is the later revision of the same part number. The smaller 20-pin ATtiny45 uses the same lock bit field, and the ATtiny4313 extends the same architecture downward in pin count.
FAQ
What does the V suffix mean on an ATTINY48V? It marks the lower-voltage variant: 1.8–5.5 V rather than 2.7–5.5 V. The maximum clock frequency at low supply is correspondingly lower.
Do the lock bits survive a chip erase? No. The chip erase clears the lock bits together with the flash and EEPROM arrays, in one operation.
Is lock bit mode 2 unreadable? No. Mode 2 blocks further programming but still permits verification. Mode 3 blocks both.
Can the ATtiny48V write its own flash? Yes, through the SPM instruction. The four-instruction write sequence is distinctive and easy to locate in a recovered listing.
Does a flash dump reproduce the device’s behaviour? Only alongside the fuse bytes. Clock source and CKDIV8 set the timing base that every delay and bit-time in the firmware depends on.
Conclusion
The ATtiny48V is not a difficult part to characterise. Four kilobytes of flash, two lock bits, a small EEPROM and a fuse byte that sets the clock. The difficulty is in the last item, because it is the one that a flash-only view leaves out, and on a V-suffixed part the clock ceiling is low enough that getting it wrong changes the behaviour of every timed operation in the program.
ATtiny48: A Small Core in a Wide Package
A small flash array in a wide package is not a contradiction. It is a part chosen for its pin count rather than its memory, and the combination says something about the product: many signals, little logic, no need for a large program.
Those are also the products that are easiest to examine, because the program is small enough to read in full and the pin count makes in-circuit access practical rather than awkward.
Why the mismatch exists
Three reasons appear repeatedly.
Driving a display or a keypad. Dozens of pins, each doing something trivial. The code is a lookup table and a loop, and it fits comfortably in a few kilobytes.
Interfacing many discrete signals. A bank of sensors or relays, each on its own pin, each with a short handler. Pin count is the constraint; memory is not.
Replacing glue logic. A part that reads eight inputs, applies a small truth table, and drives eight outputs. This is the case where the program is genuinely tiny and the package is doing all the work.
In each case the flash is small because the job is small, and the package is wide because the job is parallel.
| Property | Consequence |
|---|---|
| Many pins | In-circuit programming is usually practical |
| Small array | Full read takes seconds, double-reading costs nothing |
| Wide port set | Port configuration describes the product |
| No boot section | One protection field, binary outcome |
What the small array makes easy
A full read of an array this size takes seconds. There is no reason to skip the second pass, no reason to skip page-level comparison, and no reason to accept an unverified image.
More usefully, the whole program can be read rather than sampled. On a few kilobytes, a careful reader can account for every function, and unusual constructs stand out — a hand-written delay loop sized for a specific device, a table with an obvious stride, a checksum constant that matches an external chip.
That is a different activity from analysing a large image, where the work is statistical and the conclusions are probabilistic. Here it is exhaustive, and the conclusions can be certain.
The protection model, unchanged
Nothing about the package affects the protection. Two lock bits, four states, and one erase that clears them along with the array. No boot section, no self-programming path, no second container.
That means the reasoning is short and the outcome is binary: the array is readable, or it is not, and if it is not, the only operation that changes that returns a blank part.
The only thing the wide package changes is access. With twenty-eight pins, the programming interface is much less likely to be fully consumed by other functions, and a header is more likely to exist on the board. In-circuit entry is therefore the norm rather than the exception, which is a real practical advantage over the eight-pin members.
Reading a many-pin, small-memory device
- Supply at the design rail, measured at the socket.
- Signature and fuses. With this many pins, a part configured for an external clock is common — a wide package often accompanies a design that has room for a crystal.
- Lock byte.
- Array read in pages, twice each.
- Map the port accesses: which port is initialised as input, which as output, and in what order.
Step 5 is the one that turns the image into a description of the product. On a device whose purpose is driving many signals, the port configuration is the design. It says which pins are inputs, which are outputs, which have pull-ups enabled, and which are left alone — and that is more informative than the arithmetic in between.
What the pin map tells a customer
For a device that exists to interface with the physical world, the questions are usually about the interface: what does it expect, what does it drive, what are the timing requirements.
All three are answerable from the port configuration plus the code that reads and writes those ports. The memory size stops being interesting at that point, which is the correct outcome: the product’s behaviour is the subject, not its storage.
Related notes
- ATtiny48A and revision behaviour — what changes between dies of the same name.
- ATtiny88 and page boundaries — the larger array in the same package.
- ATtiny25 and shared pins — the opposite end of the package range.
FAQ
Does a wide package mean more memory? No. Memory size and pin count are independent choices in this family.
Is in-circuit programming easier here? Generally yes, because the programming pins are less likely to be fully committed to other functions.
Does the package change the lock bit behaviour? No. The protection model is identical across packages.
Why would a design use such a large package for such a small program? Because the pin count is the requirement and the program is incidental.
Conclusion
A small core in a wide package is a deliberate trade, and it makes examination easier rather than harder. The array fits in a single reading, the pins are accessible, and the port configuration describes the product more directly than its code does. On this kind of device, the interface is the design.
Posted in Recover Chip |
Tags: recover mcu embedded archive, recover mcu embedded code, recover mcu embedded content, recover mcu embedded data, recover mcu embedded eeprom, recover mcu embedded file, recover mcu embedded firmware, recover mcu embedded information, recover mcu embedded memory, recover mcu embedded program |
Comments Closed
ATmega2561V: The Largest Member, and the Same One Fuse
Scale changes many things about a part. A quarter of a megabyte of flash needs a wider program counter, a different page count, and a read that takes long enough to expose supply behaviour that a small part hides. Scale does not change the arbitration that decides whether anything is recoverable.
That arbitration is a single fuse bit. On a part this large it is easy to imagine that the extra memory implies extra rules. It does not. The same erase, the same lock state machine, the same fuse, applied to a bigger array.
What is different at this size
Three engineering consequences, none of them about protection.
The read takes time. A quarter of a megabyte at a conservative clock is minutes, not seconds. Over that window the supply can sag, the part can warm, and a clip can lose contact. Any of those produces a file that is correct at the start and wrong later.
The address space is fully populated. Unlike a smaller member occupying a subset of the same map, this one uses all of it, so an all-FF region in the middle is meaningful rather than a marker of unimplemented memory.
The program counter is three bytes wide. Return addresses, jump targets, and table pointers all carry an extra byte, and code that manipulates the stack directly has to account for it.
What is not different
| Rule | Applies here exactly as elsewhere |
|---|---|
| Lock mode 2 or 3 blocks verification | yes |
| Chip erase is the only way to clear locks | yes |
| Chip erase erases the flash | yes |
| EEPROM survives only if EESAVE allows | yes |
| No interface bypasses the lock byte | yes |
That table is the whole protection story, and it is identical across the family from the smallest member to this one. Familiarity with a small part transfers directly, which is one of the genuine advantages of a family that shares an architecture.
The EEPROM on a part nobody expects to have one
This member has no external memory interface, so there is no external storage to look for. Its EEPROM holds the per-unit data: calibration, identity, counters. A few kilobytes, and usually the most device-specific content in the product.
Because the flash is large and the EEPROM is small, the natural focus is the code. That focus is correct for understanding the product and wrong for understanding the unit. A device that measures or controls something external almost always carries constants in EEPROM that the code reads at start-up; without them, a faithful reproduction still measures wrong.
The fuse that decides whether those constants survive an erase is the same fuse as on every other member. Set for operational reasons — so a firmware update does not wipe calibration — and set more often than not.
Reading a large array reliably
The risks scale with the read time, so the procedure has to as well:
- Supply at the design rail, measured at the socket, with local decoupling.
- Signature, fuses, lock byte — before anything else.
- One page read twice, compared. Establishes margin.
- Full read in passes, verifying each page as it arrives; log any page that fails.
- Re-read the first page at the end and compare with step 3.
Step 5 is the one that catches drift over the duration of the read. It costs one page and it is the only check that covers the whole session rather than one page.
A page that fails verification in step 4 is not a page to average or to accept. It is a page to re-read at lower clock, or at higher supply, until two consecutive reads agree. If they never agree, the die has a marginal region and that fact belongs in the report.
Working out what you have
An all-FF block in the middle of a full-map part is informative. Three explanations, in order of likelihood: the application does not fill its allowance, an update left a gap, or a page failed to program.
The distinction matters for reproduction. A gap from an incomplete build is reproducible as-is; a gap from a failed program will not be, because the device is running code that was never fully written and its behaviour may depend on what the missing page should have contained.
Comparing the gap boundaries against page alignment settles it. A gap that starts and ends on page boundaries is structural. A gap that starts partway through a page came from an interrupted operation.
Related notes
- ATmega1280PV and the three-byte counter — the same counter on a smaller array.
- ATmega1281PV and reconstruction — the other bus-less member.
- ATmega32PA and EESAVE — the fuse’s mechanism explained from the array side.
FAQ
Does a larger flash mean stronger protection? No. The lock bit mechanism is identical. Extra memory is not extra security.
How long does a full read take? Minutes at a conservative clock. Reducing the clock for reliability is almost always the right trade.
Can the EEPROM be read while the part is locked? No. The read commands are refused in lock mode 2 or 3, which is why the erase and its one surviving array matter.
Is a gap in the middle of the image a problem? It is information. Page-aligned gaps are structural; unaligned ones record a failure.
Conclusion
Size is an engineering detail; protection is an architectural constant. This part’s quarter megabyte changes the read time, the pointer width, and the interpretation of empty regions, and it changes nothing about how a locked device is opened or what survives. Reading the fuse byte first answers the only question that cannot be answered later.
Posted in Reverse Engineer Microcontroller |
Tags: recover mcu embedded archive, recover mcu embedded bin, recover mcu embedded code, recover mcu embedded content, recover mcu embedded data, recover mcu embedded eeprom, recover mcu embedded file, recover mcu embedded firmware, recover mcu embedded hex, recover mcu embedded information, recover mcu embedded memory, recover mcu embedded program |
Comments Closed
Break IC ATmega2561 Program
Break IC ATmega2561 and copy mcu atmega2561 Program from its flash memory, the security fuse bit of the microcontroller atmega2561 will be unlocked after the process;
The device is manufactured using Atmel’s high-density nonvolatile memory technology. The On-chip ISP Flash allows the program memory to be reprogrammed in-system through an SPI serial interface, by a conventional nonvolatile memory programmer, or by an On-chip Boot program running on the AVR core.
The boot program can use any interface to download the application program in the application Flash memory. Software in the Boot Flash section will continue to run while the Application Flash section is updated, providing true Read-While-Write operation if Break microcontroller pic16c65b eeprom.
By combining an 8-bit RISC CPU with In-System Self-Program mable Flash on a monolithic ch ip, the Atmel ATmega2561 is a powerful microcontroller that provides a highly flexible and cost effective solution to many embedded control applications.
The ATmega2561 AVR is supported with a full suite of program and system development tools including: C compilers, macro assemblers, program debugger/simulators, in-circuit emulators, and evaluation kits after recover mcu pic16f687 software.
Each device in the ATmeg2561 family differs only in memory size and number of pins. Table 1 summarizes the different configurations for the six devices.
Port A is an 8-bit bi-directional I/O port with internal pull-up resistors (selected for each bit). The Port A output buffers have symmetrical drive characteristics with both high sink and source capability. As inputs, Port A pins that are externally pulled low will source current if the pull-up resistors are activated when copy microcontroller pic16f677 code.
The Port A pins are tri-stated when a reset condition becomes active, even if the clock is not running. Port B is an 8-bit bi-directional I/O port with internal pull-up resistors (selected for each bit). The Port B output buffers have symmetrical drive characteristics with both high sink and source capability. As inputs, Port B pins that are externally pulled low will source current if the pull-up resistors are activated.
The Port B pins are tri-stated when a reset condition becomes active, even if the clock is not running. Port C is an 8-bit bi-directional I/O port with internal pull-up resistors (selected for each bit). The Port C output buffers have symmetrical drive characteristics with both high sink and source capability.
As inputs, Port C pins that are externally pulled low will source current if the pull-up resistors are activated. The Port C pins are tri-stated when a reset condition becomes active, even if the clock is not running.