 Attack MCU PIC16CE625 Program
 April 25th, 2014 |
 Author:
How to Attack MCU PIC16CE625 Program and Dump Protected Firmware
Microchip’s PIC16CE625 is a popular 8-bit microcontroller frequently used in embedded applications due to its reliability and low power consumption. However, when its program memory is locked, encrypted, or protected, accessing the embedded firmware becomes a challenge—especially for engineers, analysts, or developers who need to clone, restore, or modify the system. At [Your Company Name], we specialize in attacking the MCU PIC16CE625 program to help clients unlock, decrypt, and extract its secured binary or heximal firmware.
Nuestro procedimiento para atacar la protección del MCU PIC16CE625 Análisis inicial: Comenzamos inspeccionando el chip objetivo con lupa y probando la instrumentación para identificar esquemas de protección y posibles puertas traseras. Conexión de la interfaz: Mediante técnicas de sondeo precisas, establecemos acceso físico a la memoria flash o EEPROM, a menudo mediante la interfaz directa de pines o el acceso a la traza de la PCB. Protección de bypass: Nuestro servicio se centra en explotar las vulnerabilidades conocidas en los mecanismos de protección de código del PIC16CE625. Dependiendo de la configuración, esto puede implicar fallos de alimentación, manipulación del reloj o microsondeo para desbloquear la memoria bloqueada. Volcado de firmware: Una vez evadida la protección, realizamos un volcado completo del archivo de firmware (incluyendo flash, EEPROM y bits de configuración) a un formato binario o hexadecimal legible.
Our Procedure to Attack PIC16CE625 MCU Protection
-
Initial Analysis: We begin by inspecting the target chip under magnification and test instrumentation to identify protection schemes and potential backdoors.
-
Interface Connection: Using precise probing techniques, we establish physical access to the flash or EEPROM memory, often through direct pin interfacing or PCB trace access.
-
Bypass Protection: The core of our service focuses on exploiting known vulnerabilities in the PIC16CE625’s code protection mechanisms. Depending on the configuration, this may involve power glitching, clock manipulation, or microprobing to crack the locked memory.
-
Firmware Dumping: Once protection is bypassed, we perform a full dump of the firmware archive—including flash, EEPROM, and configuration bits—into a readable binary or heximal format.
-
Reverse Engineering (Optional): We can optionally decode, decompile, or convert the dumped memory into C/C++ source code, enabling clients to review or reuse the logic for debugging, porting, or enhancement.
-
Verification & Delivery: The extracted program data is verified for integrity and then delivered to the client in the required format (e.g., binary file, Intel HEX, or disassembled source code).
Нашата процедура за атакуване на защитата на MCU PIC16CE625 Първоначален анализ: Започваме с проверка на целевия чип под увеличение и тестваме инструменти, за да идентифицираме схеми за защита и потенциални задни врати. Интерфейсна връзка: Използвайки прецизни техники за сондиране, ние установяваме физически достъп до флаш или EEPROM паметта, често чрез директно свързване на пинове или достъп до PCB трасиране. Защита от заобикаляне: Основата на нашата услуга е използването на известни уязвимости в механизмите за защита на кода на PIC16CE625. В зависимост от конфигурацията, това може да включва прекъсване на захранването, манипулиране на тактовата честота или микросондиране за разбиване на заключената памет. Дъмпинг на фърмуера: След като защитата бъде заобиколена, ние извършваме пълен дъмп на фърмуерния архив – включително флаш паметта, EEPROM и конфигурационните битове – в четлив двоичен или шестнадесетичен формат.
Services We Offer
We provide a complete solution to copy, clone, or duplicate the protected firmware of PIC16CE625 microcontrollers. Our techniques help clients overcome vendor lock-in, recover lost firmware, or analyze device behavior. All services are conducted with strict confidentiality and professionalism.
Whether you need to hack a legacy device, restore a lost firmware file, or unlock a secured embedded program, our experts can help you access the internal logic of the PIC16CE625 MCU.
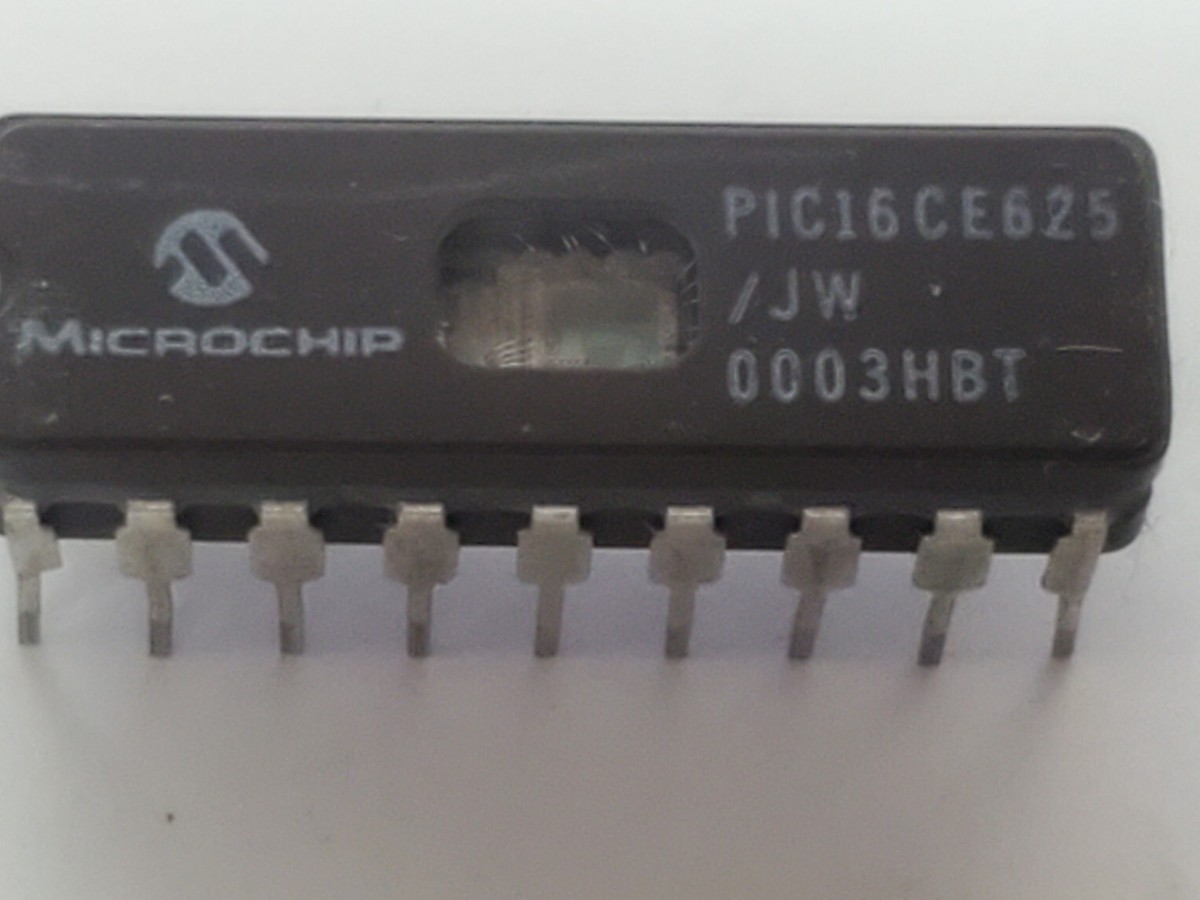
Attack MCU PIC16CE625 locked memory and extract program from Microcontroller PIC16CE625 flash memory, disable the security fuse bit after crack Microprocessor PIC16CE625 so the microprobes will be able to get access to the internal memory
Attack MCU PIC16CE625 locked memory and extract program from Microcontroller PIC16CE625 flash memory, disable the security fuse bit after crack Microprocessor PIC16CE625 so the microprobes will be able to get access to the internal memory;
Interrupt capability 16 special function hardware registers
8-level deep hardware stack
Direct, Indirect and Relative addressing modes
Peripheral Features:
· 13 I/O pins with individual direction control
· High current sink/source for direct LED drive
· Analog comparator module with:
– Two analog comparators
– Programmable on-chip voltage reference (VREF) module
– Programmable input multiplexing from device inputs and internal voltage reference
– Comparator outputs can be output signals
· Timer0: 8-bit timer/counter with 8-bit programmable prescaler
Special Microcontroller Features:
· In-Circuit Serial Programming (ICSP™) (via two pins)
· Power-on Reset (POR)
· Power-up Timer (PWRT) and Oscillator Start-up Timer (OST)
· Brown-out Reset
· Watchdog Timer (WDT) with its own on-chip RC oscillator for reliable operation
PIC16CE625 MCU Korumasına Saldırma Prosedürümüz İlk Analiz: Hedef çipi büyütme altında inceleyerek ve koruma şemalarını ve olası arka kapıları belirlemek için enstrümantasyonu test ederek başlıyoruz. Arayüz Bağlantısı: Hassas sondaj teknikleri kullanarak, genellikle doğrudan pin arayüzü veya PCB iz erişimi yoluyla flaş veya EEPROM belleğine fiziksel erişim sağlıyoruz. Baypas Koruması: Hizmetimizin özü, PIC16CE625’in kod koruma mekanizmalarındaki bilinen güvenlik açıklarından yararlanmaya odaklanır. Yapılandırmaya bağlı olarak, bu, kilitli belleği kırmak için güç arızası, saat manipülasyonu veya mikro sondaj içerebilir. Ürün Yazılımı Dökümü: Koruma atlatıldıktan sonra, flaş, EEPROM ve yapılandırma bitleri dahil olmak üzere ürün yazılımı arşivinin tam bir dökümünü okunabilir bir ikili veya altıgen biçime dönüştürüyoruz. Tersine Mühendislik (İsteğe Bağlı): İsteğe bağlı olarak, dökülen belleği kod çözebilir, derleyebilir veya C/C++ kaynak koduna dönüştürebiliriz; böylece istemcilerin hata ayıklama, taşıma veya geliştirme için mantığı gözden geçirmesini veya yeniden kullanmasını sağlayabiliriz.
Special Microcontroller Features (cont’d)
· 1,000,000 erase/write cycle EEPROM data memory
· EEPROM data retention > 40 years
· Programmable code protection
· Power saving SLEEP mode
· Selectable oscillator options
· Four user programmable ID locations
CMOS Technology:
· Low-power, high-speed CMOS EPROM/EEPROM technology
· Fully static design
· Wide operating voltage range – 2.5V to 5.5V
· Commercial, industrial and extended temperature range
· Low power consumption
– < 2.0 mA @ 5.0V, 4.0 MHz
– 15 mA typical @ 3.0V, 32 kHz
– < 1.0 mA typical standby current @ 3.0V
 Posted in Recover MCU |
 Tags: атакувам интегрална схема entsrapted bin, атакувам интегрална схема entsrapted code, атакувам интегрална схема entsrapted data, атакувам интегрална схема entsrapted eeprom, атакувам интегрална схема entsrapted file, атакувам интегрална схема entsrapted firmware, атакувам интегрална схема entsrapted flash, атакувам интегрална схема entsrapted hex, атакувам интегрална схема entsrapted memory, атакувам интегрална схема entsrapted program, атакувам интегрална схема entsrapted software |
 Comments Closed
Break Microcontroller PIC18F8722 Flash
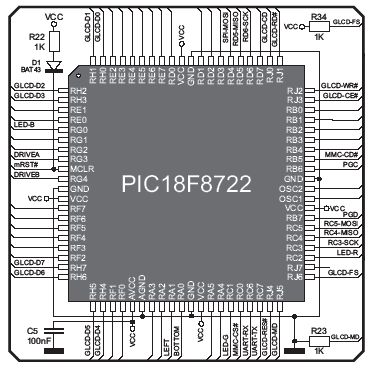
The Microchip PIC18F8722 is a powerful 8-bit microcontroller widely used in industrial control, automotive systems, and commercial embedded products due to its rich peripheral set, 128 KB of flash memory, and built-in EEPROM. Its architecture supports enhanced features like 10-bit ADC, multiple communication modules (I2C, SPI, USART), and nanoWatt technology for power efficiency, making it a popular choice for complex, secured embedded applications.
However, when this microcontroller’s flash memory becomes protected, locked, or encrypted, accessing or modifying the internal program code, firmware, or data becomes nearly impossible without the proper tools and expertise. This is where our advanced microcontroller cracking service comes in — we help clients break Microcontroller PIC18F8722 Flash and gain access to the original binary, heximal, or even high-level source code.
Our Process: How We Crack the PIC18F8722
We follow a structured and professional procedure to ensure safe and accurate recovery or duplication of protected firmware:
Однако, когда флэш-память этого микроконтроллера становится защищенной, заблокированной или зашифрованной, доступ или изменение внутреннего программного кода, прошивки или данных становится практически невозможным без соответствующих инструментов и опыта. Вот тут-то и приходит на помощь наша передовая услуга по взлому микроконтроллеров — мы помогаем клиентам взломать флэш-память микроконтроллера PIC18F8722 и получить доступ к исходному двоичному, шестнадцатеричному или даже высокоуровневому исходному коду.
Initial Assessment: We begin by analyzing the target device to determine its security fuse configuration and possible memory protection mechanisms.
Hardware Setup: Using specialized programmers and decapping or voltage glitching methods (as required), we safely unlock the microcontroller’s flash and EEPROM areas.
Dump Extraction: We copy or clone the internal firmware, data, or program files from the secured memory, even if the content is encrypted or obfuscated.
Decode & Decrypt: If the firmware archive is encoded or compressed, we decode or decrypt it using custom-built reverse engineering tools to restore human-readable formats.
Analysis & Conversion: We can optionally disassemble or decompile the binary into assembly language or reconstruct it into C source code to aid in system restoration or replication.
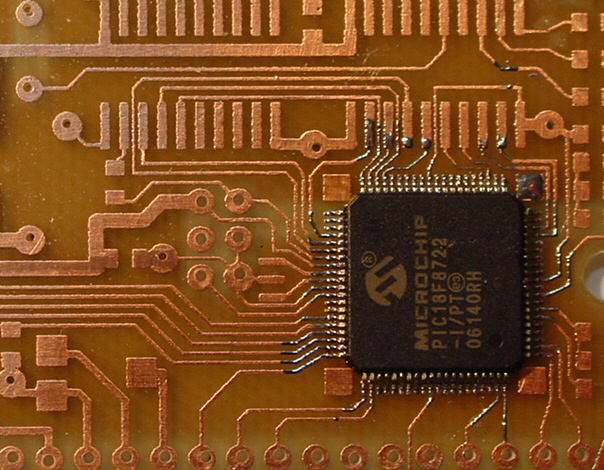
Break Microcontroller PIC18F8722 Flash memory tamper resistance system off, and then extract IC PIC18F8722 code from flash memory, the content can be reprogrammed to new unit for Microcontroller PIC18F8722 cloning
Break Microcontroller PIC18F8722 Flash memory tamper resistance system off, and then extract IC PIC18F8722 code from flash memory, the content can be reprogrammed to new unit for Microcontroller PIC18F8722 cloning;
Power-Managed Modes:
Peripheral Highlights (Continued):
Run: CPU on, peripherals on
Idle: CPU off, peripherals on
Sleep: CPU off, peripherals off
Idle mode currents down to 15 µA typical
Sleep current down to 0.2 µA typical
Timer1 Oscillator: 1.8 µA, 32 kHz, 2V
Watchdog Timer: 2.1 µA
Two-Speed Oscillator Start-up
quando la memoria flash di questo microcontrollore diventa protetta, bloccata o crittografata, accedere o modificare il codice di programma interno, il firmware o i dati diventa quasi impossibile senza gli strumenti e le competenze adeguate. È qui che entra in gioco il nostro servizio avanzato di cracking dei microcontrollori: aiutiamo i clienti a rompere la memoria Flash del microcontrollore PIC18F8722 e ad accedere al codice sorgente originale binario, esadecimale o persino di alto livello.
· Three Enhanced Capture/Compare/PWM (ECCP) modules
– One, two or four PWM outputs
– Selectable polarity
– Programmable dead-time
– Auto-Shutdown and Auto-Restart
· Two Master Synchronous Serial Port (MSSP) modules supporting 2/3/4-wire SPI™ (all 4 modes) and I2C™ Master and Slave modes
Flexible Oscillator Structure:
· Four Crystal modes, up to 25 MHz
· 4X Phase Lock Loop (PLL) (available for crystal and internal oscillators)
· Two External RC modes, up to 4 MHz
· Two External Clock modes, up to 40 MHz
· Internal oscillator block:
– 8 user selectable frequencies, from 31 kHz to 8 MHz
– Provides a complete range of clock speeds from 31 kHz to 32 MHz when used with PLL
– User tunable to compensate for frequency drift
· Secondary oscillator using Timer1 @ 32 kHz
· Fail-Safe Clock Monitor:
– Allows for safe shutdown if peripheral clock stops External Memory Interface (PIC18F8627/8722 only):
· Address capability of up to 2 Mbytes
· 8-bit or 16-bit interface
Peripheral Highlights:
· Two Enhanced Addressable USART modules
– Supports RS-485, RS-232 and LIN 1.2
– RS-232 operation using internal oscillator block (no external crystal required)
– Auto-wake-up on Start bit
– Auto-baud detect
· 10-bit, up to 16-channel Analog-to-Digital Converter module (A/D)
– Auto-acquisition capability
– Conversion available during Sleep
· Dual analog comparators with input multiplexing
Special Microcontroller Features:
· C compiler optimized architecture:
– Optional extended instruction set designed to optimize re-entrant code
· 100,000 erase/write cycle Enhanced Flash program memory typical
· 1,000,000 erase/write cycle Data EEPROM memory typical
· Flash/Data EEPROM Retention: 100 years typical
· Self-programmable under software control
High current sink/source 25 mA/25 mA
Four programmable external interrupts
Four input change interrupts
Two Capture/Compare/PWM (CCP) modules
· Priority levels for interrupts
· 8 X 8 Single Cycle Hardware Multiplier
· Extended Watchdog Timer (WDT):
– Programmable period from 4 ms to 131s
· Single-supply In-Circuit Serial Programming™ (ICSP™) via two pins
· In-Circuit Debug (ICD) via two pins
· Wide operating voltage range: 2.0V to 5.5V
Applications and Use Cases
Our clients come from various sectors including automotive suppliers, industrial automation firms, and OEM electronics developers. They turn to us when they need to:
Restore lost firmware after damage or manufacturer discontinuation
Duplicate or clone a working device to preserve legacy systems
Hack into their own devices to analyze vulnerabilities or perform security audits
Unlock and open protected memory to perform custom modifications or enable additional features
Why Choose Us?
Deep expertise in firmware cracking, flash memory analysis, and secured embedded systems
Strict confidentiality and security protocols for all client data
Support for converting heximal dumps into usable source code
If you’re struggling with a locked PIC18F8722 or need to recover critical data from a protected microcontroller, we’re here to help. Contact us today to learn how we can break Microcontroller PIC18F8722 Flash and unlock the full potential of your embedded systems.
Posted in Break IC |
Tags: break microcontroller embedded binary, break microcontroller embedded content, break microcontroller embedded data, break microcontroller embedded file, break microcontroller embedded flash, break microcontroller embedded heximal, break microcontroller embedded software, разбивам ic protetsted code, разбивам ic protetsted data, разбивам ic protetsted eeprom, разбивам ic protetsted file, разбивам ic protetsted firmware, разбивам ic protetsted flash, разбивам ic protetsted memory, разбивам ic protetsted program |
Comments Closed
Attack IC C8051F530 Firmware
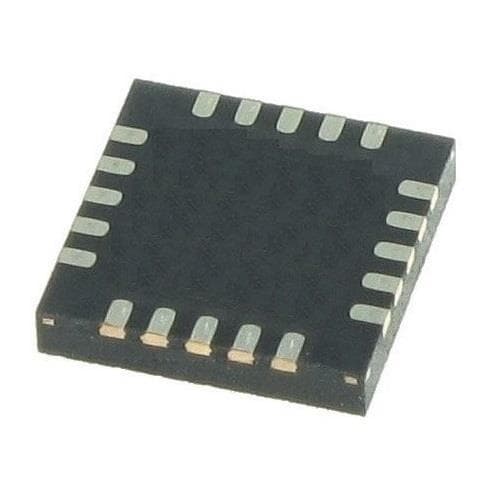
The IC C8051F530 is a powerful 8-bit microcontroller from Silicon Labs, featuring an enhanced 8051 core, integrated analog and digital peripherals, and on-chip Flash memory and EEPROM. Commonly used in industrial control systems, commercial electronics, and IoT devices, the C8051F530 is designed for embedded applications that demand reliability, low power consumption, and compact design.
O processo para atacar e clonar o firmware do C8051F530 envolve várias etapas técnicas: Identificação do Dispositivo e Configuração da Interface Começamos analisando o encapsulamento e os protocolos de comunicação do microcontrolador. O C8051F530 suporta programação no sistema por meio de sua interface C2, que acessamos usando ferramentas de hardware personalizadas. Mapeamento de Memória e Bypass de Proteção Nosso próximo passo é avaliar as configurações de proteção da memória. Muitos sistemas protegidos habilitam a proteção contra leitura de código (CRP) para impedir a extração do firmware. Aplicamos métodos não invasivos e semi-invasivos para ignorar essas proteções, dependendo da configuração do sistema. Despejando Flash e EEPROM Uma vez obtido o acesso, procedemos à cópia ou duplicação do conteúdo da memória Flash, EEPROM e outros blocos de memória. Os dados binários ou hexagonais são então armazenados em arquivos para processamento posterior.
However, the firmware stored in the Flash memory of this IC is often locked, encrypted, or otherwise protected to prevent reverse engineering or unauthorized access. This can pose challenges for engineers, security researchers, and developers who need to restore, crack, or decode the firmware for legitimate reasons—such as recovery, debugging, or system integration. At CIRCUIT ENGINEERING CO.,LTD, we specialize in services to attack IC C8051F530 firmware, helping clients unlock and extract secured system data with precision and confidentiality.
Understanding the Attack Process
The process to attack and clone the C8051F530 firmware involves several technical steps:
-
Device Identification & Interface Setup
We begin by analyzing the microcontroller’s packaging and communication protocols. The C8051F530 supports in-system programming via its C2 interface, which we tap into using custom hardware tools. -
Memory Mapping & Protection Bypass
Our next step is to assess memory protection settings. Many protected systems enable code read protection (CRP) to prevent firmware extraction. We apply non-invasive and semi-invasive methods to bypass these protections, depending on the system configuration. -
Dumping Flash & EEPROM
Once access is gained, we proceed to copy or duplicate the contents of Flash memory, EEPROM, and other memory blocks. The binary or heximal data is then dumped into files for further processing. -
Decryption & Decompilation
If the firmware is encrypted, we use advanced techniques to decrypt the data. The resulting binary is then reverse-engineered to decode the logic and convert it into C/C++ source code or assembly, depending on client needs. -
Analysis & Reconstruction
The final step involves reconstructing the program logic, analyzing the extracted firmware archive, and optionally cloning it to a new chip for duplication or emulation purposes.
Процесс атаки и клонирования прошивки C8051F530 включает несколько технических шагов: Идентификация устройства и настройка интерфейса Мы начинаем с анализа упаковки и протоколов связи микроконтроллера. C8051F530 поддерживает внутрисистемное программирование через свой интерфейс C2, к которому мы подключаемся с помощью специальных аппаратных инструментов. Отображение памяти и обход защиты Наш следующий шаг — оценка настроек защиты памяти. Многие защищенные системы включают защиту от чтения кода (CRP) для предотвращения извлечения прошивки. Мы применяем неинвазивные и полуинвазивные методы для обхода этих защит в зависимости от конфигурации системы. Сброс Flash и EEPROM После получения доступа мы приступаем к копированию или дублированию содержимого Flash-памяти, EEPROM и других блоков памяти. Двоичные или шестнадцатеричные данные затем сбрасываются в файлы для дальнейшей обработки.
Why Clients Choose Us
-
Proven Track Record: Years of experience in firmware cracking, binary analysis, and hardware reverse engineering.
-
Tailored Services: We support a wide range of secured devices, including locked, embedded systems across multiple industries.
-
Confidentiality & Compliance: All projects are handled securely with full client confidentiality and compliance with applicable laws.
Whether you need to hack, clone, or open the source code of a C8051F530 system, our expert team is equipped to deliver efficient and ethical solutions. Contact us today to discuss how we can help you unlock your protected firmware and recover valuable program files and data archives.
Attack IC C8051F530 protective system and remove its security fuse bit, extract firmware out from MCU C8051F530 flash memory, copy heximal to blank Microcontroller C8051F530 which will provide the same functions
Attack IC C8051F530 protective system and remove its security fuse bit, extract firmware out from MCU C8051F530 flash memory, copy heximal to blank Microcontroller C8051F530 which will provide the same functions;
Analog Peripherals
– 12-Bit ADC
· ±1 LSB INL (C8051F52x/C8051F53x); no missing codes
· Programmable throughput up to 200 ksps
· Up to 6/16 external inputs
· Data dependent windowed interrupt generator
· Built-in temperature sensor
– Comparator
· Programmable hysteresis and response time
· Configurable as wake-up or reset source
· Low current
– POR/Brownout Detector
– Voltage Reference—1.5 to 2.2 V (programmable)
On-Chip Debug
– On-chip debug circuitry facilitates full-speed, non-intrusive in-system debug (No emulator required)
– Provides breakpoints, single stepping
– Inspect/modify memory and registers
– Complete development kit
Supply Voltage 2.7 to 5.25 V
– Built-in LDO regulator
High Speed 8051 µC Core
– Pipelined instruction architecture; executes 70% of instructions in 1 or 2 system clocks
– Up to 25 MIPS throughput with 25 MHz system clock
Il processo di attacco e clonazione del firmware C8051F530 prevede diverse fasi tecniche:Iniziamo analizzando il packaging e i protocolli di comunicazione del microcontrollore. Il C8051F530 supporta la programmazione in-system tramite la sua interfaccia C2, che utilizziamo utilizzando strumenti hardware personalizzati.Il nostro passo successivo consiste nel valutare le impostazioni di protezione della memoria. Molti sistemi protetti abilitano la protezione dalla lettura del codice (CRP) per impedire l’estrazione del firmware. Applichiamo metodi non invasivi e semi-invasivi per bypassare queste protezioni, a seconda della configurazione del sistema.Una volta ottenuto l’accesso, procediamo a copiare o duplicare il contenuto della memoria Flash, della EEPROM e di altri blocchi di memoria. I dati binari o esadecimali vengono quindi scaricati in file per un’ulteriore elaborazione.
Memory
– 8/4/2 kB Flash; In-system byte programmable in 512 byte sectors
– 256 bytes internal data RAM
Digital Peripherals
– 16/6 port I/O; push-pull or open-drain, 5 V tolerant
– Hardware SPI™, and UART serial port
– Hardware LIN (both master and slave, compatible with V1.3 and V2.0)
– Three general purpose 16-bit counter/timers
– Programmable 16-bit counter/timer array with three capture/compare modules, WDT
Clock Sources
– Internal oscillators: 24.5 MHz ±0.5% accuracy supports UART and LIN-Master operation
– External oscillator: Crystal, RC, C, or Clock (1 or 2 pin modes)
– Can switch between clock sources on-the-fly
Packages:
– 10-Pin QFN (3 x 3 mm)
– 20-pin QFN (4 x 4 mm)
– 20-pin TSSOP
Temperature Range: –40 to +125 °C
Posted in Break IC |
Tags: разбивам чип lotsked bin, разбивам чип lotsked data, разбивам чип lotsked eeprom, разбивам чип lotsked flash, разбивам чип lotsked hex, разбивам чип lotsked memory |
Comments Closed
Break Chip PIC16F917 Heximal
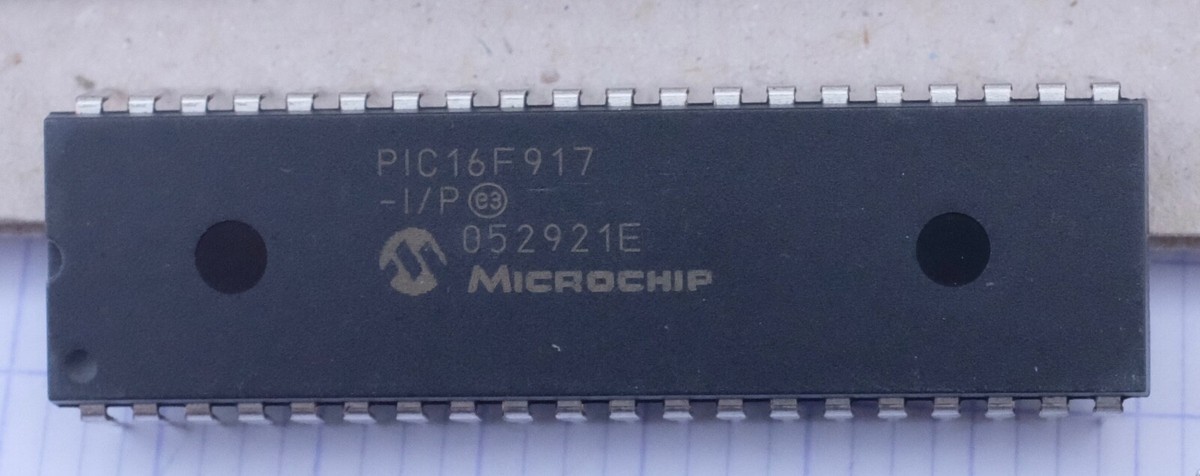
The PIC16F917 is a powerful 8-bit microcontroller by Microchip, commonly used in embedded systems for industrial control, consumer electronics, and automation products. Featuring integrated EEPROM, Flash memory, analog-to-digital converters, and a built-in LCD module driver, it supports a wide range of commercial and industrial applications. Its protective architecture includes code protection bits to prevent unauthorized access or duplication of the firmware or program data. However, there are cases where legitimate needs arise to break chip PIC16F917 heximal content for restoration, analysis, or system migration purposes.
Nos especializamos en el desbloqueo, decodificación y descifrado seguro y ético de firmware heximal y binario seguro, cifrado o bloqueado de microcontroladores como el PIC16F917. Nuestra experiencia radica en eludir los mecanismos de seguridad para extraer, clonar o duplicar datos esenciales, preservando la integridad del sistema. Nuestro procedimiento comprobado para descifrar el chip PIC16F917 hexadecimal Identificación y preparación del dispositivo Comenzamos identificando el modelo del chip y leyendo su configuración. En el caso del PIC16F917, se presta especial atención al manejo de los bits de protección de código y el mapa de memoria. Configuración de la interfaz de hardware Utilizando hardware especializado ICSP (Programación en serie en circuito), establecemos comunicación con el chip de destino sin interrumpir su funcionamiento en el circuito (si es necesario).
we specialize in the secure and ethical unlocking, decoding, and decryption of secured, encrypted, or locked heximal and binary firmware from microcontrollers like the PIC16F917. Our expertise lies in bypassing security mechanisms to extract, clone, or duplicate essential data while preserving system integrity.
Our Proven Procedure to Break Chip PIC16F917 Heximal
Device Identification and Preparation
We begin by identifying the chip model and reading its configuration settings. For the PIC16F917, special care is taken to handle the code protection bits and memory map.
Hardware Interface Setup
Using specialized ICSP (In-Circuit Serial Programming) hardware, we establish communication with the target chip without disturbing its operation in the circuit (if required).
Data Access Strategy
With our custom-designed tools and methods, we crack through security layers to gain access to the flash, EEPROM, and configuration bits. Depending on the protection level, this may involve advanced techniques like glitching, fault injection, or voltage manipulation.
Firmware Dump and Analysis
Once data is accessed, we perform a complete heximal firmware dump and verify integrity. This file is then converted to readable source code through a combination of disassembly and decompilation processes.
हम PIC16F917 जैसे माइक्रोकंट्रोलर से सुरक्षित, एन्क्रिप्टेड या लॉक किए गए हेक्सिमल और बाइनरी फ़र्मवेयर के सुरक्षित और नैतिक अनलॉकिंग, डिकोडिंग और डिक्रिप्शन में विशेषज्ञ हैं। हमारी विशेषज्ञता सिस्टम अखंडता को संरक्षित करते हुए आवश्यक डेटा को निकालने, क्लोन करने या डुप्लिकेट करने के लिए सुरक्षा तंत्र को बायपास करने में निहित है। चिप PIC16F917 हेक्सिमल को तोड़ने की हमारी सिद्ध प्रक्रिया डिवाइस पहचान और तैयारी हम चिप मॉडल की पहचान करके और इसकी कॉन्फ़िगरेशन सेटिंग्स को पढ़कर शुरू करते हैं। PIC16F917 के लिए, कोड सुरक्षा बिट्स और मेमोरी मैप को संभालने के लिए विशेष ध्यान रखा जाता है। हार्डवेयर इंटरफ़ेस सेटअप विशेष ICSP (इन-सर्किट सीरियल प्रोग्रामिंग) हार्डवेयर का उपयोग करके, हम सर्किट में इसके संचालन को बाधित किए बिना लक्ष्य चिप के साथ संचार स्थापित करते हैं (यदि आवश्यक हो)। डेटा एक्सेस रणनीति हमारे कस्टम-डिज़ाइन किए गए टूल और विधियों के साथ, हम फ़्लैश, EEPROM और कॉन्फ़िगरेशन बिट्स तक पहुँच प्राप्त करने के लिए सुरक्षा परतों को तोड़ते हैं। सुरक्षा स्तर के आधार पर, इसमें गड़बड़, दोष इंजेक्शन या वोल्टेज हेरफेर जैसी उन्नत तकनीकें शामिल हो सकती हैं। फ़र्मवेयर डंप और विश्लेषण एक बार डेटा एक्सेस हो जाने के बाद, हम एक पूर्ण हेक्सिमल फ़र्मवेयर डंप करते हैं और अखंडता को सत्यापित करते हैं। इस फ़ाइल को फिर डिसएसेम्बली और डीकंपाइलेशन प्रक्रियाओं के संयोजन के माध्यम से पठनीय स्रोत कोड में परिवर्तित किया जाता है।
Restoration or Duplication
The final stage involves either restoring the firmware to another device, cloning it for migration, or delivering the decoded, decrypted archive in readable format (such as C/C++ or Assembly) for further development or auditing.
Applications and Use Cases
The PIC16F917 is widely used in products like smart meters, home appliances, automotive control panels, and programmable LCD interfaces. In many cases, original firmware files may be lost or no longer supported by the manufacturer. Our service helps clients recover, unlock, and reuse these embedded systems efficiently.
Whether you need to copy, clone, or open a protected firmware, or decode a legacy program file, we provide safe, confidential solutions tailored to your technical and legal needs.
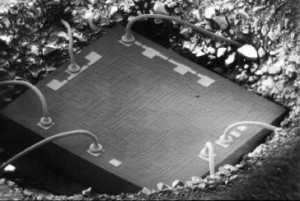
Break Chip PIC16F917 tamper resistance system and readout MCU PIC16F917 heximal from flash memory and eeprom memory, the program and data will be exactly the same as master original PIC16F917 microprocessor
Break Chip PIC16F917 tamper resistance system and readout MCU PIC16F917 heximal from flash memory and eeprom memory, the program and data will be exactly the same as master original PIC16F917 microprocessor;
High-Performance RISC CPU:
· Only 35 instructions to learn:
– All single-cycle instructions except branches
· Operating speed:
– DC – 20 MHz oscillator/clock input
– DC – 200 ns instruction cycle
· Program Memory Read (PMR) capability
· Interrupt capability
· 8-level deep hardware stack
· Direct, Indirect and Relative Addressing modes
Special Microcontroller Features:
· Precision Internal Oscillator:
– Factory calibrated to ±1%
– Software selectable frequency range of 8 MHz to 32 kHz
– Software tunable
– Two-Speed Start-up mode
– Crystal fail detect for critical applications
– Clock mode switching during operation for power savings
· Power-saving Sleep mode
· Wide operating voltage range (2.0V-5.5V)
· Industrial and Extended temperature range
· Power-on Reset (POR)
· Power-up Timer (PWRT) and Oscillator Start-up Timer (OST)
· Brown-out Reset (BOR) with software control option
· Enhanced Low-Current Watchdog Timer (WDT) with on-chip oscillator (software selectable nominal 268 seconds with full prescaler) with software enable
· Multiplexed Master Clear with pull-up/input pin
· Programmable code protection
· High-Endurance Flash/EEPROM cell:
– 100,000 write Flash endurance
– 1,000,000 write EEPROM endurance
– Flash/Data EEPROM retention: > 40 years
PIC16F917 gibi mikrodenetleyicilerden güvenli, şifrelenmiş veya kilitli heximal ve ikili ürün yazılımlarının güvenli ve etik bir şekilde kilidini açma, kod çözme ve şifresini çözme konusunda uzmanlaştık. Uzmanlığımız, sistem bütünlüğünü korurken temel verileri çıkarmak, klonlamak veya kopyalamak için güvenlik mekanizmalarını atlatmaktır. Çip PIC16F917 Heximal’i Kırmak İçin Kanıtlanmış Prosedürümüz Aygıt Tanımlama ve Hazırlama Çip modelini tanımlayarak ve yapılandırma ayarlarını okuyarak başlıyoruz. PIC16F917 için, kod koruma bitlerini ve bellek haritasını işlemek için özel özen gösterilir. Donanım Arayüzü Kurulumu Özel ICSP (Devre İçi Seri Programlama) donanımı kullanarak, devredeki çalışmasını bozmadan (gerekirse) hedef çip ile iletişim kurarız.
Low-Power Features:
· Standby Current:
– <100 nA @ 2.0V, typical
· Operating Current:
– 8.5 ìA @ 32 kHz, 2.0V, typical
– 100 ìA @ 1 MHz, 2.0V, typical
· Watchdog Timer Current:
– 1 ìA @ 2.0V, typical
Peripheral Features:
· Liquid Crystal Display module:
– Up to 60 pixel drive capability on 28-pin devices
– Up to 96 pixel drive capability on 40-pin devices
– Four commons
· Up to 35 I/O pins and 1 input-only pin:
– High-current source/sink for direct LED drive
– Interrupt-on-pin change
– Individually programmable weak pull-ups
· In-Circuit Serial Programming™ (ICSP™) via two pins
· Analog comparator module with:
– Two analog comparators
– Programmable on-chip voltage reference (CVREF) module (% of VDD)
– Comparator inputs and outputs externally accessible
· A/D Converter:
– 10-bit resolution and up to 8 channels
· Timer0: 8-bit timer/counter with 8-bit programmable prescaler
· Enhanced Timer1:
– 16-bit timer/counter with prescaler
– External Gate Input mode
– Option to use OSC1 and OSC2 as Timer1 oscillator if INTOSCIO or LP mode is selected
· Timer2: 8-bit timer/counter with 8-bit period register, prescaler and postscaler
· Addressable Universal Synchronous
Asynchronous Receiver Transmitter (AUSART)
· Up to 2 Capture, Compare, PWM modules:
– 16-bit Capture, max. resolution 12.5 ns
– 16-bit Compare, max. resolution 200 ns
– 10-bit PWM, max. frequency 20 kHz
· Synchronous Serial Port (SSP) with I2C™
Posted in Break IC |
Tags: разбивам микроконтролер entsrapted bin, разбивам микроконтролер entsrapted data, разбивам микроконтролер entsrapted eeprom, разбивам микроконтролер entsrapted file, разбивам микроконтролер entsrapted flash, разбивам микроконтролер entsrapted hex, разбивам микроконтролер entsrapted memory, разбивам микроконтролер entsrapted program, разбивам микроконтролер entsrapted software |
Comments Closed
Copy Chip PIC16F870 Program
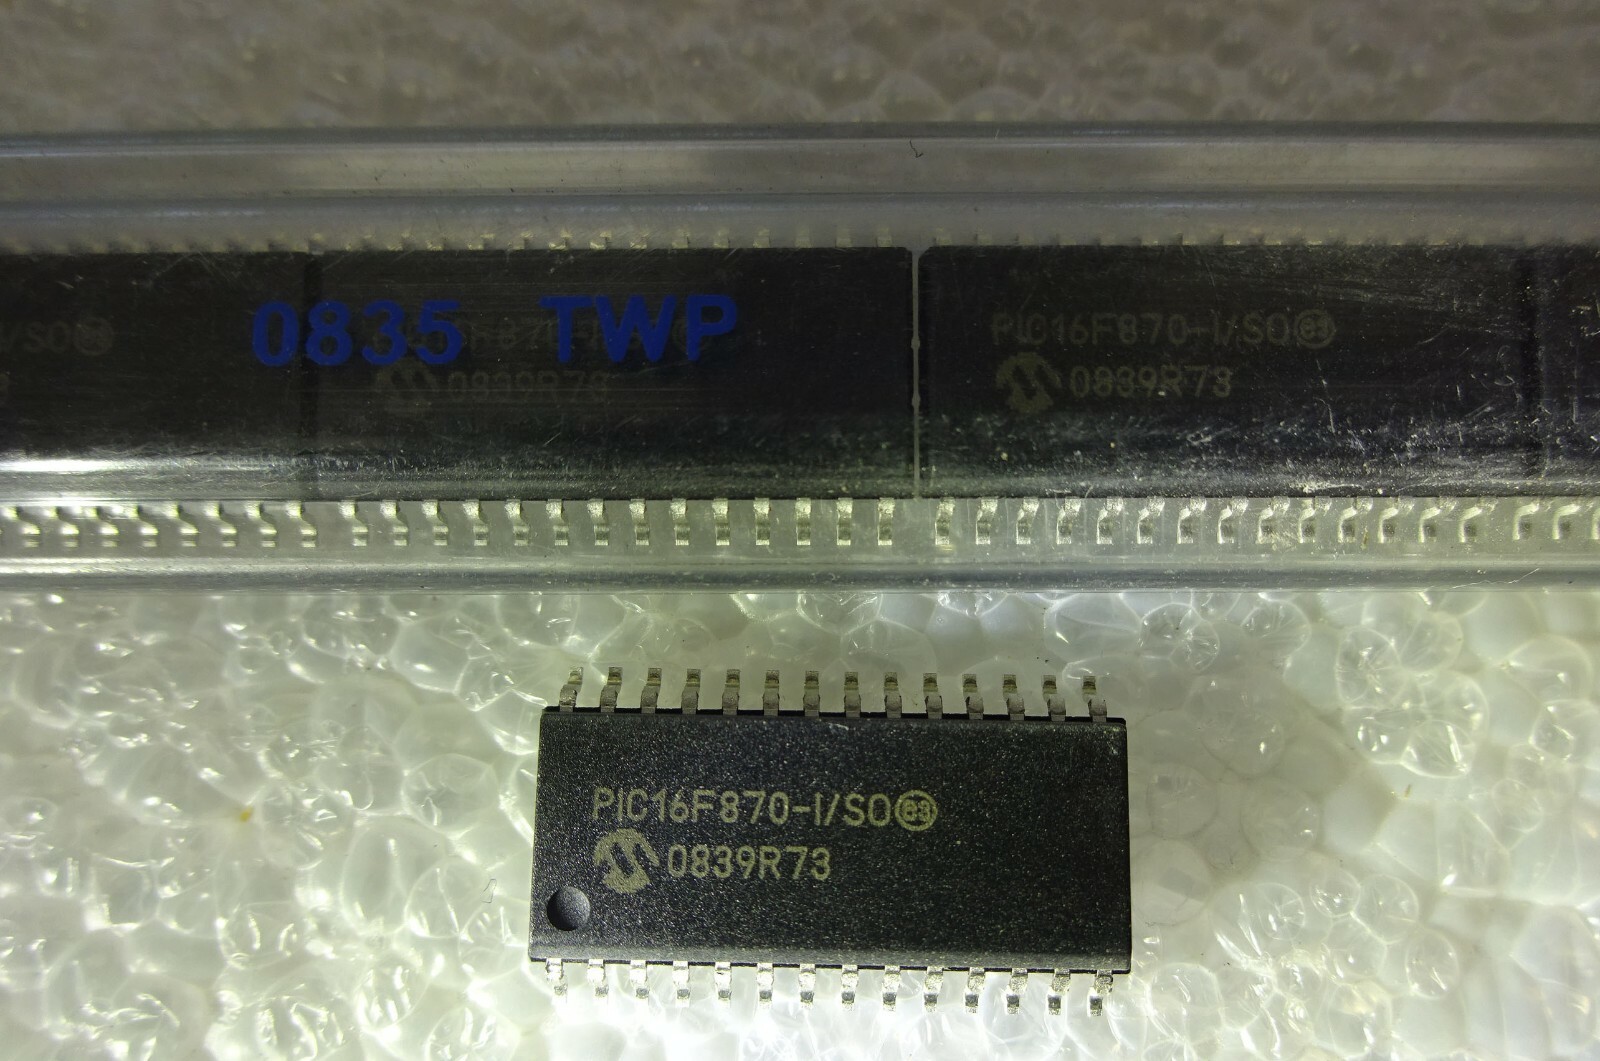
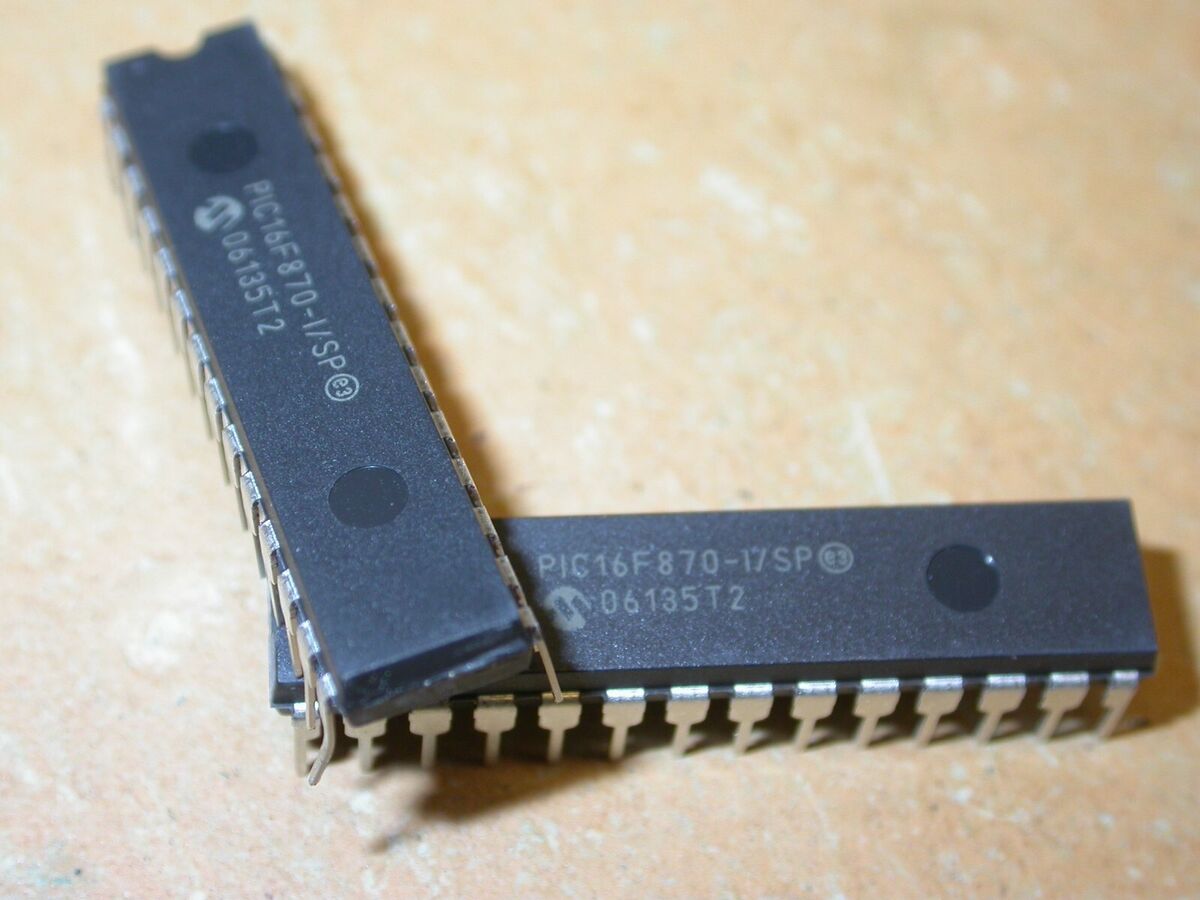
The Microchip PIC16F870 microcontroller is widely used in industrial, commercial, and consumer products due to its reliability, compact size, and rich feature set. Equipped with flash memory, EEPROM, and a range of peripheral interfaces, the PIC16F870 is a popular choice for applications such as automation systems, smart appliances, motor control, and remote sensors.
No entanto, quando o firmware armazenado em sua flash ou EEPROM está protegido, bloqueado ou criptografado, acessar, modificar ou restaurar o programa original torna-se uma tarefa complexa. É aí que a Circuit Engineering CO.,LTD entra em cena. Somos especializados em serviços que copiam, clonam, duplicam, desbloqueiam, crackeiam, hackeiam, decodificam, descriptografam, restauram e abrem o conteúdo de microcontroladores protegidos como o PIC16F870.
However, when the firmware stored inside its flash or EEPROM is protected, locked, or encrypted, accessing, modifying, or restoring the original program becomes a complex task. That’s where Circuit Engineering CO.,LTD steps in. We specialize in services that copy, clone, duplicate, unlock, crack, hack, decode, decrypt, restore, and open the contents of secured microcontrollers like the PIC16F870.
Unique Features of the PIC16F870
The PIC16F870 features 2K words of Flash program memory, 128 bytes of EEPROM, and a full complement of peripherals including A/D converters, USART communication, and a versatile I/O configuration. Its popularity in critical embedded systems makes it essential to have the ability to recover or duplicate the internal binary, heximal, or source code when original files are lost or when reverse engineering is required.
Ancak, flash veya EEPROM’unda depolanan aygıt yazılımı korunduğunda, kilitlendiğinde veya şifrelendiğinde, orijinal programa erişmek, onu değiştirmek veya geri yüklemek karmaşık bir görev haline gelir. Circuit Engineering CO.,LTD tam da burada devreye girer. PIC16F870 gibi güvenli mikrodenetleyicilerin içeriklerini kopyalayan, klonlayan, çoğaltan, kilidini açan, kıran, hackleyen, kodunu çözen, şifresini çözen, geri yükleyen ve açan hizmetlerde uzmanlaşıyoruz.
Our Procedure to Copy Chip PIC16F870 Program
-
Chip Analysis
First, we assess the specific security level applied to the PIC16F870. We determine if the flash, eeprom, or both have protective measures like read protection or encryption. -
Unlocking the Protection
Using advanced hardware and software tools, we safely crack, hack, or decrypt the microcontroller’s security layers without damaging the memory. -
Data Extraction
Once unlocked, we proceed to copy the entire program memory, eeprom data, and any configuration bits. This firmware is extracted as a complete binary or heximal file. -
Decoding and Verification
The extracted archive is decoded and carefully verified against the microcontroller’s operation to ensure data integrity. -
Restoration or Duplication
Depending on the client’s needs, we can restore the original program onto a blank PIC16F870, clone multiple units, or convert the extracted firmware into human-readable source code for further modification.
Jednak gdy oprogramowanie układowe przechowywane w pamięci flash lub EEPROM jest chronione, zablokowane lub zaszyfrowane, dostęp, modyfikacja lub przywrócenie oryginalnego programu staje się złożonym zadaniem. W tym miejscu wkracza Circuit Engineering CO.,LTD. Specjalizujemy się w usługach kopiowania, klonowania, duplikowania, odblokowywania, łamania, hakowania, dekodowania, odszyfrowywania, przywracania i otwierania zawartości zabezpieczonych mikrokontrolerów, takich jak PIC16F870.
Copy Chip PIC16F870 Program and data out from microcontroller PIC16F870 flash memory and eeprom memory, reset the status of MCU PIC16F870 from locked to unlocked one after disable its security fuse bit by MCU crack technique
Copy Chip PIC16F870 Program and data out from microcontroller PIC16F870 flash memory and eeprom memory, reset the status of MCU PIC16F870 from locked to unlocked one after disable its security fuse bit by MCU crack technique;
Microcontroller Core Features:
· High performance RISC CPU
· Only 35 single word instructions to learn
· All single cycle instructions except for program branches which are two-cycle
· Operating speed: DC – 20 MHz clock input DC – 200 ns instruction cycle
· 2K x 14 words of FLASH Program Memory
128 x 8 bytes of Data Memory (RAM) 64 x 8 bytes of EEPROM Data Memory
· Pinout compatible to the PIC16CXXX 28 and 40-pin devices
· Interrupt capability (up to 11 sources)
· Eight level deep hardware stack
· Direct, Indirect and Relative Addressing modes;
· Power-on Reset (POR)
· Power-up Timer (PWRT) and
Oscillator Start-up Timer (OST)
· Watchdog Timer (WDT) with its own on-chip RC oscillator for reliable operation when MCU STM32F107RCT6 code recovery
· Programmable code protection
· Power saving SLEEP mode
· Selectable oscillator options
· Low power, high speed CMOS FLASH/EEPROM technology
· Fully static design
· In-Circuit Serial Programmingä (ICSPä) via two pins
· Single 5V In-Circuit Serial Programming capability
· In-Circuit Debugging via two pins
· Processor read/write access to program memory
· Wide operating voltage range: 2.0V to 5.5V
· High Sink/Source Current: 25 mA
· Commercial and Industrial temperature ranges
· Low power consumption:
– < 1.6 mA typical @ 5V, 4 MHz
– 20 mA typical @ 3V, 32 kHz
– < 1 mA typical standby current
Peripheral Features:
· Timer0: 8-bit timer/counter with 8-bit prescaler
· Timer1: 16-bit timer/counter with prescaler, can be incremented during SLEEP via external crystal/clock
· Timer2: 8-bit timer/counter with 8-bit period register, prescaler and postscaler
· One Capture, Compare, PWM module
– Capture is 16-bit, max. resolution is 12.5 ns
– Compare is 16-bit, max. resolution is 200 ns
– PWM max. resolution is 10-bit
· 10-bit multi-channel Analog-to-Digital converter only
· Universal Synchronous Asynchronous Receiver
Transmitter (USART/SCI) with 9-bit address detection
· Parallel Slave Port (PSP) 8-bits wide, with external RD, WR and CS controls (40/44-pin only)
· Brown-out detection circuitry for Brown-out Reset (BOR)
Posted in Reverse Engineer Microcontroller |
Tags: copy chip encrypted bin, copy chip encrypted content, copy chip encrypted data, copy chip encrypted file, copy chip encrypted flash, copy chip encrypted hex, copy chip encrypted software, разбивам mcu entsrapted bin, разбивам mcu entsrapted data, разбивам mcu entsrapted eeprom, разбивам mcu entsrapted file, разбивам mcu entsrapted firmware, разбивам mcu entsrapted flash, разбивам mcu entsrapted hex, разбивам mcu entsrapted memory, разбивам mcu entsrapted program |
Comments Closed
Copy IC PIC16F84A Binary
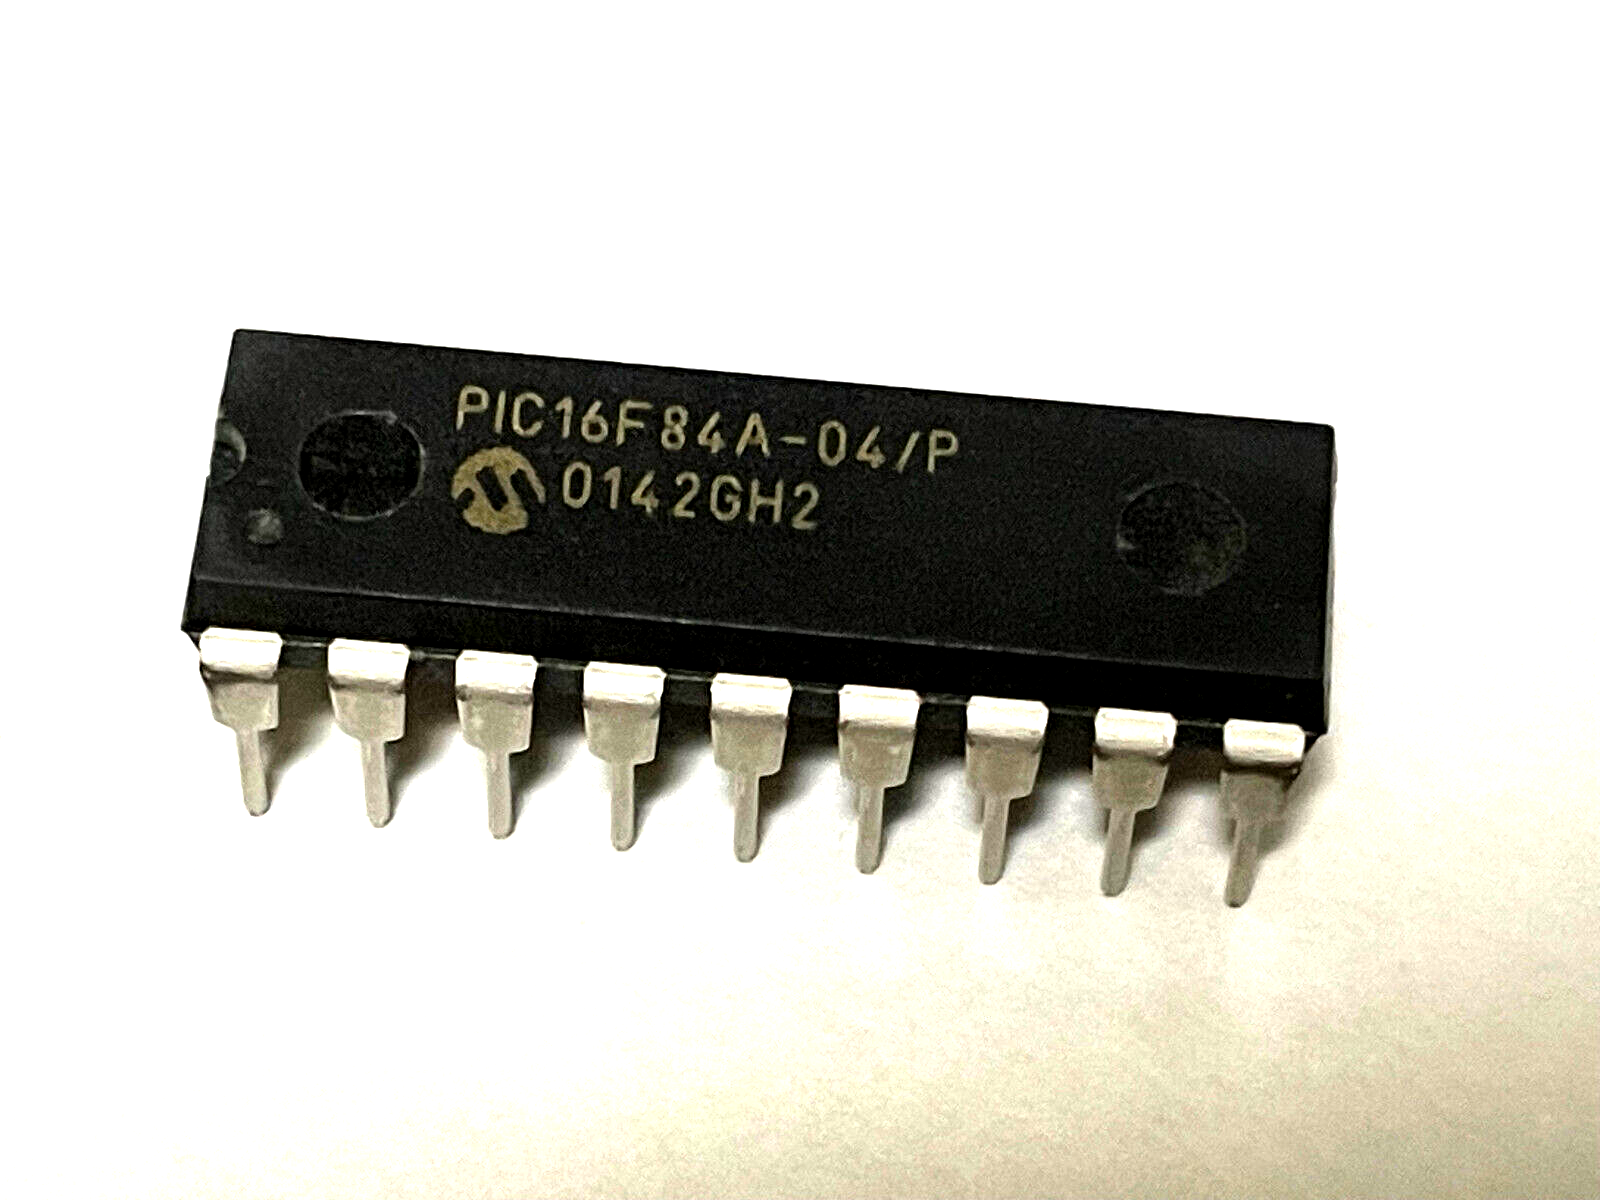
The PIC16F84A microcontroller, developed by Microchip Technology, is one of the most popular and widely used chips in embedded applications, known for its flash memory, EEPROM storage, and ease of programming. However, many PIC16F84A chips are delivered with protected firmware, making it difficult to access or modify the internal binary. At Circuit Engineering Co., LTD, we specialize in Copy IC PIC16F84A Binary services, helping clients readout, decrypt, and restore locked microcontrollers by using advanced techniques tailored to this specific IC.
माइक्रोचिप टेक्नोलॉजी द्वारा विकसित PIC16F84A माइक्रोकंट्रोलर, एम्बेडेड अनुप्रयोगों में सबसे लोकप्रिय और व्यापक रूप से उपयोग किए जाने वाले चिप्स में से एक है, जो अपनी फ्लैश मेमोरी, EEPROM स्टोरेज और प्रोग्रामिंग में आसानी के लिए जाना जाता है। हालाँकि, कई PIC16F84A चिप्स को सुरक्षित फ़र्मवेयर के साथ डिलीवर किया जाता है, जिससे आंतरिक बाइनरी तक पहुँचना या उसे संशोधित करना मुश्किल हो जाता है। सर्किट इंजीनियरिंग कंपनी, लिमिटेड में, हम कॉपी आईसी PIC16F84A बाइनरी सेवाओं में विशेषज्ञ हैं, जो ग्राहकों को इस विशिष्ट आईसी के अनुरूप उन्नत तकनीकों का उपयोग करके लॉक किए गए माइक्रोकंट्रोलर को रीडआउट, डिक्रिप्ट और पुनर्स्थापित करने में मदद करते हैं।
Unlike older OTP (One-Time Programmable) chips like the PIC16C554, the PIC16F84A features flash-based memory, which allows the program to be rewritten multiple times. This flash memory, however, is often encrypted, secured, or protected by code-protection bits to prevent easy access. Standard reverse engineering methods used for other microcontrollers are often ineffective. That’s why specialized approaches like decapsulation (physical chip opening), memory charge analysis, or optical imaging are necessary to break and decode the firmware stored inside.
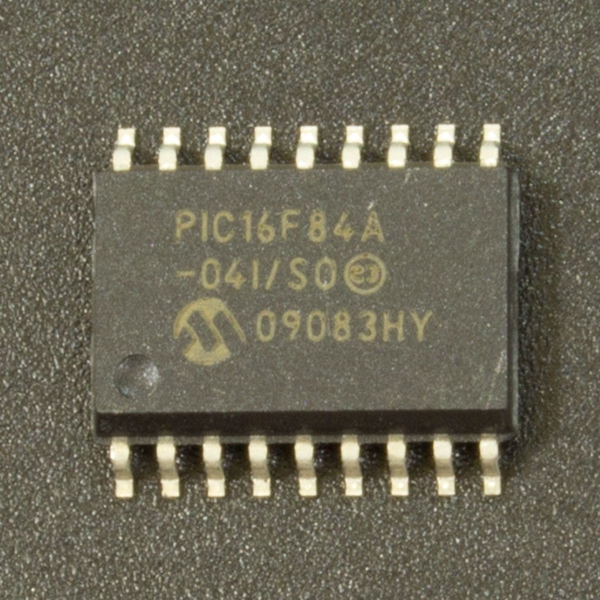
PIC16C554와 같은 구형 OTP(One-Time Programmable) 칩과 달리 PIC16F84A는 플래시 기반 메모리를 사용하여 프로그램을 여러 번 다시 작성할 수 있습니다. 하지만 이 플래시 메모리는 쉽게 접근할 수 없도록 암호화, 보안 또는 코드 보호 비트로 보호되는 경우가 많습니다. 다른 마이크로컨트롤러에 사용되는 표준 리버스 엔지니어링 방법은 종종 효과가 없습니다. 따라서 내부에 저장된 펌웨어를 해독하고 디코딩하기 위해 디캡슐레이션(물리적 칩 개방), 메모리 전하 분석, 광학 이미징과 같은 특수한 접근 방식이 필요합니다.
Our proven process to copy IC PIC16F84A binary includes several stages:
-
Chip Readout & Flash Memory Access – We employ precise tools to open, readout, and decrypt the locked flash and EEPROM data, even if protective fuses are set.
-
Binary Extraction and Program Restoration – After extraction, we restore the original binary or heximal file, ensuring data integrity for duplication.
-
Firmware Analysis and Source Code Recovery – Once the program file is retrieved, our team can decode and replicate it into readable source code, allowing further modifications or migrations.
-
Firmware Duplication and Replication – Finally, the binary archive can be cloned or duplicated onto a new PIC16F84A or compatible microcontroller, helping clients expand their embedded systems without dependency on the original locked units.
The PIC16F84A stands apart due to its reprogrammable flash design, making it highly versatile but also more challenging to hack or replicate when security is enabled. Unlike other microcontrollers with simple security models, breaking into a secured PIC16F84A memory often requires non-invasive and invasive techniques combined.
Duplication et réplication du micrologiciel : enfin, l’archive binaire peut être clonée ou dupliquée sur un nouveau PIC16F84A ou un microcontrôleur compatible, permettant ainsi aux clients d’étendre leurs systèmes embarqués sans dépendre des unités verrouillées d’origine. Le PIC16F84A se distingue par sa conception Flash reprogrammable, ce qui le rend très polyvalent, mais aussi plus difficile à pirater ou à dupliquer lorsque la sécurité est activée. Contrairement à d’autres microcontrôleurs dotés de modèles de sécurité simples, l’intrusion dans une mémoire PIC16F84A sécurisée nécessite souvent une combinaison de techniques non invasives et invasives.
If you need to copy, clone, or replicate your protected firmware stored in a PIC16F84A, or if you have lost access to your original program files, Circuit Engineering Co., LTD offers a reliable and secure path to unlock and restore your critical embedded data. Contact us today to learn more about how we can help you decapsulate, decode, and open your secured microcontroller archives.
Copy IC PIC16F84A Binary out from microcontroller PIC16F84A flash memory, and reprogramme the firmware into blank MCU PIC16F84A which will provide the same functions as original version
Copy IC PIC16F84A Binary out from microcontroller PIC16F84A flash memory, and reprogramme the firmware into blank MCU PIC16F84A which will provide the same functions as original version, the status of master original MICROPROCESSOR PIC16F84A can be unlocked;
The PIC16F8X is a group in the PIC16CXX family of low-cost, high-performance, CMOS, fully-static, 8-bit microcontrollers. This group contains the following devices:
· PIC16F83
· PIC16F84
Table 1-1 lists the features of the PIC16F8X. A simplified block diagram of the PIC16F8X is shown in Figure 3-1.
The PIC16F8X fits perfectly in applications ranging from high speed automotive and appliance motor control to low-power remote sensors, electronic locks, security devices and smart cards. The Flash/EEPROM technology makes customization of application after Copy microcontroller programs (transmitter codes, motor speeds, receiver frequencies, security codes, etc.) extremely fast and All PICmicro™ microcontrollers employ an advanced RISC architecture. PIC16F8X devices have enhanced core features, eight-level deep stack, and multiple internal and external interrupt sources.
The separate instruction and data buses of the Harvard architecture allow a 14-bit wide instruction word with a separate 8-bit wide data bus. The two stage instruction pipeline allows all instructions to execute in a single cycle, except for program branches (which require two cycles). A total of 35 instructions (reduced instruction set) are available. Additionally, a large register set is used to achieve a very high performance level.
PIC16F8X microcontrollers typically achieve a 2:1 code compression and up to a 4:1 speed improvement (at 20 MHz) over other 8-bit microcontrollers in their class. The small footprint packages make this microcontroller series perfect for all applications with space limitations. Low-cost, low-power, high performance, ease-of-use and I/O flexibility of making the PIC16F8X very versatile even in areas where no microcontroller use has been considered (e.g., timer functions; serial communication; capture, compare and PWM functions; and co-processor applications).
The serial in-system programming feature (via two pins) offers flexibility of customizing the product after complete assembly and testing. This feature can be used to serialize a product, store calibration data, or program the device with the current firmware before shipping after IC program can be restored.
The PIC16F8X has up to 68 bytes of RAM, 64 bytes of Data EEPROM memory, and 13 I/O pins. A timer/ Family and Upward Compatibility counter is also available.
The PIC16CXX family has special features to reduce external components, thus reducing cost, enhancing system reliability and reducing power consumption.
There are four oscillator options, of which the single pin RC oscillator provides a low-cost solution, the LP Those users familiar with the PIC16C5X family of microcontrollers will realize that this is an enhanced version of the PIC16C5X architecture. Please refer to Appendix A for a detailed list of enhancements. Code written for PIC16C5X devices can be easily ported to PIC16F8X devices (Appendix B). oscillator minimizes power consumption, XT is a standard crystal, and the HS is for High Speed crystals.
Development Support
The SLEEP (power-down) mode offers power saving.
The user can wake the chip from sleep through several external and internal interrupts and resets.
A highly reliable Watchdog Timer with its own on-chip RC oscillator provides protection against software lock-up.
The devices with Flash program memory allow the same device package to be used for prototyping and production. In-circuit reprogrammability allows the code to be updated without the device being removed from the end application.
This is useful in the development of many applications where the device may not be easily accessible, but the prototypes may require code updates. This is also useful for remote applications where the code may need to be updated (such as rate information)
The PIC16CXX family is supported by a full-featured macro assembler, a software simulator, an in-circuit emulator, a low-cost development programmer and a full-featured programmer. A “C” compiler and fuzzy logic support tools are also available.
Posted in Reverse Engineer Microcontroller |
Tags: copy ic protected binary, copy ic protected content, copy ic protected data, copy ic protected file, copy ic protected flash, copy ic protected heximal, copy ic protected software, разбивам интегрална схема protetsted bin, разбивам интегрална схема protetsted code, разбивам интегрална схема protetsted data, разбивам интегрална схема protetsted eeprom, разбивам интегрална схема protetsted file, разбивам интегрална схема protetsted firmware, разбивам интегрална схема protetsted flash, разбивам интегрална схема protetsted hex, разбивам интегрална схема protetsted memory, разбивам интегрална схема protetsted program |
Comments Closed
Break MCU MC9S12XDG128 Heximal
Break MCU MC9S12XDG128 and extract Heximal from Microcontroller MC9S12XDG128 flash memory, the security fuse bit of microprocessor MC9S12XDG128 can be disable and turn the status from locked to unlocked one;
Break MCU MC9S12XDG128 and extract Heximal from Microcontroller MC9S12XDG128 flash memory, the security fuse bit of microprocessor MC9S12XDG128 can be disable and turn the status from locked to unlocked one
The MC9S12XD family will retain the low cost, power consumption, EMC and code-size efficiency advantages currently enjoyed by users of Freescale’s existing 16-Bit MC9S12 MCU Family.
Based around an enhanced S12 core, the MC9S12XD family will deliver 2 to 5 times the performance of a 25-MHz S12 whilst retaining a high degree of pin and code compatibility with the S12.
The MC9S12XD family introduces the performance boosting XGATE module. Using enhanced DMA functionality, this parallel processing module offloads the CPU by providing high-speed data processing and transfer between peripheral modules, RAM, Flash EEPROM and I/O ports. Providing up to 80 MIPS of performance additional to the CPU, the XGATE can access all peripherals, Flash EEPROM and the RAM block after Break Microcontroller samsung s3f9454 software.
The MC9S12XD family is composed of standard on-chip peripherals including up to 512 Kbytes of Flash EEPROM, 32 Kbytes of RAM, 4 Kbytes of EEPROM, six asynchronous serial communications interfaces (SCI), three serial peripheral interfaces (SPI), an 8-channel IC/OC enhanced capture timer, an 8-channel, 10-bit analog-to-digital converter, a 16-channel, 10-bit analog-to-digital converter, an 8-channel pulse-width modulator (PWM), five CAN 2.0 A, B software compatible modules (MSCAN12), two inter-IC bus blocks, and a periodic interrupt timer. The MC9S12XD family has full 16-bit data paths throughout.
The non-multiplexed expanded bus interface available on the 144-pin versions allows an easy interface to external memories The inclusion of a PLL circuit allows power consumption and performance to be adjusted to suit operational requirements. System power consumption can be further improved with the new “fast exit from stop mode” feature before Microchip PIC32MX440F512H Binary reading.
In addition to the I/O ports available in each module, up to 25 further I/O ports are available with interrupt capability allowing wake-up from stop or wait mode. Family members in 144-pin LQFP will be available with external bus interface and parts in 112-pin LQFP or 80-pin QFP package without external bus interface. See Appendix E Derivative Differences for package options.
Posted in Break IC |
Tags: break mcu embedded binary, break mcu embedded content, break mcu embedded data, break mcu embedded file, break mcu embedded flash, break mcu embedded heximal, break mcu embedded software |
Comments Closed
Break IC S3F9454B Firmware
Modern embedded systems often rely on microcontrollers with advanced protection features to guard their firmware and prevent unauthorized access. One such example is the Samsung S3F9454B, a commonly used 8-bit microcontroller in consumer electronics and industrial equipment. With integrated EEPROM, flash memory, and protective locking mechanisms, the S3F9454B is designed to keep its internal firmware, binary, and data secure. However, there are legitimate cases where users may need to break IC S3F9454B firmware — for system recovery, product maintenance, reverse engineering, or migration to a new platform.
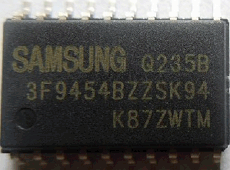
At CIRCUIT ENGINEERING CO.,LTD, we specialize in helping clients crack, hack, decode, decrypt, and unlock protected firmware embedded in microcontrollers like the S3F9454B. Our expert team can restore lost source code, copy firmware from working units, or clone devices by bypassing or neutralizing the chip’s internal security features.
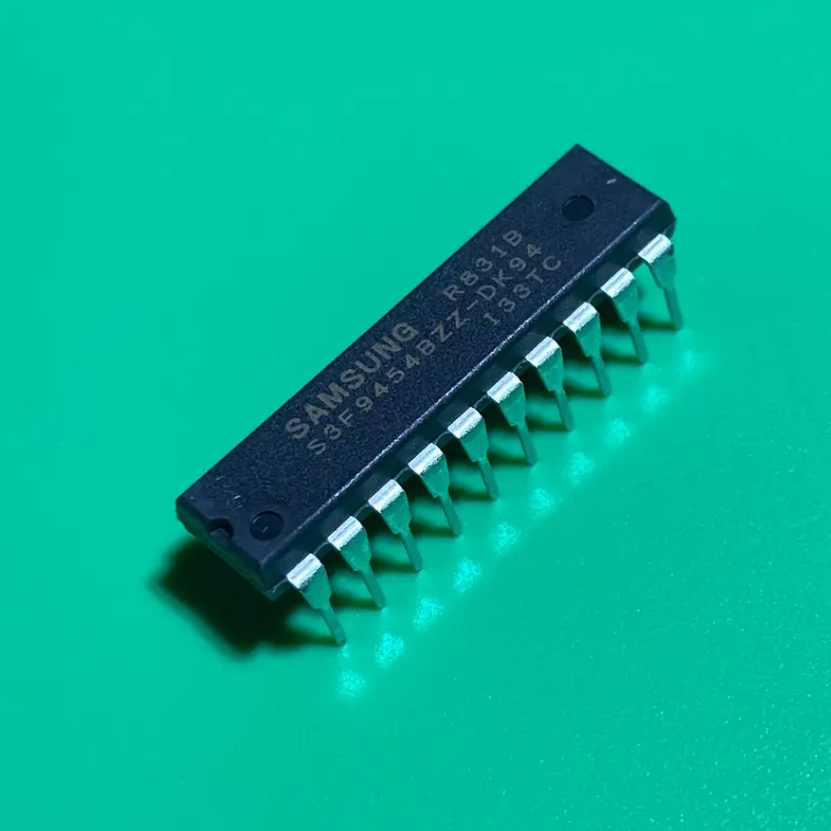
Break IC S3F9454B protective system and readout firmware from samsung Microcontroller S3F9454B, the format of firmware will be heximal which can be reprogramme to blank MCU S3F9454B flash memory;
The S3F9454B MCU is part of Samsung’s family of 8-bit microcontrollers built for embedded control in electronic appliances, automotive systems, industrial automation, and smart devices. Its key features include:
- Flash Memory for program storage
- Built-in EEPROM for non-volatile data retention
- Multiple I/O ports
- Internal oscillator
- Integrated ADCs for sensor input
- On-chip protection mechanisms against firmware read-back and duplication
These features make it ideal for compact applications, but they also complicate the process when original firmware is lost, or updates are required without access to source code.
OVERVIEW
The SAM88RCRI instruction set is designed to support the large register file. It includes a full complement of 8-bit arithmetic and logic operations. There are 41 instructions. No special I/O instructions are necessary because I/O control and data registers are mapped directly into the register file. Flexible instructions for bit addressing, rotate, and shift operations complete the powerful data manipulation capabilities of the SAM88RCRI instruction set after MCU STM32F107RCT6 code recovery.
REGISTER ADDRESSING
To access an individual register, an 8-bit address in the range 0-255 or the 4-bit address of a working register is specified. Paired registers can be used to construct 13-bit program memory or data memory addresses. For detailed information about register addressing, please refer to Chapter 2, “Address Spaces”.
ADDRESSING MODES
There are six addressing modes: Register (R), Indirect Register (IR), Indexed (X), Direct (DA), Relative (RA), and Immediate (IM). For detailed descriptions of these addressing modes, please refer to Chapter 3, “Addressing Modes” when microcontroller PIC16F684 firmware copying.
We provide a full suite of services to break the IC S3F9454B firmware and retrieve, duplicate, or clone the content from the chip’s flash, EEPROM, and program memory. Our process includes:
Secure IC Extraction: We physically and logically access the chip to extract firmware without damaging the original device.
Firmware Dumping: We open the locked firmware and retrieve heximal files, binary archives, and other secured memory data.
Decryption and Analysis: If the firmware is encrypted, we use advanced analysis and brute-force techniques to decrypt and decode it.
Disassembly & Decompilation: Our engineers can convert raw firmware into readable assembly language, and in many cases, reconstruct C/C++ source code for easier modification or reuse.
Duplication and Cloning: We can copy firmware from one device to another, creating working clones for replacement, testing, or legacy system replication.
Our clients range from electronics manufacturers and repair shops to researchers and security analysts. Common reasons to use our service include:
- Lost or corrupted firmware recovery
- Legacy system support where original source code is missing
- Competitive analysis or product teardowns
- Security audits and vulnerability research
- Product maintenance or feature expansion
With our support, companies can avoid costly delays, replace discontinued parts, or perform critical upgrades on systems where the firmware is locked and otherwise inaccessible.
Circuit Engineering Company Limited continues to be recognized as the Southern China Leader in Services for IC Break, MCU attack, Chip Recover, Microcontroller Copy service. With the advancement of today’s modern circuit board technology, it is more important than ever to have specialists available to help you at a moment’s notice. Our engineering and commercial teams collectively have a vast amount of electronic experience covering field include Consumer Electronics, Industrial Automation Electronics, Wireless Communication Electronics., etc. For more information please contact us through email.
Recover Microcontroller MC68HC908JB16 Firmware
Recover Microcontroller MC68HC908JB16 Firmware from flash memory include the program and data, the heximal file can be copied to new MCU MC68HC908JB16;
Recover Microcontroller MC68HC908JB16 Firmware from flash memory include the program and data, the heximal file can be copied to new MCU MC68HC908JB16
Features of the Microcontroller MC68HC908JB16 include the following:
High-performance M68HC08 architecture
Fully upward-compatible object code with M6805, M146805, and
M68HC05 families
Low-power design; fully static with stop and wait modes
6-MHz internal bus frequency
16,384 bytes of on-chip FLASH memory with security1 feature
384 bytes of on-chip random access memory (RAM)
Up to 21 general-purpose input/output (I/O) pins, including:
– 15 shared-function I/O pins
– 8-bit keyboard interrupt port
– 10mA high current drive for PS/2 connection on 2 pins (with USB module disabled)
– 1 dedicated I/O pin, with 25mA direct drive for infrared LED (32-pin package) if recover Microcontroller STM32F107RCT6 code
– 6 dedicated I/O pins, with 25mA direct drive for infrared LED on 2 pins and 10mA direct drive for normal LED on 4 pins (28-pin package)
Two 16-bit, 2-channel timer interface modules (TIM1 and TIM2) with selectable input capture, output compare, PWM capability on each channel, and external clock input option (TCLK)
Universal Serial Bus specification 2.0 low-speed functions:
– 1.5Mbps data rate
– On-chip 3.3V regulator
– Endpoint 0 with 8-byte transmit buffer and 8-byte receive buffer
– Endpoint 1 with 8-byte transmit buffer
– Endpoint 2 with 8-byte transmit buffer and 8-byte receive buffer
Serial communications interface module (SCI)
Dual clock generator modules (CGM) (32-pin package)
In-circuit programming capability using USB communication or standard serial link on PTA0 pin
System protection features:
– Optional computer operating properly (COP) reset
– Optional Low-voltage detection with reset
– Illegal opcode detection with reset
– Illegal address detection with reset
Master reset pin with internal pull-up and power-on reset
IRQ interrupt pin with internal pull-up and schmitt-trigger input
32-pin low-profile quad flat pack (LQFP) and 28-pin small outline
integrated circuit package (SOIC)
Features of the CPU08 include the following:
Enhanced HC05 programming model
Extensive loop control functions
16 addressing modes (eight more than the HC05)
16-bit index register and stack pointer
Memory-to-memory data transfers
Fast 8 × 8 multiply instruction
Fast 16/8 divide instruction
Binary-coded decimal (BCD) instructions
Optimization for controller applications
Third party C language support
Posted in Recover Chip |
Tags: recover microcontroller source bin, recover microcontroller source content, recover microcontroller source data, recover microcontroller source file, recover microcontroller source flash, recover microcontroller source hex, recover microcontroller source software |
Comments Closed
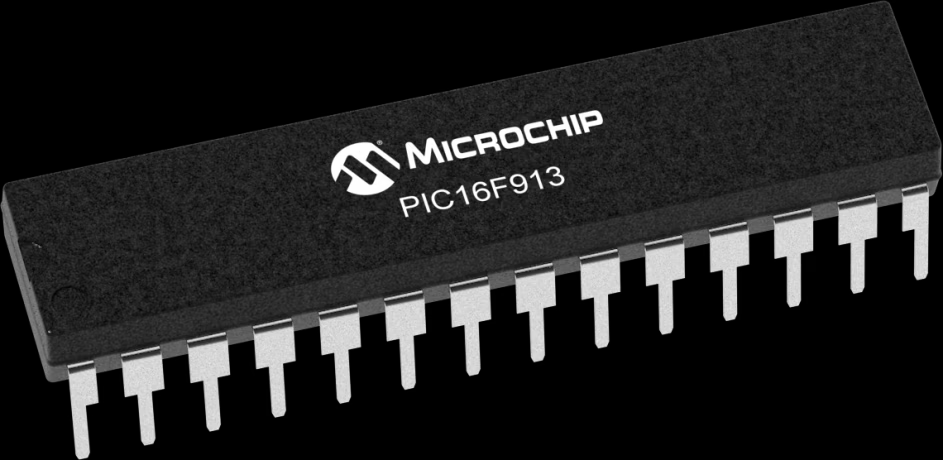
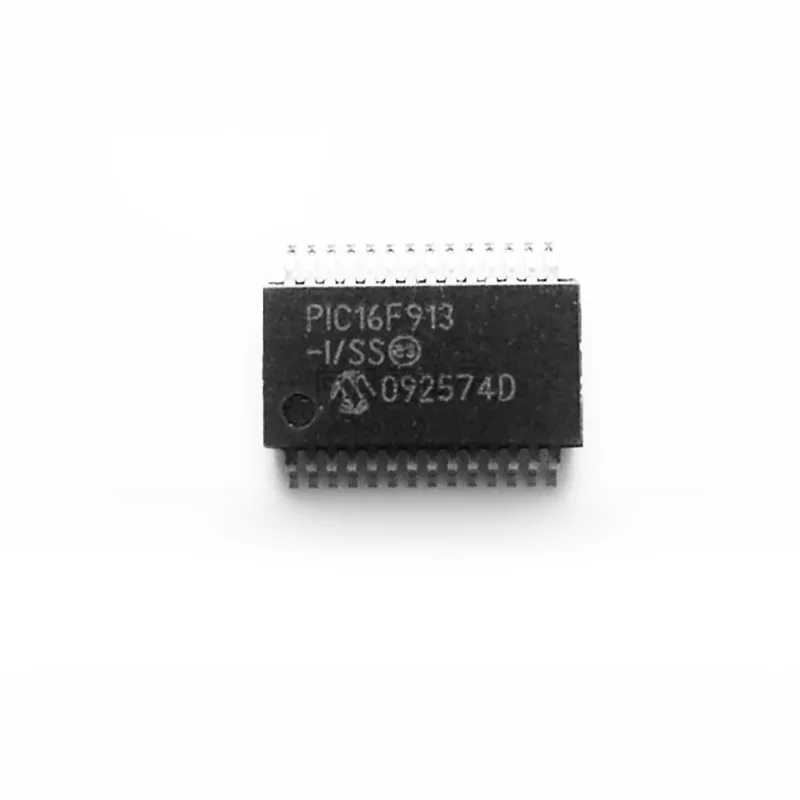
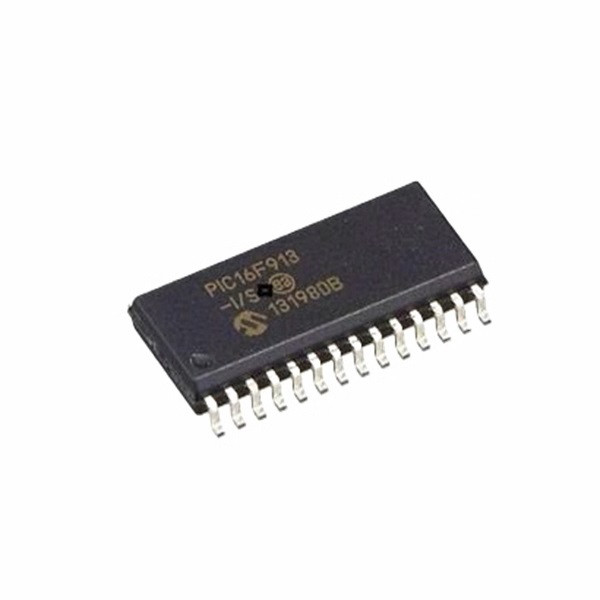
Recover Chip PIC16F913 Binary
When working with embedded systems, one of the most challenging tasks can be extracting or recovering chip PIC16F913 binary data. This microcontroller, produced by Microchip Technology, is commonly found in remote controls, industrial equipment, and sensor-based systems. Unlike many older or simpler microcontrollers, the PIC16F913 features advanced security mechanisms, making its firmware difficult to access or duplicate without specialized skills and tools.
Podczas pracy z systemami wbudowanymi jednym z najtrudniejszych zadań może być wyodrębnienie lub odzyskanie danych binarnych układu PIC16F913. Ten mikrokontroler, wyprodukowany przez Microchip Technology, jest powszechnie spotykany w pilotach zdalnego sterowania, sprzęcie przemysłowym i systemach opartych na czujnikach. W przeciwieństwie do wielu starszych lub prostszych mikrokontrolerów, PIC16F913 posiada zaawansowane mechanizmy bezpieczeństwa, co utrudnia dostęp do jego oprogramowania układowego lub jego kopiowanie bez specjalistycznych umiejętności i narzędzi.
At CIRCUIT ENGINEERING CO.,LTD we offer professional services to read out, restore, and recover PIC16F913 binaries, whether for software migration, security auditing, or backup purposes. Our process allows clients to unlock, decode, and decrypt protected memory, giving full access to the firmware, EEPROM, or flash data stored inside the microcontroller.
What Makes PIC16F913 Unique?
Compared to simpler chips like the PIC16C554 or PIC12CE519, the PIC16F913 includes:
Extended instruction set (Mid-Range architecture) with more advanced features.
Integrated LCD driver module, making it more common in display-based applications.
More robust memory protection, including locked and encrypted flash/eeprom blocks, making unauthorized binary readouts or program duplication more difficult.
تحليل ثنائي وفك تشفير البرامج الثابتة بمجرد استخراجها، تُحلل الملفات الثنائية أو السداسية لتحديد أنماط التعليمات، ومقاطع البيانات، والهياكل المنطقية. ثم يقوم فريقنا بفك تشفير أرشيف البرامج الثابتة، وإعادة بناء تسلسل الكود الأصلي ومنطقه. استعادة البرامج الثابتة واستعادة الكود المصدري عند الحاجة، نستعيد الكود المصدري من الملف الثنائي المفكك. على الرغم من أن ملف البرنامج المستعاد قد لا يتطابق تمامًا مع الكود الأصلي المكتوب بلغة C، إلا أنه يوفر تمثيلًا قابلاً للاستخدام والقراءة، ويمكن تعديله أو نسخه حسب الحاجة. الاستنساخ والنسخ بعد استعادة البيانات، نساعد عملائنا على استنساخ أو نسخ البرامج الثابتة على شرائح أو أجهزة جديدة. سواءً للنسخ الاحتياطي أو الإنتاج، يتيح هذا النسخ الكامل للبرنامج الأصلي المؤمّن.
On-board comparators, analog modules, and enhanced I/O, increasing complexity of its firmware structure.
This chip’s secured and embedded firmware is designed to prevent unauthorized duplication or tampering. However, with the right techniques, even protected programs and data archives can be successfully recovered.
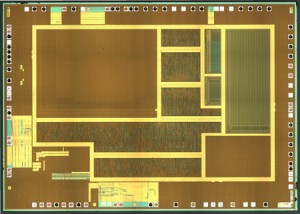
Recover Chip PIC16F913 Binary is a process of dumping heximal from MCU’s PIC16F913 flash memory, the status of Microcontroller PIC16F913 can be changed from locked to open by MCU Cracking technique
Recover Chip PIC16F913 Binary is a process of dumping heximal from MCU’s PIC16F913 flash memory, the status of Microcontroller PIC16F913 can be changed from locked to open by MCU Cracking technique;
High-Performance RISC CPU:
· Only 35 instructions to learn:
– All single-cycle instructions except branches
· Operating speed:
– DC – 20 MHz oscillator/clock input
– DC – 200 ns instruction cycle
· Program Memory Read (PMR) capability
· Interrupt capability
· 8-level deep hardware stack
· Direct, Indirect and Relative Addressing modes
Special Microcontroller Features:
· Precision Internal Oscillator:
– Factory calibrated to ±1%, typical
– Software selectable frequency range of
8 MHz to 125 kHz
– Software tunable
– Two-Speed Start-up mode
– External Oscillator fail detect for critical applications
– Clock mode switching during operation for power savings
· Software selectable 31 kHz internal oscillator
· Power-Saving Sleep mode
· Wide operating voltage range (2.0V-5.5V)
· Industrial and Extended temperature range
· Power-on Reset (POR)
· Power-up Timer (PWRT) and Oscillator Start-up
Timer (OST)
· Brown-out Reset (BOR) with software control option
· Enhanced Low-Current Watchdog Timer (WDT) with on-chip oscillator (software selectable nominal 268 seconds with full prescaler) with software enable
· Multiplexed Master Clear with pull-up/input pin
· Programmable code protection
· High-Endurance Flash/EEPROM cell:
– 100,000 write Flash endurance
– 1,000,000 write EEPROM endurance
– Flash/Data EEPROM retention: > 40 years
Quando si lavora con sistemi embedded, uno dei compiti più impegnativi può essere l’estrazione o il recupero dei dati binari del chip PIC16F913. Questo microcontrollore, prodotto da Microchip Technology, è comunemente presente in telecomandi, apparecchiature industriali e sistemi basati su sensori. A differenza di molti microcontrollori più vecchi o più semplici, il PIC16F913 è dotato di meccanismi di sicurezza avanzati, che rendono il suo firmware difficile da accedere o duplicare senza competenze e strumenti specializzati.
Low-Power Features:
· Standby Current:
– <100 nA @ 2.0V, typical
· Operating Current:
– 11 ìA @ 32 kHz, 2.0V, typical
– 220 ìA @ 4 MHz, 2.0V, typical
· Watchdog Timer Current:
– 1 ìA @ 2.0V, typical
Peripheral Features:
· Liquid Crystal Display module:
– Up to 60/96/168 pixel drive capability on 28/40/64-pin devices, respectively
– Four commons
· Up to 24/35/53 I/O pins and 1 input-only pin:
– High-current source/sink for direct LED drive
– Interrupt-on-change pin
– Individually programmable weak pull-ups
· In-Circuit Serial Programming™ (ICSP™) via two pins
· Analog comparator module with:
– Two analog comparators
– Programmable on-chip voltage reference (CVREF) module (% of VDD)
– Comparator inputs and outputs externally accessible
· A/D Converter:
– 10-bit resolution and up to 8 channels
· Timer0: 8-bit timer/counter with 8-bit
programmable prescaler
· Enhanced Timer1:
– 16-bit timer/counter with prescaler
– External Timer1 Gate (count enable)
– Option to use OSC1 and OSC2 as Timer1 oscillator if INTOSCIO or LP mode is selected
· Timer2: 8-bit timer/counter with 8-bit period register, prescaler and postscaler
· Addressable Universal Synchronous
Asynchronous Receiver Transmitter (AUSART)
· Up to 2 Capture, Compare, PWM modules:
– 16-bit Capture, max. resolution 12.5 ns
– 16-bit Compare, max. resolution 200 ns
– 10-bit PWM, max. frequency 20 kHz
· Synchronous Serial Port (SSP) with I2C™
Posted in Recover Chip |
Tags: recover chip encrypted binary, recover chip encrypted content, recover chip encrypted data, recover chip encrypted file, recover chip encrypted flash, recover chip encrypted heximal, recover chip encrypted software, екстрахирам интегрална схема entsrapted bin, екстрахирам интегрална схема entsrapted code, екстрахирам интегрална схема entsrapted data, екстрахирам интегрална схема entsrapted eeprom, екстрахирам интегрална схема entsrapted file, екстрахирам интегрална схема entsrapted firmware, екстрахирам интегрална схема entsrapted flash, екстрахирам интегрална схема entsrapted hex, екстрахирам интегрална схема entsrapted memory, екстрахирам интегрална схема entsrapted program, екстрахирам интегрална схема entsrapted software |
Comments Closed