 Recover Chip PIC16F83 Eeprom: Reading a Part That Lost Power Mid-Write
 March 24th, 2010 |
 Author:
Most recovery work starts from a device that is either working or dead. This part produces a third category that is more interesting: a device that is alive, responds to the programming interface, returns a full image, and behaves wrongly. The image is a mixture of old content, new content, erased rows and partially erased cells, and the job is to read that mixture correctly rather than to assume the read failed.
The PIC16F83 is the smaller member of the classic eighteen-pin flash pair: 512 by 14 bits of program memory, 64 bytes of data EEPROM, a few dozen bytes of RAM, one timer, no converter. It was designed into timers, chargers, access control and small appliances, and a fair number of those designs used self-programming — the device rewriting part of its own flash during operation, or writing its EEPROM at the end of a production test.
Self-programming is what makes the interrupted state a real case rather than a theoretical one.
What an interruption actually leaves
Flash erase works in blocks. A write works in words. Between the start of an erase and the completion of the write that follows it, the array is in a state that has no valid interpretation as program content.
| State | What the cells read | How it appears in a listing |
|---|---|---|
| fully erased | all ones | blank, expected after erase |
| fully written | intended value | normal code |
| erase interrupted | a rising pattern of ones across the row | runs of 0x3FF with occasional valid words |
| write interrupted | value between erased and target | words that decode to implausible instructions |
| EEPROM write interrupted | mixture of old and new bytes | settings that fail consistency checks |
The third row is the giveaway. On a 14-bit word, an erase that stops partway leaves some cells at one and some at zero, and the resulting word is usually a value with a high run of ones — 0x3FF, 0x3FE, 0x3FC, 0x3F8. A region where these appear in sequence, mixed with genuine instructions, is not corruption from a bad read. It is a physical record of where the erase stopped.
Why the read is usually still valid
It is worth stating plainly, because customers often assume otherwise: an image containing a half-erased region is a correct read of a damaged device. The programming interface reports what the cells hold, and if the cells are in an intermediate state, the image contains intermediate values.
That distinction changes the deliverable. What the customer needs is not a repaired image but a map of which regions are trustworthy. An image that has been “cleaned” — intermediate values replaced with blank or with a plausible guess — has destroyed the only evidence of what happened.
The 64 bytes that often explain the failure
On this part the data EEPROM is 64 bytes, and the code frequently writes it during operation: a run counter, a setpoint changed by the user, a state that must survive power loss. A write to EEPROM takes milliseconds, and a supply that collapses during that window leaves a byte that is neither the old nor the new value.
The signature is localised: one byte, or a short run within a row, whose value is inconsistent with the surrounding structure. A setpoint of 20 stored next to a setpoint of 200 with a value of 148 in between is an interrupted write, not an encoding.
Reading the EEPROM before anything else is the rule, because it is the block most likely to have been mid-write when the failure occurred, and it is the block whose content the customer most often wants back.
The program array: boundary and blank tail
512 words is small enough that the whole array can be read and inspected. Two boundary facts matter.
The configuration word sits at the top of the map, and on this family the last program word may also carry a factory calibration value for the internal oscillator. A read that treats the top word as configuration only will discard the calibration; a read that treats it as program only will program the wrong configuration.
The blank tail between the end of the code and the configuration word reads as all ones. It is not empty in the sense of “nothing was here” — it is erased, which is a state the array was put into deliberately at manufacture.
Telling a bad read from a bad device
| Observation | Likely cause | Next step |
|---|---|---|
| every word identical | read inhibited or interface fault | check protection state, then die |
| word zero not a jump | wrong word convention | reconvert the file |
| one region with rising-one patterns | interrupted erase | map the region, deliver as damaged |
| scattered implausible words | marginal read timing | re-read at lower clock |
| image verifies but device misbehaves | missing calibration or config | re-read the top word |
The fourth row is worth trying before any physical work. On an old device with a tired interface, lowering the programming clock often converts a noisy read into a clean one, and it costs nothing.
What a recovery on this part should contain
The full 512-word image including the top word, with the word convention stated. The configuration fields decoded. The 64 bytes of EEPROM raw, plus a note identifying which bytes look interrupted and why. And a region map marking addresses that read as intermediate values rather than as code or blank.
That map is the part that lets the customer decide whether the design is repairable: a program whose main loop is intact and whose configuration block is damaged is a candidate for reconstruction, while a program whose interrupt handler is half erased is not.
Where a larger part in the same family shows how the EEPROM contents drive the design’s behaviour, PIC16F84 code breaking covers the two-customer problem. Where the same small array is OTP and therefore cannot be half erased at all, PIC12F508 code recovery sets out the different failure set. And where the interrupted region must be reconstructed from behaviour rather than read, PIC12CE518 binary recovery describes that path.
The short version
An interrupted write produces an image that is correctly read and partly invalid. Do not clean it. Map it: which words are code, which are intermediate, which bytes of the EEPROM were mid-write, and which part of the map can be trusted. That map is the deliverable.
 Posted in

Break MCU: Four Different Deliverables Hiding Behind One Verb
A request that begins with “we need this MCU broken” almost never means one thing. In practice it means one of four things, and the four are not points on a scale of difficulty. They are different products. Two of them are compatible with each other. Two of them are mutually exclusive with almost everything else. The reason this matters commercially is that the phrase “break MCU” is quoted as if it were a single line item, and the misunderstanding only surfaces after the sample has been opened.
The four outcomes are: a raw bit image of the memory, a loadable image that will run on a replacement part, a maintainable engineering project that can be edited and rebuilt, and a written behavioural specification of what the device does. A fifth outcome, a working clone, is sometimes implied but is a manufacturing problem rather than an extraction problem. Sorting a request into one of these four before touching the part is the entire discipline.
The four outcomes and what each one consumes
| Deliverable | What the customer receives | What it costs irreversibly |
|---|---|---|
| Raw bit image | A binary or hex file, no interpretation | The protection state of the sample, often the sample itself |
| Loadable image | A file that programs a blank part and boots | The sample, plus any calibration unique to it |
| Engineering project | Disassembly, recovered structure, buildable source | The sample, plus weeks of interpretation |
| Behavioural specification | Timing, protocols, state transitions, no code | Usually nothing; often obtainable without opening the part |
The right-hand column is the part nobody asks about at quotation time. A raw image and a loadable image are close relatives: both come from the same read, and the difference is whether the address map and the configuration bytes were captured along with the code. An engineering project starts from either of those and adds interpretation, which is where the schedule goes. A behavioural specification may require none of the above and can sometimes be produced from a logic analyser and a bench full of stimulus.
Why “unlock” and “read out” cannot both be satisfied
The single most common impossible request is to remove the protection and keep the contents. On most flash-based microcontrollers, the protection is stored in the same non-volatile block as the code, and the only primitive that clears it is a full erase. The erase is not selective. It clears the lock and the code in one operation, because both are the same kind of cell.
This is not a vendor trick. It is what the silicon can do. A protection bit that could be cleared without disturbing its neighbours would be a protection bit an attacker could clear, which defeats its purpose. So the design choice is forced: either the lock survives an erase, or the erase takes everything.
Once that is understood, the request decomposes. If the customer needs the code, the route is a read that was never authorised by the lock — a physical or side-channel route. If the customer needs a working unlocked part, the route is an erase, and the code is gone by definition. Restoring embedded information covers what can still be salvaged in the second case, which is more than most people expect but never includes the original program.
Identity before method
Every method choice depends on facts that are settled before any tool is connected. Whether the die is flash, OTP or mask ROM changes everything: mask ROM has no erase primitive at all, so the “unlock” conversation does not apply. Whether the package is plastic or ceramic changes the physical route. Whether the part is a genuine device or a remarked clone changes what the read even means.
| Question | Why it decides the method |
|---|---|
| Flash, OTP or mask ROM? | Only flash has an erase path; OTP and mask are read-only by construction |
| Protection in the array or in a separate fuse block? | Separate fuses can sometimes be isolated; in-array bits cannot |
| Debug port disabled or merely unprotected? | A disabled port may still respond to a specific entry sequence |
| Single die or stacked package? | Stacked packages change which surface is reachable |
A wrong answer to the first row sends the whole project down a road that does not exist. This is why a competent first response to “break MCU” is a set of questions about the part number, the package marking and the failure mode, not a price.
The read is not the deliverable
A read that produces bytes has proved almost nothing. The bytes must be shown to be a coherent image: a vector table at a plausible address, a stack pointer that points into RAM, checksums that close, strings that decode, and code that disassembles into a plausible instruction mix rather than noise. An image that fails these tests is either a partial read, a read through a protection mechanism that returns a decoy pattern, or a read of the wrong address window.
The decoy case deserves emphasis. Some devices return all zeros or all ones when a protected region is read, and a naive pipeline will happily write that out as a file. A file of uniform bytes is not evidence of an empty device. It is evidence that the read was refused, and the refusal looks exactly like data unless somebody checks.
Where interpretation starts
The jump from a loadable image to an engineering project is the point where the work stops being extraction and becomes analysis. Tools can produce a disassembly in minutes. Producing something a firmware engineer can maintain takes longer, because the losses are structural: register allocation is gone, inlined functions have no call site, macros have been expanded, and the optimiser has reordered blocks. Cracking microcontroller source code sets out those four losses and what can be reconstructed around them.
The honest framing is that the deliverable is a reconstruction, not a recovery. It will compile, it will behave, and it will not be the original file. Projects that expect the original file are projects that will be disappointed at delivery, no matter how well the work was done.
Matching the route to the family
Different families fail in different places, and the failure mode is the most useful thing to know before starting. On Microchip’s 8-bit parts the decisive interaction is between row erase and the code protect bit, which is covered in attacking Microchip MCU firmware. On ARM parts it is usually the debug authentication rather than the flash lock. On CPLD and FPGA the object being read is a configuration pattern rather than a program, and the vocabulary of “firmware” starts to mislead.
A single intake form that records family, package, protection state, observed behaviour and the required deliverable will route a request correctly in most cases. The same form filled in badly produces a quotation that cannot be honoured. Where the chosen route is the classic one of isolating the protection structure on the die, MCU break describes that procedure in the narrow sense the phrase originally carried.
Services at this boundary
Work in this area covers session readout where the port still answers, physical extraction where it does not, image validation before delivery, and reconstruction of a buildable project from a validated image. It does not cover recovering contents that a full erase has already destroyed, and it does not cover clearing a protection bit while preserving the data it protected, because on the parts where that matters the two share the same cells.
The useful conversation is therefore short: what is the part, what state is it in, and which of the four deliverables does the project need. Everything else follows from those three answers.
Reverse Engineering Microcontroller PIC16C716 Heximal
Reverse engineering Microcontroller PIC16C716 can locate the security fuse bit of it, and break off it in order to take the embedded software from mcu pic16c716, and then copy the microprocessor pic16c716 program out to new MCU;
Reverse engineering Microcontroller PIC16C716 can locate the security fuse bit of it, and break off it in order to take the embedded software from mcu pic16c716, and then copy the microprocessor pic16c716 program out to new MCU
There are two memory blocks in each of these PICmicro® microcontroller devices. Each block (Program Memory and Data Memory) has its own bus so that concurrent access can occur.
Additional information on device memory may be found in the PICmicro Mid-Range Reference Manual, (DS33023).
The PIC16C712/716 has a 13-bit program counter capable of addressing an 8K x 14 program memory space. PIC16C712 has 1K x 14 words of program memory and PIC16C716 has 2K x 14 words of program memory. Accessing a location above the physically implemented address will cause a wraparound.
The reset vector is at 0000h and the interrupt vector is at 0004h.
Each bank extends up to 7Fh (128 bytes). The lower locations of each bank are reserved for the Special
Function Registers. Above the Special Function Registers are General Purpose Registers, implemented as static RAM. All implemented banks contain special function registers. Some “high use” special function registers from one bank may be mirrored in another bank for code reduction and quicker access.
The Special Function Registers are registers used by the CPU and Peripheral Modules for controlling the desired operation of the device. These registers are implemented as static RAM. A list of these registers is give in Table 2-1 after attacking Microcontroller.
The special function registers can be classified into two sets; core (CPU) and peripheral. Those registers associated with the core functions are described in detail in this section. Those related to the operation of the peripheral features are described in detail in that peripheral feature section.
cracking secured mcu PIC16C716 flash memory and readout embedded flash memory binary and heximal file
The STATUS register, shown in Figure 2-4, contains the arithmetic status of the ALU, the RESET status and the bank select bits for data memory. The STATUS register can be the destination for any instruction, as with any other register. If the STATUS register is the destination for an instruction that affects the Z, DC or C bits, then the write to these three bits is disabled. These bits are set or cleared according to the device logic. Furthermore, the TO and PD bits are not writable. Therefore, the result of an instruction with the STATUS register as destination may be different than intended.
The program counter (PC) specifies the address of the instruction to fetch for execution. The PC is 13 bits wide. The low byte is called the PCL register after Reverse engineering Microcontroller. This register is readable and writable. The high byte is called the PCH register. This register contains the PC<12:8> bits and is not directly readable or writable. All updates to the PCH register go through the PCLATH register.
The stack allows a combination of up to 8 program calls and interrupts to occur. The stack contains the return address from this branch in program execution. Midrange devices have an 8 level deep x 13-bit wide hardware stack. The stack space is not part of either program or data space and the stack pointer is not readable or writable. The PC is PUSHed onto the stack when a CALL instruction is executed or an interrupt causes a branch. The stack is POPed in the event of a RETURN, RETLW or a RETFIE instruction execution when Reverse engineering Microcontroller.
PCLATH is not modified when the stack is PUSHed or POPed. After the stack has been PUSHed eight times, the ninth push overwrites the value that was stored from the first push. The tenth push overwrites the second push (and so on). The CALL and GOTO instructions provide 11 bits of address to allow branching within any 2K program memory page. When doing a CALL or GOTO instruction, the upper bit of the address is provided by PCLATH<3>.
unlock encrypted microcontroller pic16c716 flash memory and extract embedded firmware in the format of binary or heximal
When doing a CALL or GOTO instruction, the user must ensure that the page select bit is programmed so that the desired program memory page is addressed. If a return from a CALL instruction (or interrupt) is executed, the entire 13-bit PC is pushed onto the stack. Therefore, manipulation of the PCLATH<3> bit is not required for the return instructions (which POPs the address from the stack).
For example, CLRF STATUS will clear the upper-three bits and set the Z bit. This leaves the STATUS register as 000u u1uu (where u = unchanged).
Recover Microprocessor ATmega1281PA Flash
Recover Microprocessor ATmega1281PA Flash heximal file, copy mcu atmega1281pa memory content to new microcontroller and provide the same functions, the security fuse bit of microcontroller atmega1281pa will be cracked reset the status.
The FOCnA/FOCnB/FOCnC bits are only active when the WGMn3:0 bits specifies a non-PWM mode. When writing a logical one to the FOCnA/FOCnB/FOCnC bit, an immediate compare match is forced on the waveform generation unit.
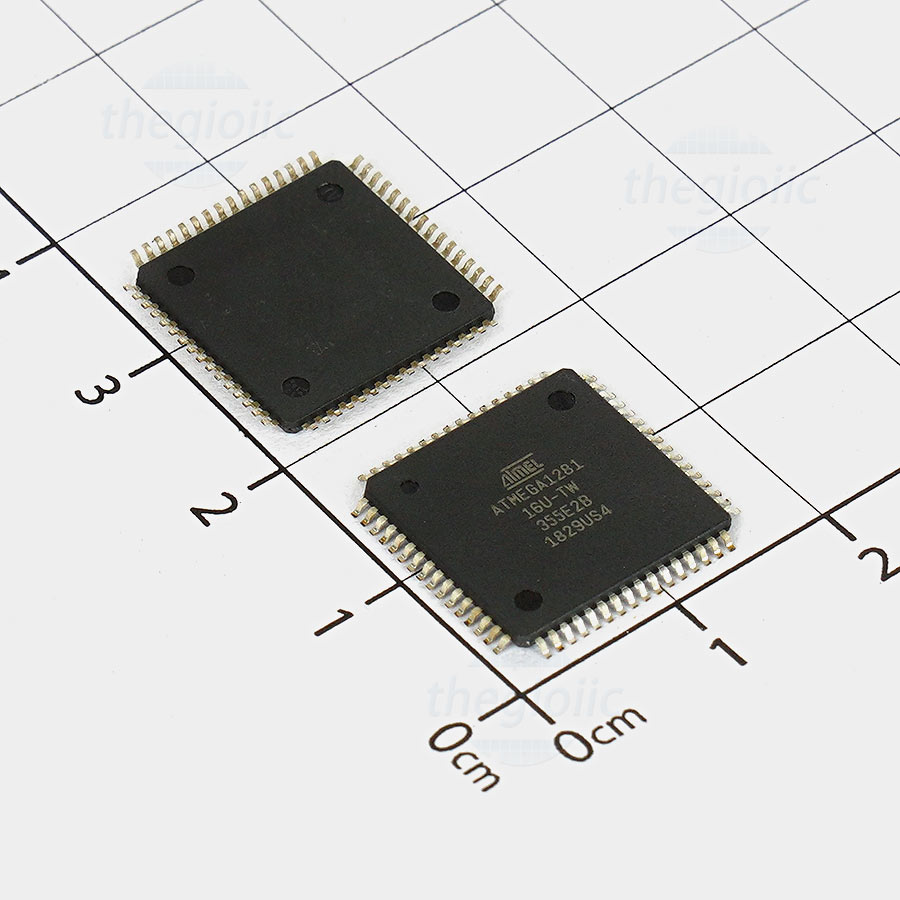
Recover Microprocessor ATmega1281PA Flash heximal file, copy mcu atmega1281pa memory content to new microcontroller and provide the same functions, the security fuse bit of microcontroller atmega1281pa will be cracked reset the status.
The OCnA/OCnB/OCnC output is changed according to its COMnx1:0 bits setting. Note that the FOCnA/FOCnB/FOCnC bits are implemented as strobes. Therefore it is the value present in the COMnx1:0 bits that determine the effect of the forced compare.
A FOCnA/FOCnB/FOCnC strobe will not generate any interrupt nor will it clear the timer in Clear Timer on Compare Match (CTC) mode using OCRnA as TOP before break microcontroller pic16f886.
unlock encrypted mcu atmega1281 microcontroller fuse bit and dump embedded firmware from flash memory and eeprom memory
The two Timer/Counter I/O locations (TCNTnH and TCNTnL, combined TCNTn) give direct access, both for read and for write operations, to the Timer/Counter unit 16-bit counter after Recover MICROPROCESSOR flash.
To ensure that both the high and low bytes are read and written simultaneously when the CPU accesses these registers, the access is performed using an 8-bit temporary High Byte Register (TEMP). This temporary register is shared by all the other 16-bit registers. See “Accessing 16-bit Registers” on page 137.
Modifying the counter (TCNTn) while the counter is running introduces a risk of missing a compare match between TCNTn and one of the OCRnx Registers when attacking dsp mcu texas instrument tms320f2401pg hex.
Writing to the TCNTn Register blocks (removes) the compare match on the following timer clock for all compare units. The Output Compare Registers contain a 16-bit value that is continuously compared with the counter value (TCNTn).
A match can be used to generate an Output Compare interrupt, or to generate a waveform output on the OCnx pin. The Output Compare Registers are 16-bit in size. To ensure that both the high and low bytes are written simultaneously when the CPU writes to these registers, the access is performed using an 8-bit temporary High Byte Register (TEMP).
recover secured microprocessor ATMEGA1281 flash memory and readout mcu embedded firmware from flash program memory and eeprom data memory
This temporary register is shared by all the other 16-bit registers. See “Accessing 16-bit Registers” on page 137. The Input Capture is updated with the counter (TCNTn) value each time an event occurs on the ICPn pin (or optionally on the Analog Comparator output for Timer/Counter1).
The Input Capture can be used for defining the counter TOP value. The Input Capture Register is 16-bit in size. To ensure that both the high and low bytes are read simultaneously when the CPU accesses these registers, the access is performed using an 8-bit temporary High Byte Register (TEMP).
This temporary register is shared by all the other 16-bit registers. See “Accessing 16-bit Registers” on page 137.
Break IC ATmega1281A Flash
Break IC ATmega1281A and copy microcontroller atmega128a Flash content in the format of heximal, the fuse bit of mcu atmega1281a will be unlocked by focus ion beam technique;
The Timer/Counter is a synchronous design and the timer clock (clkTn) is therefore shown as a clock enable signal in the following figures.
The figures include information on when Interrupt Flags are set, and when the OCRnx Register is updated with the OCRnx buffer value (only for modes utilizing double buffering). Figure 58 shows a timing diagram for the setting of OCFnx.
The COMnA1:0, COMnB1:0, and COMnC1:0 control the output compare pins (OCnA, OCnB, and OCnC respectively) behavior. If one or both of the COMnA1:0 bits are written to one, the OCnA output overrides the normal port functionality of the I/O pin it is connected to when recover chip atmega1281pv flash.
If one or both of the COMnB1:0 bits are written to one, the OCnB output overrides the normal port functionality of the I/O pin it is connected to.
If one or both of the COMnC1:0 bits are written to one, the OCnC output overrides the normal port functionality of the I/O pin it is connected to. However, note that the Data Direction Register (DDR) bit corresponding to the OCnA, OCnB or OCnC pin must be set in order to enable the output driver.
When the OCnA, OCnB or OCnC is connected to the pin, the function of the COMnx1:0 bits is dependent of the WGMn3:0 bits setting. Table 79 shows the COMnx1:0 bit functionality when the WGMn3:0 bits are set to a normal or a CTC mode (non-PWM) if recover mcu atmega169pa code.
Combined with the WGMn3:2 bits found in the TCCRnB Register, these bits control the counting sequence of the counter, the source for maximum (TOP) counter value, and what type of waveform generation to be used, see Table 82.
Modes of operation supported by the Timer/Counter unit are: Normal mode (counter), Clear Timer on Compare match (CTC) mode, and three types of Pulse Width Modulation (PWM) modes. (See “Modes of Operation” on page 147.).
recover atmega1281 microcontroller embedded firmware and crack atmega1281 mcu fuse bit
Setting this bit (to one) activates the Input Capture Noise Canceler. When the Noise Canceler is activated, the input from the Input Capture Pin (ICPn) is filtered. The filter function requires four successive equal valued samples of the ICPn pin for changing its output after recover chip atmega128apv source code.
The input capture is therefore delayed by four Oscillator cycles when the noise canceler is enabled.
This bit selects which edge on the Input Capture Pin (ICPn) that is used to trigger a capture event. When the ICESn bit is written to zero, a falling (negative) edge is used as trigger, and when the ICESn bit is written to one, a rising (positive) edge will trigger the capture.
When a capture is triggered according to the ICESn setting, the counter value is copied into the Input Capture Register (ICRn). The event will also set the Input Capture Flag (ICFn), and this can be used to cause an Input Capture Interrupt, if this interrupt is enabled.
When the ICRn is used as TOP value (see description of the WGMn3:0 bits located in the TCCRnA and the TCCRnB Register), the ICPn is disconnected and consequently the input capture function is disabled.
The FOCnA/FOCnB/FOCnC bits are only active when the WGMn3:0 bits specifies a non-PWM mode. When writing a logical one to the FOCnA/FOCnB/FOCnC bit, an immediate compare match is forced on the waveform generation unit.
Reverse Engineering MCU ATmega1281P Firmware
Reverse Engineering MCU ATmega1281P and copy embedded Firmware from microcontroller atmega1281p memory to new MCU, to make microprocessor atmega1281p cloning units.
The Timer/Counter Overflow Flag (TOVn) is set at the same timer clock cycle as the OCRnx Registers are updated with the double buffer value (at BOTTOM).
When either OCRnA or ICRn is used for defining the TOP value, the OCnA or ICFn Flag set when TCNTn has reached TOP. The Interrupt Flags can then be used to generate an interrupt each time the counter reaches the TOP or BOTTOM value.
When changing the TOP value the program must ensure that the new TOP value is higher or equal to the value of all of the Compare Registers. If the TOP value is lower than any of the Compare Registers, a compare match will never occur between the TCNTn and the OCRnx before attack microcontroller mc68hc705p6a memory.
As Figure 57 shows the output generated is, in contrast to the phase correct mode, symmetrical in all periods. Since the OCRnx Registers are updated at BOTTOM, the length of the rising and the falling slopes will always be equal. This gives symmetrical output pulses and is therefore frequency correct.
Using the ICRn Register for defining TOP works well when using fixed TOP values. By using ICRn, the OCRnA Register is free to be used for generating a PWM output on OCnA before copying pic16lf877 MCU program.
However, if the base PWM frequency is actively changed by changing the TOP value, using the OCRnA as TOP is clearly a better choice due to its double buffer feature.
In phase and frequency correct PWM mode, the compare units allow generation of PWM waveforms on the OCnx pins. Setting the COMnx1:0 bits to two will produce a non-inverted PWM and an inverted PWM output can be generated by setting the COMnx1:0 to three.
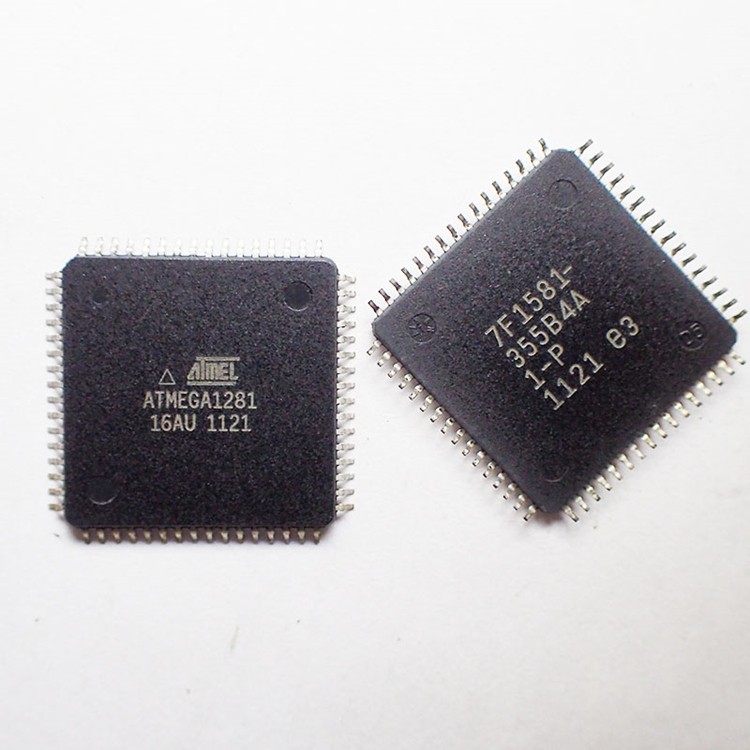
crack locked microcontroller ATMEGA1281 memory and clone its heximal file from program flash and data eeprom
The actual OCnx value will only be visible on the port pin if the data direction for the port pin is set as output (DDR_OCnx). The PWM waveform is generated by setting (or clearing) the OCnx Register at the compare match between OCRnx and TCNTn when the counter increments, and clearing (or setting) the OCnx Register at compare match between OCRnx and TCNTn when the counter decrements.
The PWM frequency for the output when using phase and frequency correct PWM can be calculated by the following equation:
The N variable represents the prescaler divider (1, 8, 64, 256, or 1024). The extreme values for the OCRnx Register represents special cases when generating a PWM waveform output in the phase correct PWM mode.
If the OCRnx is set equal to BOTTOM the output will be continuously low and if set equal to TOP the output will be set to high for non-inverted PWM mode. For inverted PWM the output will have the opposite logic values. If OCR1A is used to define the TOP value (WGM13:0 = 9) and COM1A1:0 = 1, the OC1A output will toggle with a 50% duty cycle.
ATmega1281PV: What Source Code From a Hex Image Can and Cannot Be
The phrase “source code recovery” describes a real activity and a misunderstanding at the same time. What comes out of a device is machine code: instructions and data at addresses. What a compiler produced it from is gone — names, types, structure, comments, the reasoning behind a decision.
Between those two things sits a process of inference. It is genuinely useful and it has hard limits, and both are worth stating precisely, because a customer who expects compilable C from a hex file will be disappointed by an honest answer and misled by a confident one.
What the instruction stream preserves
A large amount of structure survives compilation, because the compiler had to encode it:
- Function boundaries. Call and return pairs delimit them, even without symbols. The prologue that saves registers is a recognisable pattern.
- Control flow. Branches, loops, and jump tables are all explicit. A state machine produces a characteristic dispatch table.
- Data layout. Structures that appear in more than one function are visible as repeated offset patterns from the same base register.
- Constants. Magic numbers, thresholds, and string literals are all present verbatim.
From that, a competent reconstruction produces something that compiles and behaves identically. On a well-structured program, the result is often close to the original in shape.
What is destroyed
Four things are gone and no amount of analysis brings them back:
| Lost | Why it cannot be recovered |
|---|---|
| Identifier names | Not encoded; the compiler discarded them |
| Type information | Reduced to sizes and access widths |
| Comments and intent | Never in the binary |
| Optimisations applied | The source-level structure that motivated them |
The second row is subtler than it looks. A 16-bit value and a two-element byte array assemble identically. A signed comparison and an unsigned one differ by one instruction and by nothing else. The reconstructed code will be correct and may be misleading about what the designer meant.
Why this still matters commercially
Three legitimate uses, each with a different standard of success:
Understanding a protocol. The byte sequence a device accepts and the checks it performs are fully recoverable from behaviour plus code. Names are irrelevant; the state machine is the deliverable.
Reproducing a device. A build that meets the same specification is often the goal, not a byte-identical one. Reconstructed code that compiles and passes the same tests achieves it.
Establishing what a product does. The question is whether a device performs an operation, not how elegantly. That question is answered by the presence of an algorithm, not by its naming.
None of those require source code in the sense a developer means. All of them are commonly described as source code recovery, which is where the confusion starts.
The part with no external bus
This member is the variant without an external memory interface. That matters here for a specific reason: the entire program lives in one contiguous internal array, so the image is complete in a way it would not be on a bus-equipped sibling.
It also means there is no bus configuration in the start-up code to reconstruct, and no possibility that part of the logic sits in an external chip. The scope of the reconstruction is unambiguous, which is a genuine advantage when the deliverable is meant to be complete.
Working order for a reconstruction
The sequence that produces something defensible:
- Read signature, fuses, lock byte. Establishes the die and the protection state.
- Read the full array with page-level verification.
- Identify the vector table and the reset path. This fixes the address base and the compiler’s vector convention.
- Locate the string cluster. Strings are the fastest route to orienting within an image and often reveal the protocol and the product name.
- Reconstruct functions outward from strings and from peripheral register access, which is where the code touches hardware and therefore where behaviour is anchored.
- Cross-check every reconstructed function against observed device behaviour.
Step 6 is what separates a plausible reconstruction from a verified one. Machine code can be reconstructed into something that compiles and is wrong; behaviour is the only oracle that does not lie.
What to tell a customer
The honest framing is short. The image is complete and verified. The program can be reconstructed into compilable form and its behaviour reproduced. The original source, its names, its structure and its comments are not in the device and cannot be extracted from it.
That is not a limitation of a particular method. It is a property of compilation, and any claim to the contrary is describing something other than what is in the silicon.
Related notes
- ATmega1280PV and the three-byte counter — the sibling with an external bus.
- ATmega1280P and the EEPROM array — where the per-unit data lives.
- ATmega640 and partial images — when the image is genuinely incomplete.
FAQ
Can a hex file be decompiled into exact C? No. It can be reconstructed into C that compiles and behaves the same. Names, types and comments are not in the binary.
Is the reconstruction legally usable? That depends on jurisdiction and on the purpose. The technical question and the legal question are separate and both need answering.
Why do reconstructed names look arbitrary? Because they are. A function is named for what it does, which is inferred from what it touches, not from what the author called it.
Does the absence of an external bus help? Yes. It guarantees the internal image is the whole program, which removes one source of incompleteness.
Conclusion
Recovering source code means reconstructing behaviour from machine code, and the reconstruction is bounded by what compilation preserves. Control flow, constants and data layout survive; names, types and intent do not. Stating that boundary accurately is more useful than promising a developer’s source tree that the silicon never contained.
ATmega169A: Finding a Segment Table in a Flat File
A flat binary has no sections, no labels, no boundaries. Everything that a linker knew has been thrown away, and what remains is bytes in order. Finding a table in that is a matter of recognising shape rather than of reading a header.
On a display product the largest table has a distinctive shape, and learning to see it makes the rest of the image legible.
The shape of a segment table
A character table maps an index to a bit pattern. Three properties make it findable:
Fixed stride. Entries are the same size, because the register layout does not change between characters. A stride of a few bytes repeated a few dozen times is a table.
Low entropy in the high bits. Only some bits of each entry correspond to connected segments. The rest are zero, which makes the entries look like small numbers with a regular spacing.
Monotone index nearby. The code that reads the table increments an index, which appears as a short loop with a bounded counter.
| Property | What it looks like in a hex view |
|---|---|
| Fixed stride | Repeating pattern every N bytes |
| Sparse bits | Many 00 bytes interleaved with small values |
| Bounded values | Most entries below a threshold |
| Neighbouring index | A loop counter with a small limit |
Why display tables are larger than they need to be
A digit needs perhaps seven segments. A display with four digits, several annunciators and a couple of icons needs a table of a few dozen entries, each holding a pattern spread across backplane phases.
Because the pattern is distributed rather than contiguous, each entry is wider than the visible information requires. That is what produces the sparse, regular look — and it is also why the table is bigger than an outsider would expect.
Reading around the table
Once a candidate is found, three checks confirm it:
- The number of entries matches the number of displayable symbols, including blanks and error states.
- Extracting the entries and rendering them reproduces the visible characters.
- The code that indexes it also handles the decimal point or a leading-zero blanking case.
The third is the strongest. A table used for a display has special-case handling for the blank and for the decimal point, and that handling is code adjacent to the lookup.
What the flat file hides and what it cannot hide
It hides addresses, section order, and the distinction between code and data. It cannot hide the internal structure of data, because the structure is what the data is.
That is the general principle for reading a binary: look for repetition, look for stride, look for bounded values, and look for the code that indexes them. Those four signals find tables in any image, regardless of architecture.
The revision question
The A suffix marks a die revision. It may change the signature byte and a few analogue behaviours, and it does not change the table shape.
What it can change is the contrast constant that sits near the table, which is why a table extracted from one revision and applied to another may render correctly and look different. Recording the revision with the table prevents that being discovered in the field.
Reading order
- Signature, fuses, lock byte.
- Array read, verified — a flat file with one wrong byte corrupts a table silently.
- Locate repeated structures by stride.
- Confirm each candidate against the visible display.
- Record the table with the revision and the contrast constant.
Step 5 is the packaging that makes the result usable. A table without its revision and contrast is a fragment, and fragments get applied to the wrong device.
Related notes
- ATmega169PA and the driver — how the table is consumed.
- ATmega169PV and display fuses — the settings outside the file.
- ATmega640PV and binary offsets — the general problem of flat files.
FAQ
How do I know a table’s stride? By measuring the distance between repeated patterns in a hex view.
Can a table be mistaken for code? Rarely. Code has varied structure; tables repeat.
Why does one wrong byte matter so much? Because a table has no checksum and no redundancy. One bad entry renders one wrong character.
Does the revision change the table? Usually not. It can change the contrast value next to it.
Conclusion
A flat binary still contains structure, because structure is a property of the data rather than of the file. Fixed stride, sparse bits, bounded values and a nearby index are enough to find a segment table — and confirming it against the visible display turns a guess into a verified reconstruction.
Recover MCU R5F562T6BDFF Binary: A Flat File With No Map Is a File You Have to Prove
Of the file formats a recovery can deliver, the binary is the most portable and the least self-describing. It is a sequence of bytes. It does not say where they came from, how long they should be, or what order they are in. Everything it does not say has to be established some other way and then written down next to the file.
On an RX62T that is entirely workable, because the architecture places its reset vector at the very top of the four-gigabyte address space. The last four bytes of a correct image are an address, and an address is a falsifiable claim. This single property turns the binary from an unverifiable blob into something that can be checked in ten seconds.
The part is R5F562T6BDFF#V3 — RX62T group, one of the two memory classes the group offers, QFP-type package, version code after the hash. The version code affects paperwork rather than silicon, which means the length of the array is decided by the memory class field and not by the suffix.
What a binary omits
| property | in an S-record or HEX file | in a binary |
|---|---|---|
| start address | in every record | assumed, and must be agreed |
| length | implied by the highest address used | exactly the file size, which may be wrong |
| gaps | expressed as absent records | indistinguishable from zero-filled memory |
| endianness | not expressed, but the bytes are positioned | not expressed |
| integrity | per-record checksum | none |
Two rows cause most of the trouble. The length is not a declaration, it is an observation: a file that is two kilobytes short looks like a valid file that is two kilobytes shorter. And a gap in the image is silently filled with zeros, which on this architecture is a legal instruction and therefore does not announce itself.
Three ways a binary is wrong without looking wrong
The first is truncation. A read that stopped early, a transfer that dropped its last block, or a buffer that was sized for the smaller memory class produces a file whose end is missing. On this device the missing end contains the vector table, so the file survives a checksum and fails at the first reset.
The second is padding. A tool that sized the output to the larger memory class, or that padded to a round number, produces a file whose first bytes are right and whose tail is zeros. The vector area reads as zero, which is a plausible-looking address — the start of the flash — and will send a rebuilt device into the start of its own code with no initialisation.
The third is a base offset. A binary has no addresses, so the implied base is a convention. If the read started at an offset other than zero, everything is displaced and the vector table lands in the middle of the file rather than at its end. This is the only one of the three that is easy to spot, because the file length no longer matches the expected array size.
The five-second proof
Read the last four bytes as a thirty-two-bit little-endian value and as a thirty-two-bit big-endian value.
One of the two will be an address inside the flash region — a small number, aligned, and well below the option-setting area at the top of the map. The other will be a value in the hundreds of millions, which is not an address any code can execute from. That comparison proves the base, the endianness and the completeness of the file in one step, because truncation moves the vector out of the last four bytes and padding replaces it with zeros.
Do the same with the exception vectors immediately below. On this architecture those entries are handler addresses, tightly clustered, and a block of four or five that all decode to plausible aligned values in the same region is strong evidence that the image is intact and correctly oriented.
When a binary is the right deliverable
A binary is right when the thing that will consume it expects bytes at an address. Production programmers, some bootloader upload paths and most test fixtures work that way.
A binary is wrong as the only deliverable, because it cannot describe itself. The professional pattern is to deliver both: the binary for the tools that want it, and an addressed file for the people who will inspect it, generated from the same read rather than from two separate reads. The pair then proves itself, because converting one to the other is a lossless operation that can be diffed.
There is an exception worth naming. When the customer’s toolchain is old enough that its binary reader assumes a particular base address, a binary delivered alongside a note stating that base is more useful than a modern format the tool cannot open. That is a support decision rather than a technical one, and it is worth asking about before delivery rather than after.
Recording what the file cannot say
Three facts belong in the delivery note for a binary on this part, and none of them can be recovered from the file later.
The base address, stated explicitly, because it is the one thing a binary cannot express.
The endianness of the original design, because a correct set of bytes decodes into two different programs depending on the answer.
The expected length, with the actual length next to it, so that a future reader can tell a truncated file from a complete one without the datasheet.
For the addressed container that solves all three of those problems at once, R5F562T7EDFF heximal covers record formats. For the byte-order question that the binary cannot answer, R5F562T7BDFF code takes it apart. And for a full bundle rather than a single file, R5F562T6DDFF firmware shows what else travels with the image.
FAQ
Can a binary be converted back to addresses? Only with the base address, which has to come from outside the file. With it, conversion is exact.
Does a zero-filled tail mean the read failed? Not necessarily. It can mean the file was padded to the larger memory class. The vector check distinguishes padding from a genuine empty region.
Is a binary smaller than the array ever correct? Yes, when the design’s code does not use the whole flash. What must be stated is the base and the length actually used, not the length the device could hold.
The short version
A binary says nothing, so everything it omits has to be written down: base, byte order, expected length. The reset vector at the top of the map proves the first and the second, and the file size is only evidence when compared against the memory class. Deliver the binary and an addressed file from the same read, and neither can lie about the other.
ATmega169PV: Display Fuses, Bias, and a Screen That Stays Dark
A microcontroller that drives glass has an unusual problem: the display needs a clock of its own, a bias voltage, and a contrast setting, and all three have to be right before anything appears. None of them is in the program.
They are fuse settings. That makes a device with a perfect flash image capable of showing nothing at all, and it makes the fuse byte the first thing to read on any display product that arrives dead but functional.
What the display fuses control
| Setting | Effect | Symptom when wrong |
|---|---|---|
| Driver clock source | Waveform timing | Flicker, or nothing |
| Bias | Voltage levels per phase | Faint, patchy, or invisible |
| Initial contrast | Segment drive strength | Readable in one light, not another |
| Multiplex ratio | Number of backplanes | Ghosting, or half the display blank |
The fourth row is the one that produces the most confusing result. A multiplex setting that does not match the glass produces a display where some segments light and others do not, and that pattern looks like a firmware bug in the segment table. It is not: the table is fine and the waveform is driving the wrong number of common lines.
Why the fuses are outside the image
Fuses are configuration, not content. They are read and written through dedicated commands, they are not part of the flash address space, and no hex file of the program contains them.
So a recovery that produces a flash image and stops there has produced the program and omitted the settings that make the display work. Restoring that image onto a blank part with default fuses yields a device that runs and shows nothing.
That is a specific and common failure, and it is entirely avoidable: read the fuse byte at the same time as the flash and keep them together as one artefact.
Reading the display configuration out of the code
The firmware still has work to do, and it leaves traces:
- Enabling the driver and selecting the multiplex ratio at start-up.
- Writing an initial contrast value, which may then be adjusted.
- A periodic interrupt that refreshes the display, or a write to a frame-complete flag.
- Temperature compensation, if the product is careful, which reads a sensor and adjusts contrast.
That last item is worth looking for. A firmware that compensates contrast for temperature is a firmware written by someone who saw the product fail in the field, and the compensation curve is a design decision stored in the image.
Why the P and V suffixes matter here
The picoPower die changed the display driver along with everything else, and the extended low-voltage range interacts with contrast: at a lower supply there is less voltage headroom for the bias levels, and the same contrast setting produces a dimmer display.
A product specified across a wide supply range therefore has to adjust contrast with voltage, not just temperature. Firmware that does not is firmware that was validated at one rail.
Reading order for a display device
- Signature, fuses, lock byte — the display fuses first among them.
- Array read, verified.
- Initialisation: driver enable, multiplex, contrast.
- Refresh path: interrupt or polling, and its period.
- Segment table and its index.
Step 5 is the deliverable, and it is verifiable against the glass. If the table reconstructed from the image renders the product’s actual display, the analysis is correct — a property no other kind of product offers so directly.
Related notes
- ATmega169PA and the segment map — the table itself, in detail.
- ATmega169A and the binary image — finding it in a flat file.
- ATmega8A and fuse dependence — the same principle without a display.
FAQ
Can the display work without the driver fuses being set? No. The waveform and bias come from those settings.
Are display fuses readable on a locked part? Yes. Fuses are outside the lock bit mechanism.
Why do some segments not light? Usually a multiplex ratio that does not match the glass, not a table error.
Does contrast need temperature compensation? For a product used across a range, yes, and careful firmware does it.
Conclusion
On a display product, the fuse byte is as important as the image. Driver clock, bias, contrast and multiplex live outside the flash and outside every hex file, and a wrong one turns a perfect recovery into a dark screen. Reading them together with the code is what makes the result reproducible.