Archive for the ‘Break IC’ Category
 Attack STM32F038E6 Microprocessor Secured Memory
 April 29th, 2021 |
 Author:
Attack STM32F038E6 Microprocessor Secured Memory and extract locked firmware from mcu stm32f038e6 flash memory, rewrite copied heximal file to new microcontroller stm32f038e6 for processor cloning;
The ARM® Cortex®-M0 is a generation of ARM 32-bit RISC processors for embedded systems. It has been developed to provide a low-cost platform that meets the needs of MCU implementation, with a reduced pin count and low-power consumption, while delivering outstanding computational performance and an advanced system response to interrupts.
атаковать защищенную память микропроцессора STM32F038E6 и извлечь заблокированную прошивку из флэш-памяти MCU STM32F038E6, перезаписать скопированный шестигранный файл на новый микроконтроллер STM32F038E6 для клонирования процессора;
The ARM® Cortex®-M0 processors feature exceptional code-efficiency, delivering the high performance expected from an ARM core, with memory sizes usually associated with 8- and 16-bit devices when breaking stm32f030r8 microprocesor locked bits. The STM32F038x6 devices embed ARM core and are compatible with all ARM tools and software.
The device has the following features:
- 4 Kbytes of embedded SRAM accessed (read/write) at CPU clock speed with 0 wait states and featuring embedded parity checking with exception generation for fail-critical applications.
- The non-volatile memory is divided into two arrays:
- 32 Kbytes of embedded Flash memory for programs and data
- Option bytes
- The non-volatile memory is divided into two arrays:
The option bytes are used to write-protect the memory (with 4 KB granularity) and/or readout-protect the whole memory with the following options:
- Level 0: no readout protection
- Level 1: memory readout protection, the Flash memory cannot be read from or written to if either debug features are connected or boot in RAM is selected
- Level 2: chip readout protection, debug features (Cortex®-M0 serial wire) and boot in RAM selection disabled which can be attacked by readout protection removal technique;
 Posted in

Break STM32F038C6 MCU Locked Flash Memory
Break STM32F038C6 MCU Locked Flash Memory protection and readout embedded heximal file from microprocessor stm32f038c6 memory, the fuse bit of stm32f038c6 will be unlocked in order to extract source code;
The STM32F038x6 microcontrollers incorporate the high-performance ARM® Cortex®-M0 32-bit RISC core operating at up to 48 MHz frequency, high-speed embedded memories (32 Kbytes of Flash memory and 4 Kbytes of SRAM), and an extensive range of enhanced peripherals and I/Os.
All devices offer standard communication interfaces (one I2C, one SPI/ I2S and one USART), one 12-bit ADC, five 16-bit timers, one 32-bit timer and an advanced-control PWM timer when recover flash firmware from stm32f031e6 microcontroller.
сломать защиту заблокированной флэш-памяти STM32F038C6 MCU и считывание встроенного шестнадцатеричного файла из памяти микропроцессора STM32F038C6, бит предохранителя STM32F038C6 будет разблокирован для извлечения исходного кода;
The STM32F038x6 microcontrollers operate in the -40 to +85 °C and -40 to +105 °C temperature ranges at a 1.8 V ± 8% power supply. A comprehensive set of power-saving modes allows the design of low-power applications.
The STM32F038x6 microcontrollers include devices in five different packages ranging from 20 pins to 48 pins with a die form also available upon request. Depending on the device chosen, different sets of peripherals are included.
These features make the STM32F038x6 microcontrollers suitable for a wide range of applications such as application control and user interfaces, hand-held equipment in order to reverse engineering mcu stm32f031f4 microprocessor source code, A/V receivers and digital TV, PC peripherals, gaming and GPS platforms, industrial applications, PLCs, inverters, printers, scanners, alarm systems, video intercoms and HVACs.
Break ARM Microprocessor STM32F030CC Flash Memory
Break ARM Microprocessor STM32F030CC Flash Memory and clone embedded heximal from mcu stm32f030cc flash memory, the readout protection will be disable and source code of microcontroller stm32f030cc will be extracted;
The internal voltage reference (VREFINT) provides a stable (bandgap) voltage output for the ADC. VREFINT is internally connected to the ADC_IN17 input channel. The precise voltage of VREFINT is individually measured for each part by ST during production test and stored in the system memory area. It is accessible in read-only mode.
The advanced-control timer (TIM1) can be seen as a three-phase PWM multiplexed on six channels to attack secured cpu stm32f070rb locked bit. It has complementary PWM outputs with programmable inserted dead times. It can also be seen as a complete general-purpose timer. The four independent channels can be used for:
एआरएम माइक्रोप्रोसेसर एसटीएम 32 एफ 030 सीसी फ्लैश मेमोरी और एमसीयू एसटीएम 32 एफ 030 सीसी फ्लैश मेमोरी से क्लोन एम्बेडेड हेक्सिमल को तोड़ें, रीडआउट सुरक्षा अक्षम हो जाएगी और माइक्रोकंट्रोलर एसटीएम 32 एफ 030 सीसी का स्रोत कोड निकाला जाएगा;
- Input capture
- Output compare
- PWM generation (edge or center-aligned modes)
- One-pulse mode output
If configured as a standard 16-bit timer, it has the same features as the TIMx timer. If configured as the 16-bit PWM generator, it has full modulation capability (0-100%).
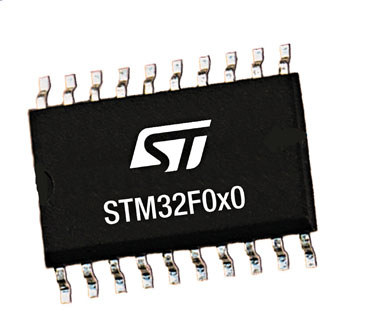
The counter can be frozen in debug mode. Many features are shared with those of the standard timers which have the same architecture. The advanced control timer can therefore work together with the other timers via the Timer Link feature for synchronization or event chaining by breaking stm32f030r8 microprocessor locked bits.
ARM MCU STM32F031C4 Flash Memory Breaking
ARM MCU STM32F031C4 Flash Memory Breaking is a process to crack microprocessor stm32f031c4 flash memory security fuse bit, and then extract flash binary from stm32f031c4 arm microcontroller;
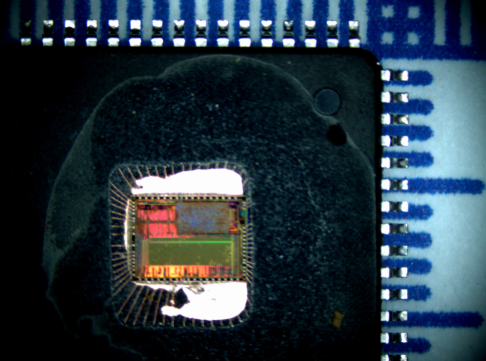
The STM32F031x4/x6 microcontrollers incorporate the high-performance ARM® Cortex®- M0 32-bit RISC core operating at up to 48 MHz frequency, high-speed embedded memories (up to 32 Kbytes of Flash memory and 4 Kbytes of SRAM) to break stm32f030r8 mcu locked bits, and an extensive range of enhanced peripherals and I/Os. All devices offer standard communication interfaces (one I2C, one SPI/ I2S and one USART), one 12-bit ADC, five 16-bit timers, one 32-bit timer and an advanced-control PWM timer.
The STM32F031x4/x6 microcontrollers operate in the -40 to +85 °C and -40 to +105 °C temperature ranges, from a 2.0 to 3.6 V power supply. A comprehensive set of power-saving modes allows the design of low-power applications.
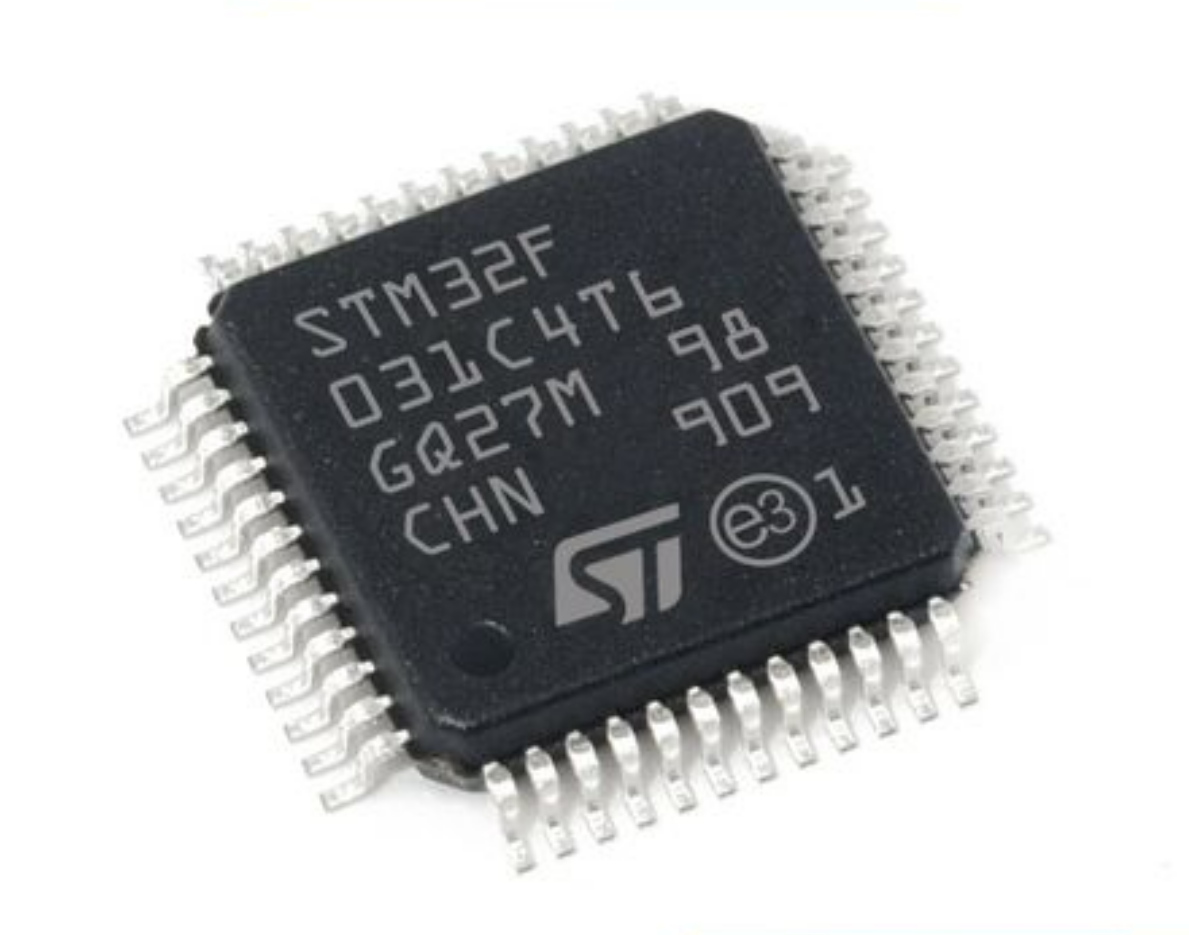
एआरएम एमसीयू एसटीएम 32 एफ 031 सी 4 फ्लैश मेमोरी ब्रेकिंग माइक्रोप्रोसेसर एसटीएम 32 एफ 031 सी 4 फ्लैश मेमोरी सिक्योरिटी फ्यूज बिट को क्रैक करने की एक प्रक्रिया है, और फिर एसटीएम 32 एफ 031 सी 4 आर्म माइक्रोकंट्रोलर से फ्लैश बाइनरी निकालने के लिए;
The STM32F031x4/x6 microcontrollers include devices in six different packages ranging from 20 pins to 48 pins with a die form also available upon request. Depending on the device chosen, different sets of peripherals are included when attacking stm32f070rb arm mcu locked bits.
These features make the STM32F031x4/x6 microcontrollers suitable for a wide range of applications such as application control and user interfaces, hand-held equipment, A/V receivers and digital TV, PC peripherals, gaming and GPS platforms, industrial applications, PLCs, inverters, printers, scanners, alarm systems, video intercoms and HVACs.
Break ARM STM32F030R8 Microprocessor Locked Bits
The stm32f030r8 is an Arm Cortex-M0-based mcu from STMicroelectronics, designed for cost-sensitive embedded applications requiring reliable control, low power consumption, integrated peripherals, and straightforward real-time processing. Although the requested subject uses the term microprocessor, stm32f030r8 is more precisely classified as a microcontroller because its processing core, memory, timers, communication interfaces, and other peripherals are integrated into a single device. The stm32f030r8 can be found in industrial controllers, consumer electronics, smart appliances, instrumentation, lighting equipment, motor-control products, building automation, power-management equipment, and compact embedded systems.
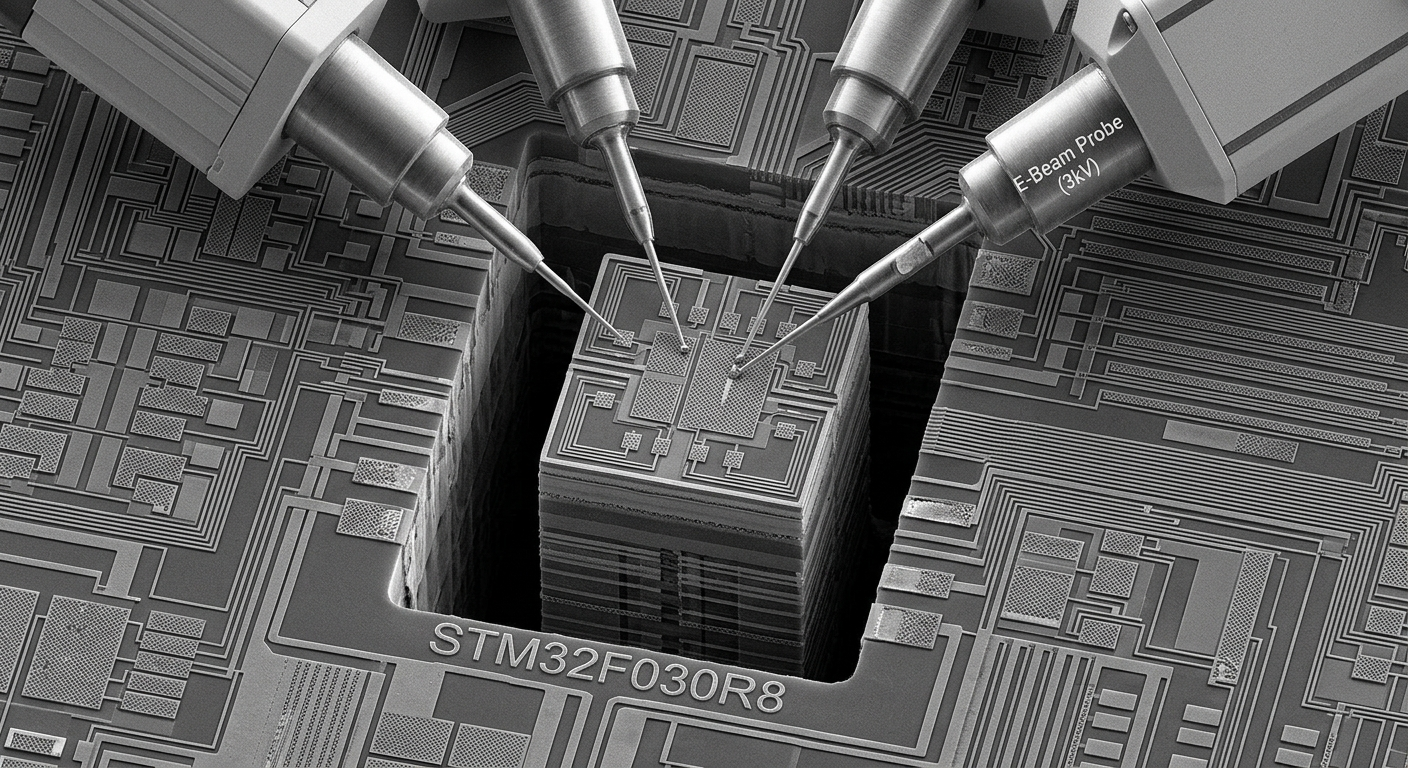
In these products, an embedded firmware program may contain important control logic, calibration data, configuration information, and executable binary information stored in internal flash memory. When the original development file, source project, or firmware archive is unavailable, our authorized break arm stm32f030r8 microprocessor locked bits service provides an engineering-oriented approach to assessing whether valuable program information can be recovered from an existing stm32f030r8 device.
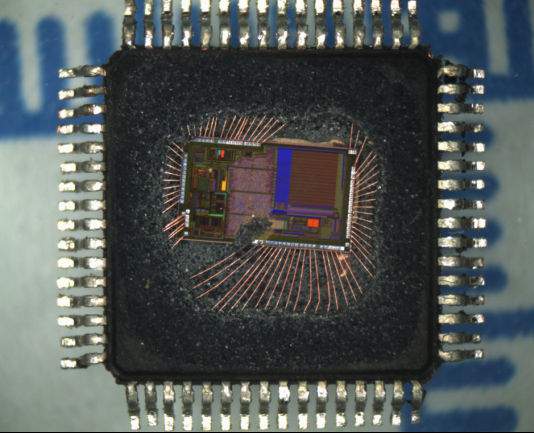
System clock selection is performed on startup, however the internal RC 8 MHz oscillator is selected as default CPU clock on reset. An external 4-32 MHz clock can be selected, in which case it is monitored for failure.
The objective is not simply to attack, break, or hack a device, but to investigate a customer’s authorized hardware and determine whether its embedded information can be preserved. For a stm32f030r8, engineers first examine the physical condition, device configuration, surrounding PCB circuitry, available documentation, and relevant security settings.
Particular attention may be given to readout-protection configuration and other protective, protected, or locked states that affect access to embedded flash memory. Depending on the device condition and project requirements, laboratory-level semiconductor investigation may also be considered, including carefully controlled decapsulate analysis when technically justified and legally authorized. The objective is to retrieve useful firmware information and decode recovered binary or heximal records into an engineering-readable form where feasible.
The recovered material may include program data, memory contents, configuration information, or other useful file and archive resources. While customers may describe the requirement using terms such as attack, break, or hack, our service is focused on authorized recovery, preservation, and engineering analysis rather than providing instructions for defeating security mechanisms. The stm32f030r8 recovery process is therefore evaluated individually, because the achievable result depends on the specific protection configuration, physical condition, memory architecture, and available evidence.
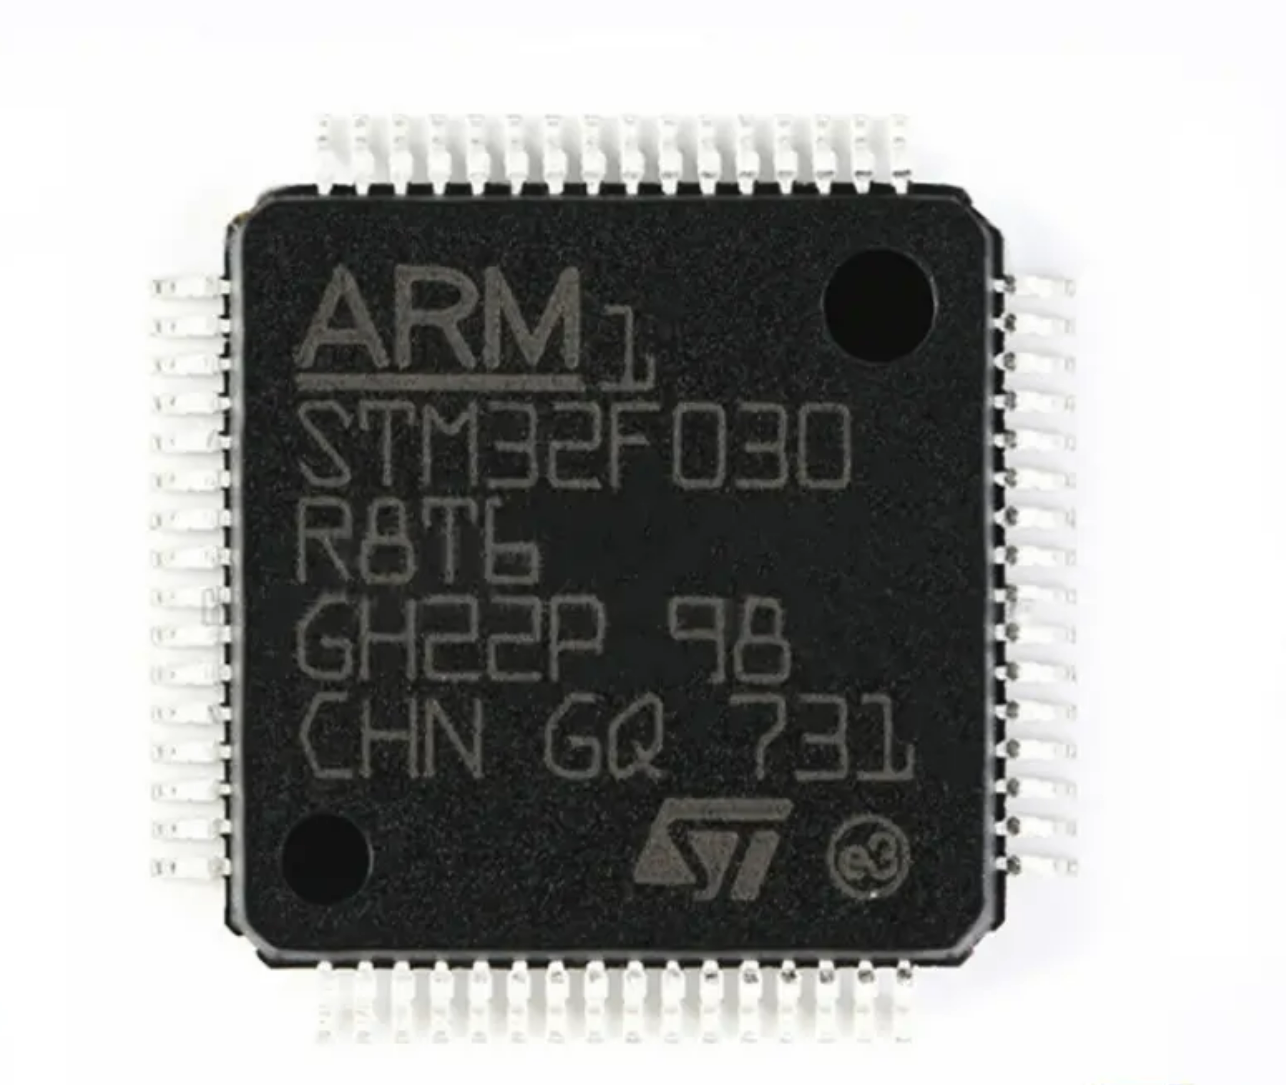
Several prescalers allow the application to configure the frequency of the AHB and the APB domains. The maximum frequency of the AHB and the APB domains is 48 MHz.
Another important consideration when working with the stm32f030r8 is the difference between recovered machine code and the original development project. A recovered binary or heximal image is not normally equivalent to the original source code. The source project may contain comments, variable names, build configurations, libraries, and other development information that cannot automatically be reconstructed from firmware.
Our engineering analysis can instead correlate the recovered program with the target circuit’s functions, interfaces, timing behavior, peripheral usage, and application requirements. This can help determine how particular firmware sections relate to the embedded system and whether the recovered information can support further development. Where technically appropriate, semiconductor-level investigation can complement conventional firmware analysis.
Similar recovery concepts may also be relevant when customers have legacy products involving dsp, mcu, microcontroller, or microprocessor devices, including projects whose historical documentation incorrectly identifies a component as a texas instrument device. The purpose of examining a stm32f030r8 is ultimately to preserve authentic engineering information rather than merely produce an unexplained memory dump.
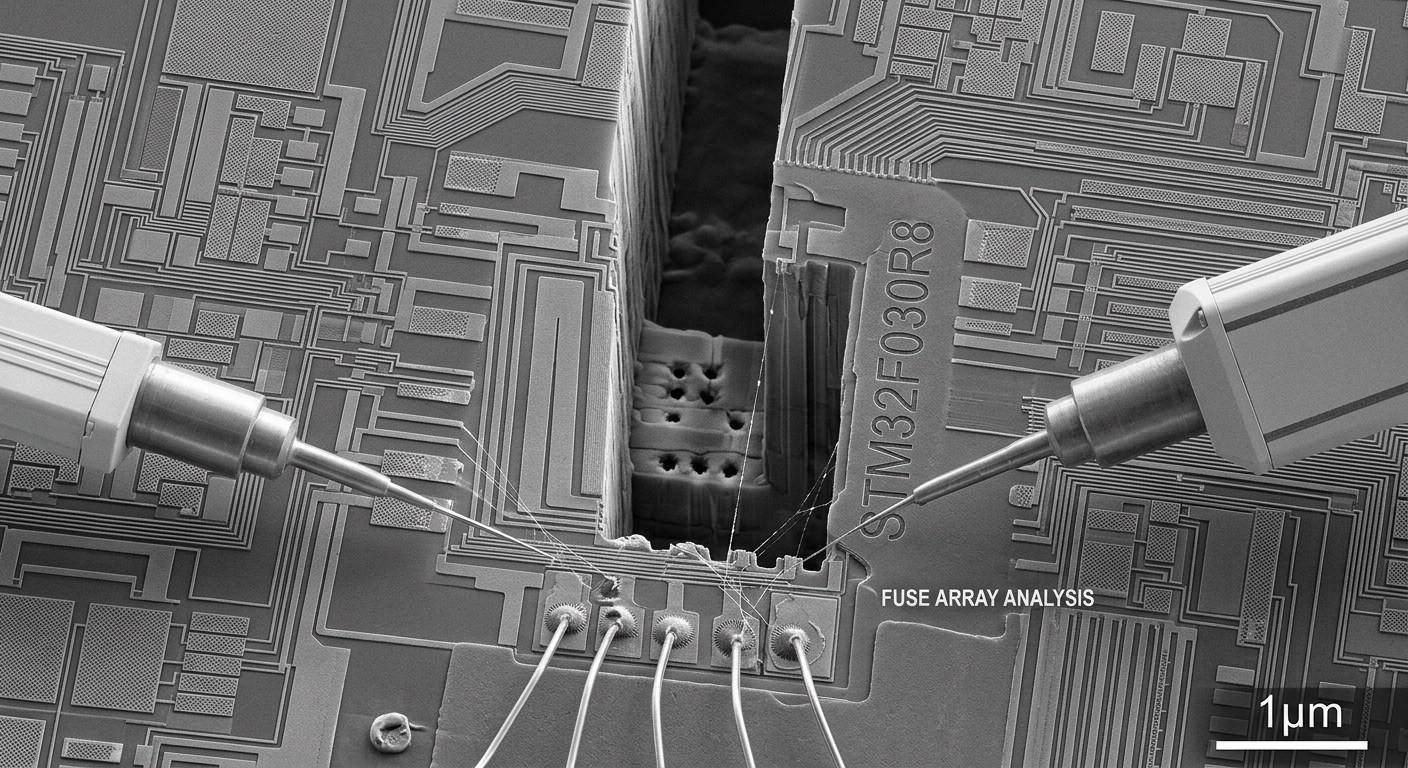
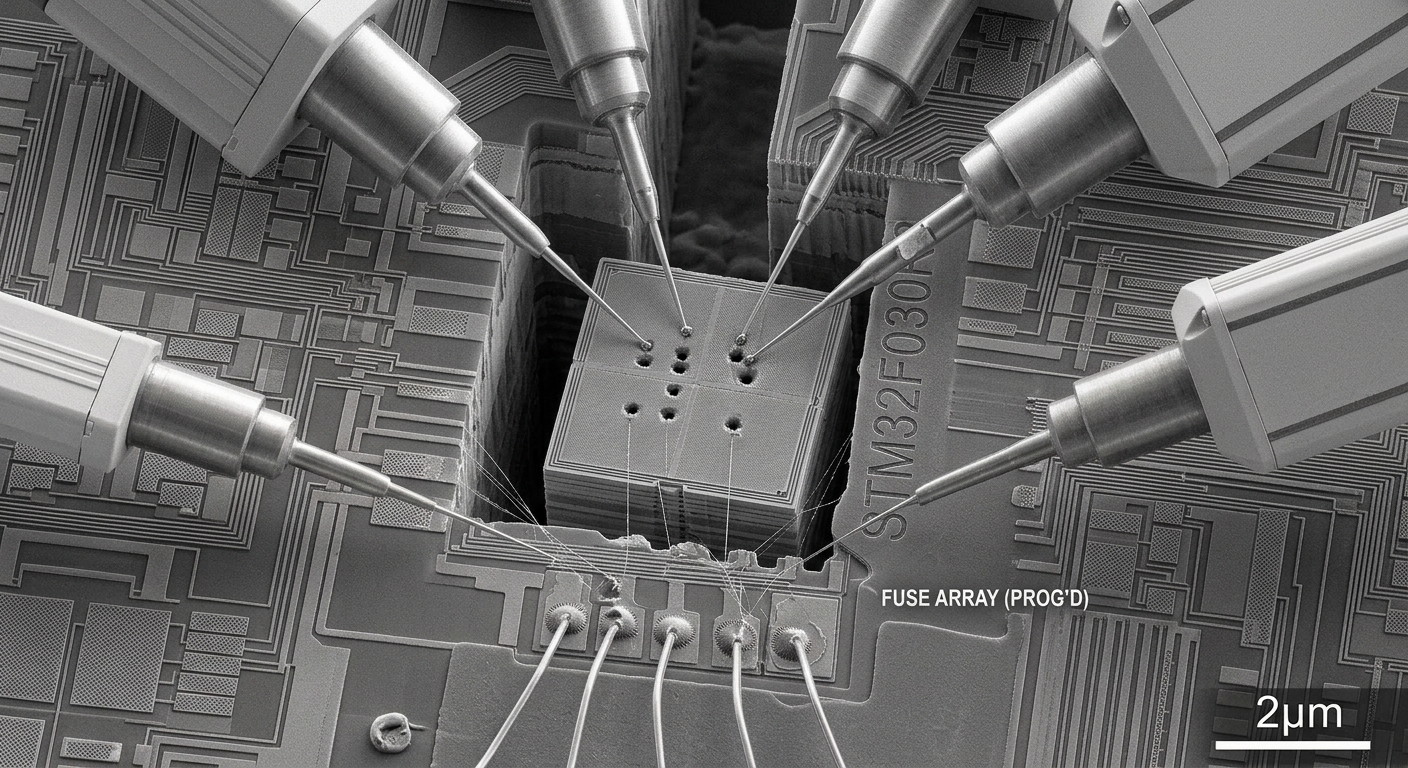
For equipment manufacturers, repair organizations, engineering laboratories, and owners of discontinued products, recovering the embedded firmware from a stm32f030r8 can provide significant lifecycle value. Recovered flash information, validated binary records, configuration data, and organized file or archive materials can assist with troubleshooting, replacement-board development, functional verification, product migration, and long-term maintenance.
In appropriate authorized projects, recovered firmware information may also support controlled efforts to clone or duplicate an existing hardware platform for engineering evaluation, compatibility testing, or manufacturing continuity. This is particularly useful when the original programmer, firmware source code, or development archive has been lost but functioning equipment remains available.
By combining embedded-system analysis, firmware examination, semiconductor investigation, and practical reverse-engineering experience, our service provides a structured way to investigate the stm32f030r8, understand its locked configuration, and recover whatever legitimate engineering information remains technically accessible. For customers dealing with protected or discontinued embedded equipment, the stm32f030r8 can therefore become the starting point for firmware preservation, repair, redesign, and continued product support rather than forcing an entire control system to be recreated from scratch.
Attack ARM STM32F030C8 Microcontroller Readout Protection
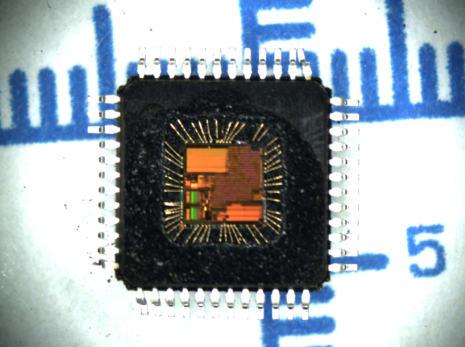
Attack ARM STM32F030C8 Microcontroller Readout Protection to be able to clone the embedded firmware from mcu stm32f030c8 flash memory, and then copy heximal to new microprocessor stm32f030c8 for functions replication;
The STM32F030x4/x6/x8/xC microcontrollers support three low-power modes to achieve the best compromise between low power consumption, short startup time and available wakeup sources:
· Sleep mode
In Sleep mode, only the CPU is stopped. All peripherals continue to operate and can wake up the CPU when an interrupt/event occurs.
· Stop mode
Stop mode achieves very low power consumption while retaining the content of SRAM and registers. All clocks in the 1.8 V domain are stopped, the PLL in the process of cracking stm32f071vc mcu protection system, the HSI RC and the HSE crystal oscillators are disabled. The voltage regulator can also be put either in normal or in low power mode.
ataque Protección de lectura del microcontrolador ARM STM32F030C8 para poder clonar el firmware integrado de la memoria flash MCU STM32F030C8 y luego copiar hexamal al nuevo microprocesador STM32F030C8 para la replicación de funciones;
The device can be woken up from Stop mode by any of the EXTI lines. The EXTI line source can be one of the 16 external lines and RTC.
· Standby mode
The Standby mode is used to achieve the lowest power consumption. The internal voltage regulator is switched off so that the entire 1.8 V domain is powered off. The PLL, the HSI RC and the HSE crystal oscillators are also switched off. After entering Standby mode for the sake of attacking stm32f070rb arm mcu locked bit, SRAM and register contents are lost except for registers in the RTC domain and Standby circuitry. The device exits Standby mode when an external reset (NRST pin), an IWDG reset, a rising edge on the WKUP pins, or an RTC event occurs.
Break ARM STM32F072C8 Microcontroller Protection
Break ARM STM32F072C8 Microcontroller Protection over the flash memory, normally the fuse bit of MCU STM32F072C8 will be disable by processor cracking, and copy embedded heximal from flash memory of mcu stm32f072c8 to new MCU for cloning purpose;
System clock selection is performed on startup, however the internal RC 8 MHz oscillator is selected as default CPU clock on reset. An external 4-32 MHz clock can be selected, in which case it is monitored for failure. If failure is detected, the system automatically switches
back to the internal RC oscillator. A software interrupt is generated if enabled. Similarly, full interrupt management of the PLL clock entry is available when necessary (for example on failure of an indirectly used external crystal, resonator or oscillator).
Several prescalers allow the application to configure the frequency of the AHB and the APB domains. The maximum frequency of the AHB and the APB domains is 48 MHz.
Additionally, also the internal RC 48 MHz oscillator can be selected for system clock or PLL input source. This oscillator can be automatically fine-trimmed by the means of the CRS peripheral using the external synchronization.
ARM Microcomputer STM32F072R8 Readout Protection Breaking
ARM Microcomputer STM32F072R8 Readout Protection Breaking can unlock the fuse bit applied over microcontroller stm32f072r8 flash memory, and then readout embedded heximal from stm32f072r8 mcu;
The STM32F072x8/xB microcontrollers include devices in seven different packages ranging from 48 pins to 100 pins with a die form also available upon request. Depending on the device chosen, different sets of peripherals are included which will bring more difficult for recover stm32f051c4 microprocessor flash binary.
La rottura della protezione di lettura del microcomputer ARM STM32F072R8 può sbloccare la punta del fusibile applicata sulla memoria flash del microcontrollore stm32f072r8 e quindi leggere l’heximal incorporato dall’MCU stm32f072r8;
These features make the STM32F072x8/xB microcontrollers suitable for a wide range of applications such as application control and user interfaces, hand-held equipment, A/V receivers and digital TV, PC peripherals, gaming and GPS platforms, industrial applications, PLCs, inverters, printers, scanners, alarm systems, video intercoms and HVACs.
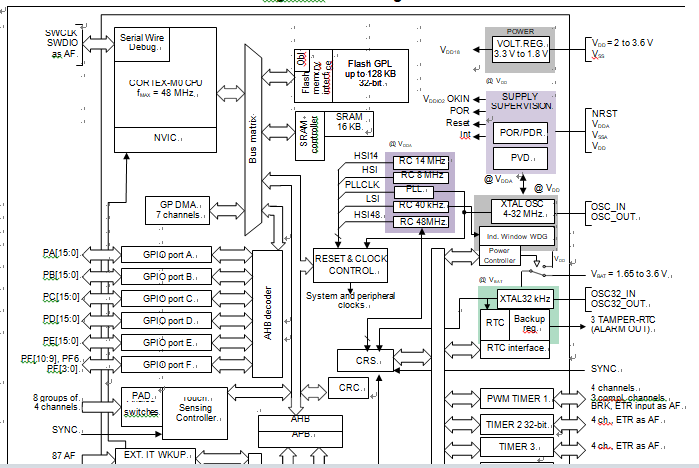
The Arm® Cortex®-M0 is a generation of Arm 32-bit RISC processors for embedded systems. It has been developed to provide a low-cost platform that meets the needs of MCU implementation, with a reduced pin count and low-power consumption, while delivering outstanding computational performance and an advanced system response to interrupts.
The Arm® Cortex®-M0 processors feature exceptional code-efficiency, delivering the high performance expected from an Arm core, with memory sizes usually associated with 8- and 16-bit devices. The STM32F072x8/xB devices embed Arm core and are compatible with all Arm tools and software which is suitable for breaking stm32f071rb microcontroller locked bits protection over flash memory content.
ARM STM32F071RB Microcontroller Locked Bit Breaking
After ARM STM32F071RB Microcontroller Locked Bit Breaking has been completed, the stm32f071rb chip firmware can be decoded and then clone binary content to new microprocessor;
The current consumption of the I/O system has two components: static and dynamic.
I/O static current consumption
All the I/Os used as inputs with pull-up generate current consumption when the pin is externally held low. The value of this current consumption can be simply computed by using the pull-up/pull-down resistors values given in Table 53: I/O static characteristics.
For the output pins, any external pull-down or external load must also be considered to estimate the current consumption. Additional I/O current consumption is due to I/Os configured as inputs if an intermediate voltage level is externally applied to recover stm32f051c4 mcu flash binary file.
dopo che il bit breaking bloccato del microcontrollore ARM STM32F071RB è stato completato, il firmware del chip STM32F071RB può essere decodificato e quindi clonare il contenuto binario sul nuovo microprocessore;
This current consumption is caused by the input Schmitt trigger circuits used to discriminate the input value. Unless this specific configuration is required by the application, this supply current consumption can be avoided by configuring these I/Os in analog mode. This is notably the case of ADC input pins which should be configured as analog inputs.
Any floating input pin can also settle to an intermediate voltage level or switch inadvertently, as a result of external electromagnetic noise. To avoid current consumption related to floating pins, they must either be configured in analog mode for the sake of restore microprocessor stm32f051c6 flash heximal, or forced internally to a definite digital value. This can be done either by using pull-up/down resistors or by configuring the pins in output mode.
Hack ARM STM32F071VB MCU Flash Memory Protection
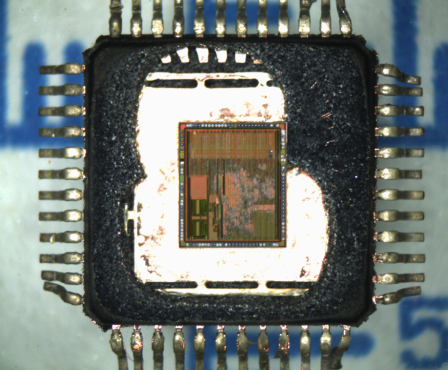
Hack ARM STM32F071VB MCU Flash Memory Protection needs to apply an invasive cracking method normally starts from decapsulate the silicon package over microcontroller stm32f071vb processor, and then readout the unlocked microprocessor stm32f071vb flash code directly;
Up to two I2C interfaces (I2C1 and I2C2) can operate in multimaster or slave modes. Both can support Standard mode (up to 100 kbit/s) or Fast mode (up to 400 kbit/s). I2C1 also supports Fast Mode Plus (up to 1 Mbit/s), with 20 mA output drive. Both support 7-bit and 10-bit addressing modes, multiple 7-bit slave addresses (two addresses, one with configurable mask). They also include programmable analog and digital noise filters.
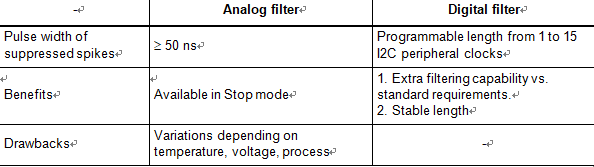
In addition, I2C1 provides hardware support for SMBUS 2.0 and PMBUS 1.1: ARP capability, Host notify protocol, hardware CRC (PEC) generation/verification by recover flash data from locked stm32f071rb mcu, timeouts verifications and ALERT protocol management. The I2C interfaces can be served by the DMA controller.
hack ARM STM32F071VB La protezione della memoria flash MCU deve applicare un metodo di cracking invasivo che normalmente inizia dal decapsulare il pacchetto di silicio sul processore STM32F071VB del microcontrollore e quindi leggere direttamente il codice flash del microprocessore sbloccato STM32F071VB;
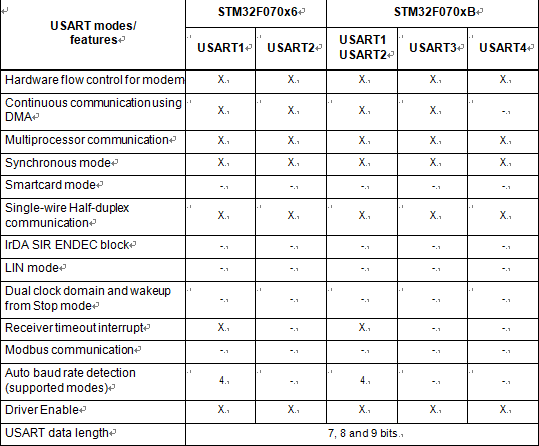
The device embeds up to four universal synchronous/asynchronous receivers/transmitters that communicate at speeds of up to 6 Mbit/s. belwo Table gives an overview of features as implemented on the available USART interfaces. All USART interfaces can be served by the DMA controller.